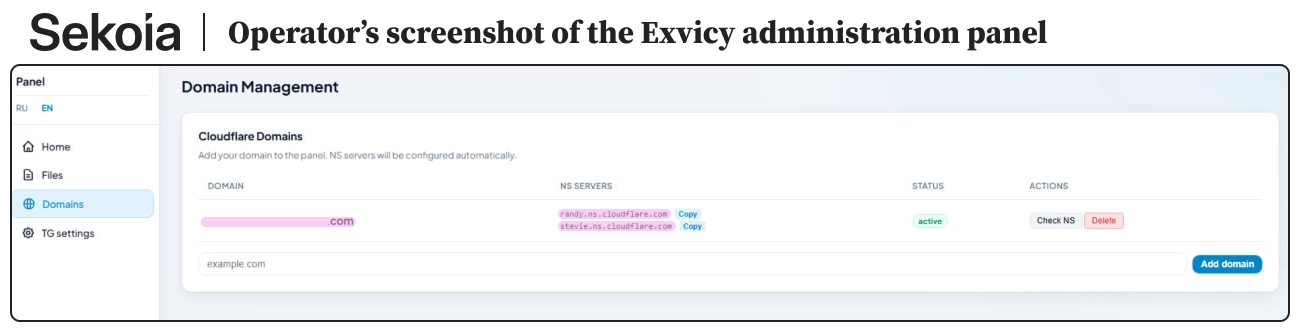
Sekoia TDR uncovered Exvicy, a ClickFix Malware-as-a-Service framework advertised on Exploit.IN by the threat actor @Exvicy and used to impersonate Cloudflare Turnstile verification pages on compromised WordPress sites. The investigation linked Exvicy to active operator infrastructure, PowerShell downloaders, and code reuse from ErrTraffic, indicating Exvicy is a copycat framework built from the same client-side codebase. #Exvicy #ErrTraffic #Exploit.IN #CloudflareTurnstile #WordPress
Keypoints
- Exvicy was advertised on the Russian-speaking Exploit.IN forum as a ClickFix MaaS framework sold by the threat actor @Exvicy.
- The operator initially priced the service at $1,200 per month and later raised it to $2,000 per month, citing daily detections and maintenance needs.
- Researchers pivoted from a screenshot in the forum post to identify Exvicy-related infrastructure, including domains, IP addresses, and administration panels.
- Exvicy pages impersonate Cloudflare Turnstile verification challenges and use the Windows Run dialog to trick victims into executing malicious commands.
- The framework injects obfuscated JavaScript into compromised WordPress sites, which loads ClickFix HTML and communicates with Exvicy C2 servers.
- Analysts found a malicious PowerShell downloader hosted on Exvicy infrastructure that retrieves an MSI installer and reports installation status to C2.
- Code comparison showed Exvicy reuses ErrTraffic JavaScript routines, supporting the assessment that Exvicy is a direct copycat of ErrTraffic.
MITRE Techniques
- [T1059.001] PowerShell – Used to download and execute a remote script from the ClickFix lure and malicious infrastructure (‘powershell … $a=irm …; $ExecutionContext.InvokeCommand.InvokeScript($a)’).
- [T1059.007] JavaScript – Used as the initial payload injected into compromised WordPress sites to deobfuscate and run the embedded ClickFix logic (‘This script contains a payload obfuscated via Base64 encoding and XOR encryption’).
- [T1189] Drive-by Compromise – Compromised WordPress sites were injected with Exvicy code so visitors were served malicious ClickFix pages (‘This script was injected into a compromised WordPress book promotion site’).
- [T1204.002] Malicious File Execution – Victims were instructed to press Win+R, paste, and run the malicious command in the Windows Run dialog (‘press “Win + R”, then “Ctrl + V”, followed by “Enter”’).
- [T1027] Obfuscated Files or Information – Both the injected JavaScript and embedded commands were heavily obfuscated using Base64, XOR, and randomized variable names (‘payload obfuscated via Base64 encoding and XOR encryption’).
- [T1105] Ingress Tool Transfer – The script downloaded secondary payloads and installers from remote infrastructure (‘retrieving an MSI installer from a Cloudflare R2 bucket’).
- [T1071.001] Web Protocols – Exvicy C2 communications used HTTP GET and POST requests to fetch HTML and exchange status data (‘/api.php?k=…’).
- [T1547] Boot or Logon Autostart Execution – Not observed as persistent host autostart, not applicable; no direct evidence in the article.
- [T1115] Clipboard Data – The lure copied a prebuilt PowerShell command to the clipboard for victim execution (‘copied to the user’s clipboard via the copyText JavaScript function’).
- [T1497.001] System Checks – The framework used anti-analysis / browser checks to avoid or detect debugging and execution anomalies (‘anti-analysis logic’).
Indicators of Compromise
- [Domains] Exvicy C2 and lure infrastructure domains – cloudflarecapcha.com, perfectverified.com, and other related domains such as cloudflare-check[.]net and kawaiininjaclub[.]cfd
- [IP addresses] Exvicy panels and C2 endpoints – 89.34.90[.]159, 89.34.90[.]150, and other infrastructure IPs such as 91.92.33[.]213 and 151.243.113[.]21
- [URLs / paths] Administration panels and lure endpoints – hxxps://us-addnewdevice[.]com/panel, hxxp://89.34.90[.]159/panel, and /embed/?embed=1&host=
- [Domains] ErrTraffic-related infrastructure referenced for comparison – analysis-id-lfg[.]info, verification-js-cdn[.]boats, and chatgpt-web[.]vip
- [Blockchain identifiers] ErrTraffic EtherHiding / DDR-related artifacts – contract address 0xB6bC9e1D0b2fB96Ab7C47E04Cb0BE477410bC1f2 and wallet 0xCaf2C54E400437da717cF215181B170F65187aBf
- [File names / payloads] Delivered or referenced payloads – putty.exe and MSI installer retrieved by the PowerShell downloader
Read more: https://www.sekoia.com/blog/exvicy-a-copycat-of-the-errtraffic-malware-distribution-framework