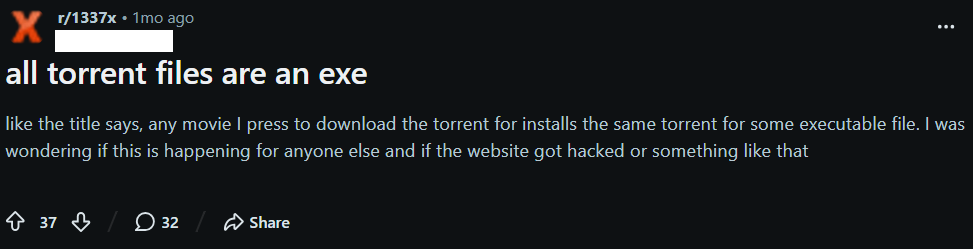
Researchers uncovered MovieReaper, a modular multi-stage crimeware campaign that spread through compromised torrent file storage and used a blockchain-based C2 layer for resilience. The operation affected hundreds of victims across multiple countries and relied on evasive loaders, Solana-based infrastructure, and a final file-management implant. #MovieReaper #Solana #deadhub.org #ittorrents.org
Keypoints
- MovieReaper was identified as a previously unknown modular, multi-stage malware framework distributed through compromised torrent tracker file storage.
- The campaign infected several hundred victims, including individuals and organizations across Europe, Asia, and Africa.
- Attackers did not compromise torrent trackers directly; they abused the public repository itorrents[.]org to serve malicious torrent files.
- The loader used anti-sandbox and anti-detection measures, including encrypted strings, PEB-based API resolution, and syscalls.
- Stage 2 used the Solana blockchain to retrieve the address of a second C2 server, increasing the resilience of the operation.
- Stage 3 performed UAC bypass, persistence, and masquerading by copying itself to %ProgramData%MicrosoftWindowsTelemetrymsedge.exe.
- The final implant provided a file manager with 21 commands for remote filesystem access, file manipulation, and preview-based exfiltration.
MITRE Techniques
- [T1027 ] Obfuscated Files or Information – The malware encrypted strings with a custom stream cipher to hinder analysis [‘strings are encrypted with a custom stream cipher’]
- [T1106 ] Native API – The loader avoided standard API calls and used direct syscall execution and ntdll internals [‘avoids making LoadLibrary and GetProcAddress calls’ and uses ‘raw NtProtectVirtualMemory syscall’]
- [T1055 ] Process Injection – The loader mapped shellcode into RWX memory and executed it in memory [‘map it into the RWX memory and execute’]
- [T1014 ] Rootkit – The loader rewrote exception handling and redirected control flow for stealthy execution [‘registers a vectored exception handler and rewrites the handler address in memory’]
- [T1620 ] Reflective Code Loading – Stage 2 parsed a COFF file, loaded it into memory, and executed its entry function [‘parses the COFF file and loads it to the memory, and executes the module_init function’]
- [T1548.002 ] Abuse Elevation Control Mechanism: Bypass User Account Control – Stage 3 achieved UAC bypass to continue execution [‘Stage 3 performs UAC Bypass’]
- [T1036 ] Masquerading – The malware renamed itself as a Windows telemetry component to blend in [‘masquerades the original binary as C:ProgramDataMicrosoftWindowsTelemetrymsedge.exe’]
- [T1071.001 ] Application Layer Protocol: Web Protocols – The malware communicated with C2 over HTTP/HTTPS for downloading payloads and command traffic [‘connects to it using plain HTTP’ and ‘communicates with its C2 server strictly through HTTPS’]
- [T1090 ] Proxy – The Solana blockchain was used as a distribution layer to relay the next-stage C2 address [‘uses the Solana blockchain network as a distribution layer of endpoints’]
- [T1105 ] Ingress Tool Transfer – The loader downloaded shellcode and later stages from remote servers [‘download the shellcode’ and ‘the next stage from the second C2 server’]
- [T1543.003 ] Create or Modify System Process: Windows Service – The malware established persistence and restarted itself as part of the staged execution [‘achieves persistence’ and ‘restarts itself’]
Indicators of Compromise
- [File hashes] Loader sample and related binaries – MD5 A0B13781EDD7CFDAB13D79AFFF3C83C1, SHA-256 4334BBAEA8DE33BF9D45E9B4E4E3BC24843F9FAFCAE492F11E2D4D33DBB4CDD5310CABAE3FBE6DB8742849B588093F9A0B13781EDD7CFDAB13D79AFFF3C83C170060341CAF3338697A7DDFE0FB62875AD4643EEA15AC286FA47D1131F9EF756D0B967571AC8A3863C7F324BF5BDE99CD88D550D0FB8E60CFFFF3EA61FF7A067
- [File paths] Persistence/masquerade location – %ProgramData%MicrosoftWindowsTelemetrymsedge.exe
- [Mutexes] Loader synchronization mutexes – GlobalE4AyDKzvEhe2hgAr, GlobalfnulSktzSqvVLXHU
- [Domains] First-stage C2 and related infrastructure – deadhub[.]org
- [IP addresses] First-stage and second-stage C2 endpoints – 193.23.118[.]155, 208.64.33[.]90, and 208.94.246[.]53
- [Domain/website] Compromised torrent source used to distribute malicious torrent files – itorrents[.]org
Read more: https://securelist.com/moviereaper-malware-torrent-odyssey-solana/121344/