ESET Research reports that FamousSparrow, a China-aligned APT, has shifted from SparrowDoor to a new modular C++ backdoor called SparroWocky and has used it against governmental targets across Latin America since at least August 2025. The new implant adds stealthy loading, persistence, and data theft features, while its infrastructure and targeting show a strong focus on regional government entities and open-source tooling integration. #FamousSparrow #SparrowDoor #SparroWocky #LatinAmerica
Keypoints
- FamousSparrow has replaced SparrowDoor with a new custom backdoor named SparroWocky.
- The group has been targeting governmental organizations across Latin America since at least August 2025.
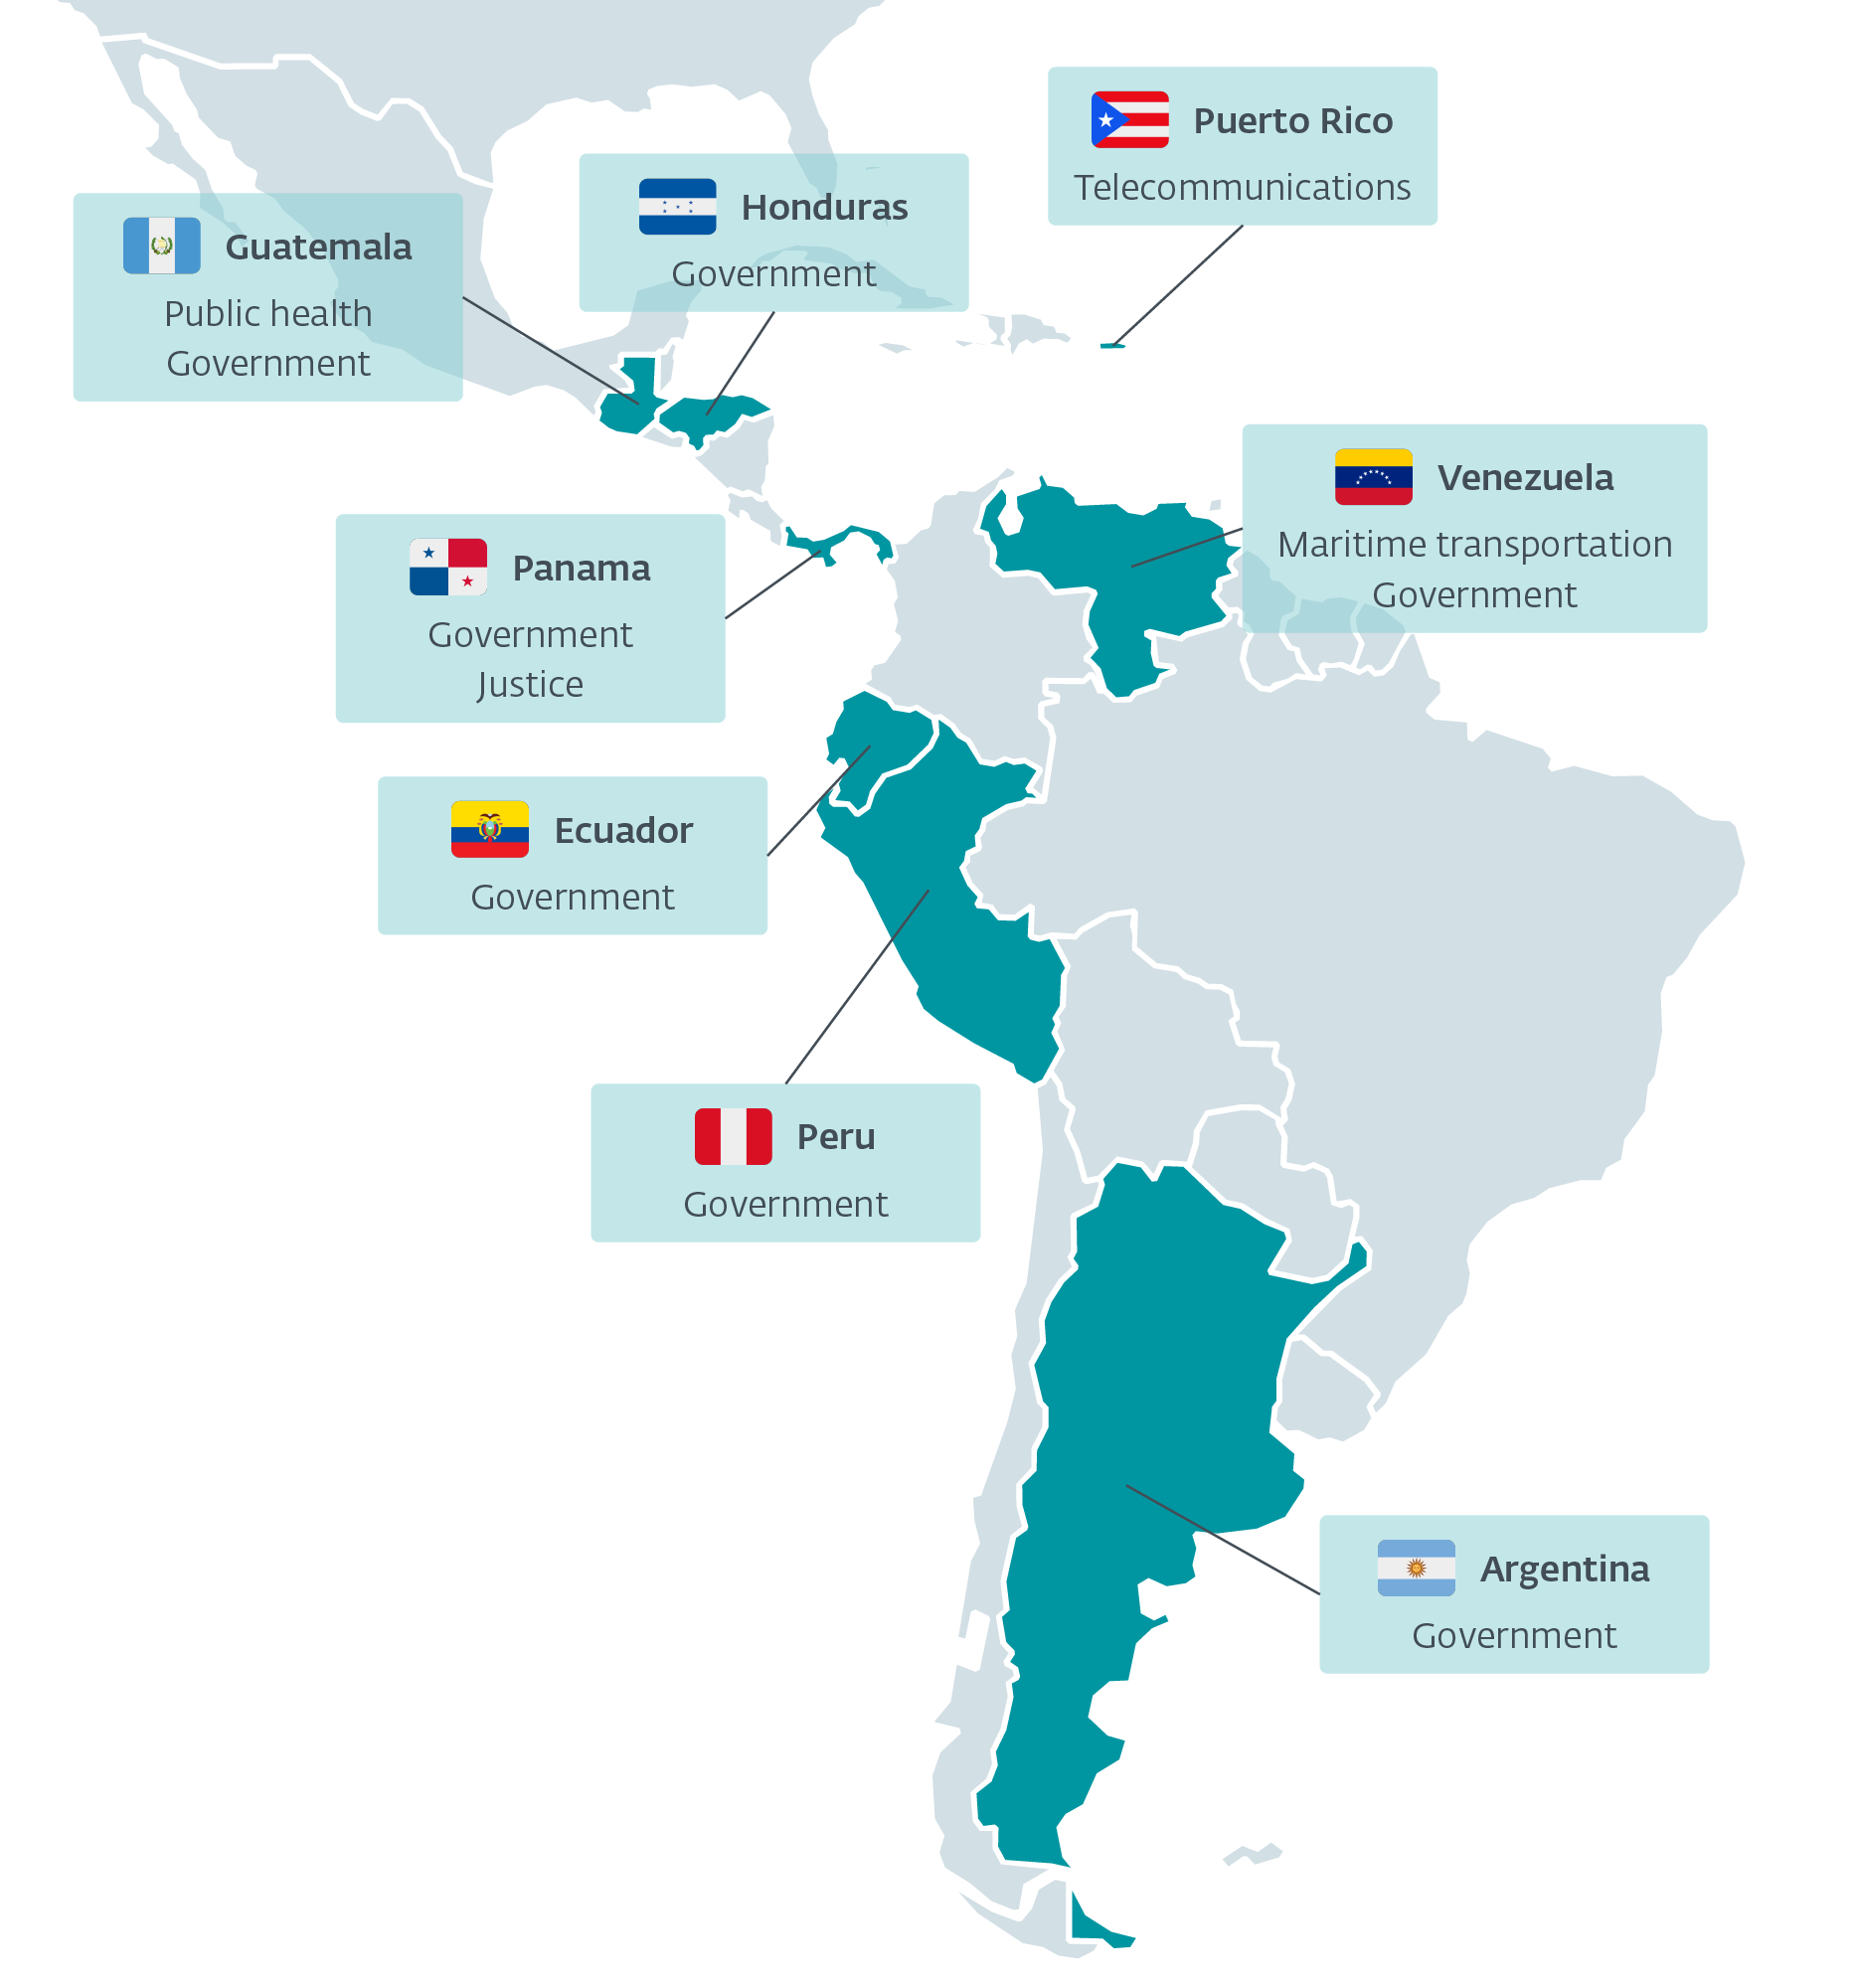
- ESET observed SparroWocky being used in multiple countries, including Argentina, Ecuador, Guatemala, Honduras, Panama, Peru, Puerto Rico, and Venezuela.
- SparroWocky is a modular C++ backdoor with strong anti-analysis features and deep knowledge of Windows internals.
- The malware can establish persistence through services or registry Run keys, execute commands, exfiltrate files, and take screenshots.
- The loader uses DLL side-loading, RC4-encrypted payload files, and in-memory reflective loading to hide execution.
- SparroWocky can load and execute Beacon Object Files and incorporates open-source tooling such as Mbed TLS, MinHook, and COFF Loader.
MITRE Techniques
- [T1583.003] Acquire Infrastructure: Virtual Private Server – FamousSparrow used VPS infrastructure for C&C and delivery servers [‘FamousSparrow has acquired servers to use for C&C and delivery servers for SparroWocky.’]
- [T1587.001] Develop Capabilities: Malware – The group developed SparroWocky and its loader [‘FamousSparrow has developed SparroWocky and its loader.’]
- [T1608.001] Stage Capabilities: Upload Malware – The loader was uploaded to attacker-controlled delivery servers [‘FamousSparrow has uploaded the SparroWocky trident loader to attacker-controlled delivery servers.’]
- [T1190] Exploit Public-Facing Application – FamousSparrow gained access by exploiting public Exchange servers [‘FamousSparrow gained access to targets’ networks by exploiting publicly reachable Exchange servers.’]
- [T1059.003] Command and Scripting Interpreter: Windows Command Shell – SparroWocky can execute commands via cmd.exe [‘Executes by spawning cmd.exe’]
- [T1569.002] System Services: Service Execution – The malware can start itself as a service for persistence [‘When establishing persistence via a service, SparroWocky starts the service directly.’]
- [T1106] Native API – SparroWocky uses Windows native APIs extensively [‘SparroWocky uses the native Windows API.’]
- [T1559] Inter-Process Communication – SparroWocky synchronizes instances with mutex, event, and shared memory [‘SparroWocky uses an interprocess communication mechanism to synchronize instances when a new one is launched.’]
- [T1574.001] Hijack Execution Flow: DLL – The loader runs via DLL side-loading [‘The SparroWocky loader is executed via DLL side-loading.’]
- [T1547.001] Boot or Logon Autostart Execution: Registry Run Keys / Startup Folder – SparroWocky can persist through a Run key [‘SparroWocky can persist via a registry Run key.’]
- [T1543.003] Create or Modify System Process: Windows Service – SparroWocky can create a Windows service for persistence [‘SparroWocky can persist via a Windows service.’]
- [T1134.002] Access Token Manipulation: Create Process with Token – The malware can spawn processes with tokens from active sessions [‘SparroWocky can create processes using a token obtained from any existing user session.’]
- [T1140] Deobfuscate/Decode Files or Information – The loader decrypts its configuration and payload with RC4 [‘SparroWocky’s loader retrieves the configuration and payload via RC4 decryption of the content of a file with a custom format.’]
- [T1480.002] Execution Guardrails: Mutual Exclusion – SparroWocky prevents concurrent instances using a mutex [‘SparroWocky uses a mutex to prevent multiple instances from running concurrently.’]
- [T1564.010] Hide Artifacts: Process Argument Spoofing – The malware hides true arguments by reading them from stdin [‘When loading an external PE file, SparroWocky hooks functions to retrieve its command line arguments from stdin.’]
- [T1027.007] Obfuscated Files or Information: Dynamic API Resolution – SparroWocky resolves APIs with hashing [‘SparroWocky uses a custom API hashing algorithm to dynamically resolve API functions at runtime.’]
- [T1620] Reflective Code Loading – SparroWocky reflectively loads PE and BOF objects into memory [‘SparroWocky reflectively loads its payload into memory. SparroWocky can reflectively load and execute PE and BOF objects.’]
- [T1070.004] Indicator Removal: File Deletion – SparroWocky can delete its files after use [‘SparroWocky can delete itself from the compromised machine.’]
- [T1070.009] Indicator Removal: Clear Persistence – SparroWocky can remove its persistence before termination [‘SparroWocky can remove its persistence mechanism from the compromised machine.’]
- [T1036.001] Masquerading: Invalid Code Signature – The loader preserves an impersonated module’s invalid signature [‘The SparroWocky loader keeps the now invalid signature of the legitimate module it is impersonating.’]
- [T1036.004] Masquerading: Masquerade Task or Service – The service uses legitimate-looking names and descriptions [‘SparroWocky uses legitimate or generic names and descriptions for its persistence service.’]
- [T1083] File and Directory Discovery – SparroWocky can list files and directories on mapped drives [‘SparroWocky can list files and directories on mapped drives.’]
- [T1680] Local Storage Discovery – SparroWocky can retrieve information about mapped storage devices [‘SparroWocky can retrieve information about mapped storage devices.’]
- [T1082] System Information Discovery – The malware collects system details including hostname and Windows version [‘SparroWocky can collect information about the system it is running on, such as the Windows version, hostname, and the IP addresses of network interfaces.’]
- [T1033] System Owner/User Discovery – SparroWocky retrieves the current and active-session usernames [‘SparroWocky can retrieve the username of the current user and of any user with an active session.’]
- [T1120] Peripheral Device Discovery – SparroWocky enumerates display devices [‘SparroWocky can retrieve information about connected display devices.’]
- [T1005] Data from Local System – SparroWocky exfiltrates files from local storage [‘SparroWocky can exfiltrate files from mapped storage.’]
- [T1113] Screen Capture – SparroWocky periodically captures screenshots [‘SparroWocky can periodically capture screenshots.’]
- [T1573.002] Encrypted Channel: Asymmetric Cryptography – SparroWocky uses TLS for its handshake [‘SparroWocky uses TLS, which uses asymmetric cryptography in its handshake.’]
- [T1573.001] Encrypted Channel: Symmetric Cryptography – SparroWocky encrypts exfiltrated data with RC4 [‘SparroWocky uses RC4 to encrypt the information it exfiltrates.’]
- [T1090.001] Proxy: Internal Proxy – SparroWocky can relay traffic between the C&C server and another machine [‘SparroWocky can proxy connections between the C&C server and another remote machine.’]
- [T1090.002] Proxy: External Proxy – SparroWocky can use HTTP or SOCKS5 proxies to reach C&C [‘SparroWocky can use an HTTP or SOCKS5 proxy to connect to its C&C server.’]
- [T1095] Non-Application Layer Protocol – SparroWocky communicates over TLS on TCP [‘SparroWocky uses TLS over TCP to communicate with its C&C server.’]
- [T1041] Exfiltration Over C2 Channel – Stolen data is sent over the same C&C channel [‘SparroWocky exfiltrates data through the same connection used to receive commands from the C&C server.’]
Indicators of Compromise
- [SHA-1 ] SparroWocky loaders and in-memory backdoor samples – 3209689E509205CCDB7E49062B7B407DDC23CAC1, 52C6646759CF6037BB17466203631C4BD794532F, and 2 more hashes
- [Filename ] loader and payload artifacts – winfsp-x64.dll, DukeQt.dll, and .dat payload files
- [SHA-1 ] SparroWocky backdoor sample in memory – 44F0A22B143B79FA760BF31E14C8FFF714C8A2A1, 9AA9FF61BC63CCAB9074FE837F39C980CA9DDC8C
- [IP address ] C&C servers for SparroWocky – 216.238.110[.]120, 38.60.224[.]235, and 15 more IPs
- [Registry keys/values ] persistence and proxy-related settings – SOFTWAREMicrosoftWindowsCurrentVersionRun, HKCUSoftwareMicrosoftWindowsCurrentVersionInternet Settings
- [Service name ] service persistence – ProcAuditManager
- [Registry value ] registry persistence name – SnapCart
- [File/pipe paths ] execution and IPC artifacts – .pipeccpipe, MyMutexName, MyEventName, and MySharedMemName
- [Magic value ] payload file header marker – 0x11328712
- [Encryption/key material ] payload and command traffic protection – 16-byte RC4 key, eight-byte per-message RC4 key, and personalization string acdbenus
Read more: https://www.welivesecurity.com/en/eset-research/beware-sparrowock-backdoor-bites-commands-catch/