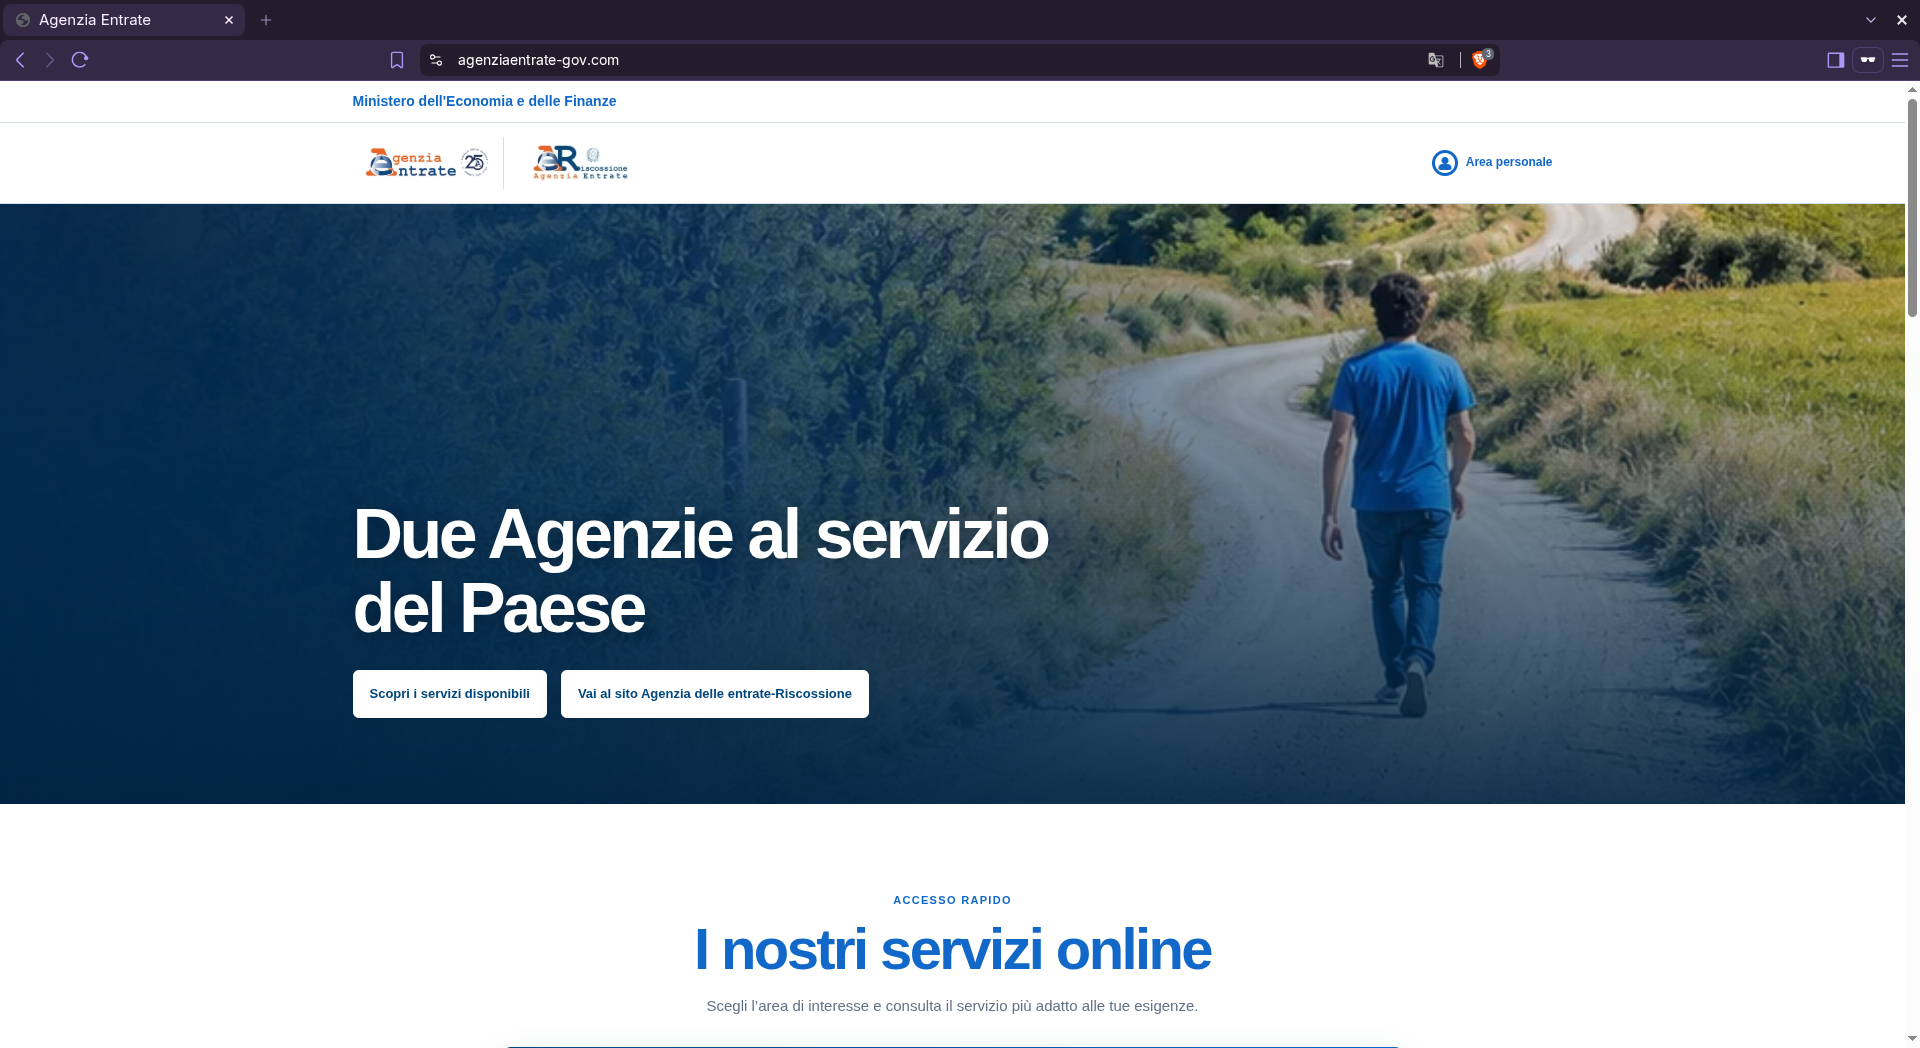
CERT-AGID identified a highly polished phishing campaign impersonating Agenzia delle Entrate and Agenzia delle entrate-Riscossione to steal personal data through a fake “Bonus Vacanze” request. The fraudulent site mimics official pages, redirects some users to legitimate SPID/CieID authentication flows, and then pressures victims to submit identity documents, payroll slips, a selfie, phone number, and email. #AgenziadelleEntrate #AgenziadelleentrateRiscossione #CERTAGID #BonusVacanze #SPID #CieID
Keypoints
- CERT-AGID detected a new phishing campaign abusing the names, logos, and graphics of Agenzia delle Entrate and Agenzia delle entrate-Riscossione.
- The lure used was a supposed application for a “Bonus Vacanze.”
- The fake site was unusually well crafted, with multiple sections and a multi-step flow designed to appear legitimate.
- The homepage closely mirrored the official Agenzia delle Entrate portal and included links to real institutional content.
- A fake “Bonus Vacanze” page offered SPID, CieID, and “Altro” login options; the “Altro” path requested identity card images, health card images, payroll slips, a selfie, phone number, and email.
- SPID and CieID selections redirected users to real authentication pages, increasing the campaign’s credibility.
- CERT-AGID alerted the affected entity, requested takedown of the hosting site, and distributed IoCs through its feed to accredited organizations.
MITRE Techniques
- [T1583.001 ] Acquire Infrastructure: Domains – The attackers used a fraudulent website to host the phishing flow and lure victims into entering personal data (‘la pagina fraudolenta’ / ‘il sito malevolo’).
- [T1566.002 ] Phishing: Spearphishing Link – Victims were directed through a crafted web page that impersonated official government services to collect sensitive information (‘una nuova campagna che utilizza in modo fraudolento il nome, il logo e la grafica…’).
- [T1036 ] Masquerading – The site copied the branding and structure of the official portal to appear legitimate (‘riproduce in modo piuttosto fedele la home del portale dell’Agenzia delle Entrate’).
- [T1204.001 ] User Execution: Malicious Link – Users were induced to continue interacting with the site by clicking navigation items and proceeding through the fake login flow (‘indurre l’utente a proseguire fino all’inserimento dei propri dati’).
- [T1110.001 ] Brute Force: Password Guessing – Not mentioned.
Indicators of Compromise
- [URLs ] phishing website and related pages – the fraudulent home page, “Tutti i servizi” page, and fake “Bonus Vacanze” login flow
- [Organizations impersonated ] branding used in the campaign – Agenzia delle Entrate, Agenzia delle entrate-Riscossione
- [Services / identity providers ] legitimate authentication redirects used to build trust – SPID, CieID, Identity Provider SPID, Ministero dell’Interno
- [Requested data types ] data sought from victims – front/back images of carta d’identità, tessera sanitaria, last three months of buste paga, selfie, phone number, email address
- [IOC feed ] campaign indicators distributed by CERT-AGID – feed del CERT-AGID, Download IoC
Read more: https://cert-agid.gov.it/news/falso-bonus-vacanze-dellagenzia-delle-entrate-ruba-dati-personali/