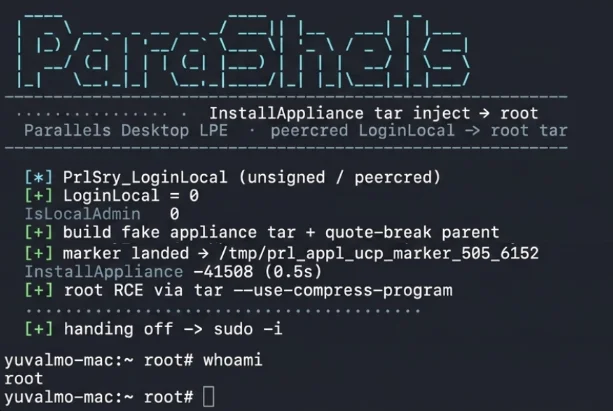
JFrog disclosed CVE-2026-90894, a Parallels Desktop flaw dubbed “ParaShells” that can let any local user on a Mac escalate to root on the host. The issue affects Parallels Desktop for Mac v26.4.0 on Apple ARM-based systems and was fixed by Alludo in Parallels Desktop v27.0.0. #CVE-2026-90894 #ParaShells #ParallelsDesktop #Alludo
Keypoints
- CVE-2026-90894 allows local privilege escalation to root on Mac hosts running Parallels Desktop.
- The flaw is an argument injection bug in Parallels Desktop’s appliance extraction path.
- Exploitation requires a vulnerable Parallels install, an active prl_disp_service, and low-privileged local code execution.
- The attack can lead to system software replacement, data access, and persistence through launchd.
- Alludo fixed the issue in Parallels Desktop v27.0.0, and organizations should inventory and update affected Macs.