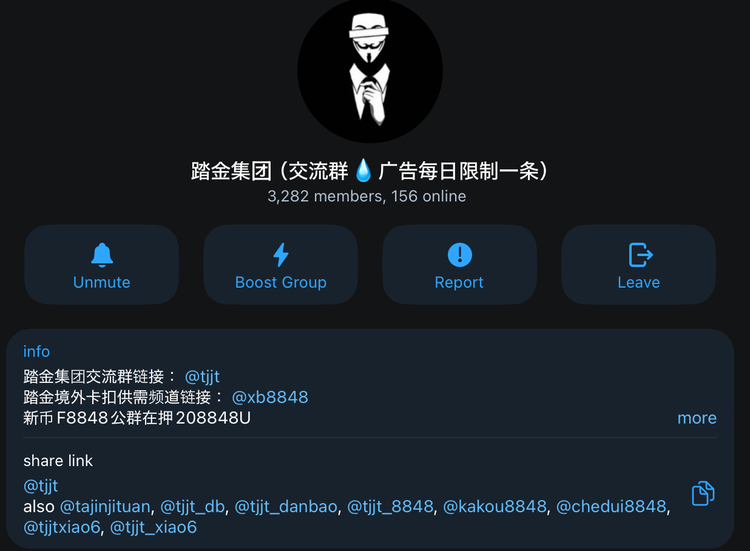
Tajin Group is a Chinese-speaking threat group that uses Telegram-based guarantee marketplaces, Fragment Market, and multiple payment gateways to run phishing, carding, money laundering, and cash-out operations across many countries. The group has shifted from Dabai Guarantee to Xinbi Guarantee, while buying Telegram usernames and anonymous numbers to improve OPSEC and expand its financial crime services. #TajinGroup #DabaiGuarantee #XinbiGuarantee #FragmentMarket #CCAvenue #Geidea #NGenius #Selfridges #ChowTaiFookJewelleryHongKong
Keypoints
- Tajin Group operates as a third-party vendor on Chinese-language Telegram guarantee marketplaces and advertises financial crime services.
- The group is active in phishing, payment card theft, money laundering, fund transfers, and carding.
- Tajin Group shifted from Dabai Guarantee to Xinbi Guarantee, indicating vendors move between marketplaces when conditions change.
- The group buys Telegram usernames and anonymous phone numbers through Fragment Market to strengthen OPSEC and link multiple identities to one Telegram account.
- Tajin Group tests and abuses payment channels such as CCAvenue UAE, Geidea UAE, N-Genius, and Selfridges gift cards for illicit transactions.
- The group has detailed knowledge of BIN prefixes, transaction limits, 3DS behavior, and bank-specific payment controls across multiple countries.
- Tajin Group also promotes cash-out and withdrawal services involving cards, ATMs, NFC relay/ghost-tapping, and high-value goods such as jewelry.
MITRE Techniques
- [T1583.001 ] Acquire Infrastructure: Domains – The group uses unique payment links and merchant pages hosted on payment platforms to support fraud and laundering (‘generated unique payment links’)
- [T1583.003 ] Acquire Infrastructure: Virtual Private Server – Not explicitly mentioned as VPS, but the group offers self-hosted online stores and remote payment setups (‘self-hosted online stores using 3D and 2D payment gateways’)
- [T1585.001 ] Establish Accounts: Social Media Accounts – The group operates multiple Telegram channels and acquires Telegram usernames to manage accounts (‘sold and bought at least 100 Telegram usernames’)
- [T1586.002 ] Compromise Accounts: Email Accounts – The group uses email-based gift card workflows and payment-related account access in support of laundering (‘contact the private Telegram handle… to get the email address’)
- [T1090 ] Proxy – The group uses intermediary payment gateways and unique links to route transactions and obscure direct attribution (‘generate unique payment links’)
- [T1114 ] Email Collection – The group discusses sending and receiving card-related or gift-card related information by email (‘cards arrive in Tajin Group’s email inbox’)
- [T1204.001 ] User Execution: Malicious Link – Victims or operators are directed to open payment URLs that lead to merchant pages (‘Visiting this URL led us to a link belonging to CCAvenue’)
- [T1553.004 ] Subvert Trust Controls: Install Root Certificate – Not directly stated; no clear evidence in the text.
- [T1110.003 ] Brute Force: Password Spraying – Not mentioned explicitly; omitted from operational use.
- [T1021.001 ] Remote Services: Remote Desktop Protocol – Not directly mentioned; no clear evidence in the text.
- [T1078 ] Valid Accounts – The group relies on compromised payment cards, bank-linked accounts, and Telegram identities that function as usable accounts (‘compromised payment cards’, ‘Telegram account’)
- [T1567.002 ] Exfiltration to Cloud Storage – The text references ‘sync panels’ and cloud-based storage abuse for stealing sensitive information (‘stealing sensitive information through cloud-based storage platforms such as OneDrive and Dropbox’)
- [T1056.001 ] Input Capture: Keylogging – Not mentioned explicitly; omitted from operational use.
- [T1649 ] Steal or Forge Authentication Certificates – Not mentioned explicitly; omitted from operational use.
- [T1657 ] Financial Theft – The group conducts carding, cash-out, and money laundering using stolen payment data (‘payment card theft’, ‘money laundering operations’)
Indicators of Compromise
- [Telegram channels ] Tajin Group communication and laundering channels – @tjjt, @xb8848, @tjjt_gx, @dbtm898, @tjjt_liaotianqun, @tjjt_wailiao
- [Telegram usernames/handles ] Operators and service contacts – @tjjt66, @jingwaikakou, @tjjtyw, @tjjt_yewu
- [TON wallet addresses ] Blockchain wallets linked to username ownership and suspicious funds – UQAXN4aCAbJ_1GK1jA38eOpG-py3MYP3RhAuChCG4HE7oX1S, UQCOe_qYf9xsaQFWbq5Jg-Q0BRP_RwwHYIY1ErS9enJrjgoW
- [Phone numbers ] Anonymous/collectible number used for Telegram contact – +888 0353 0246
- [Domains ] Payment and merchant infrastructure – payae[.]cc, ccavenue[.]ae, geidea[.]net, network[.]ae, giftcards.selfridges[.]com
- [Domains ] Bank and merchant references mentioned in BIN lists and contextual analysis – icbc.com[.]cn, lzbank[.]com, abchina[.]com, ccb[.]com, unionpayintl[.]com
- [Payment link paths ] Unique laundering links shared by Tajin Group – /QTTb209, /Qwpf734
- [Merchant names ] CCAvenue-linked entities used in laundering pages – MOON ENTERPRISE TRADING LLC, SUNWEL ENTERPRISE TRADING LLC
- [Cryptocurrency / amounts ] Deposits and payments tied to vendor activity – 208,848 USDT, 88 fragments, 88 Toncoins, 1,899 Toncoins
- [BIN prefixes ] Card BINs blocked or referenced in the fraud scheme – 488910, 528557, 402167, 430938, 465941, 466286, 456933, and many more listed in the article
Read more: https://www.recordedfuture.com/research/tajin-group-gurantee-marketplace