Keypoints
- The campaign targeted organizations in the hospitality and hotel industry across Europe and Asia, with a particular focus on Japan.
- Attackers used photo-themed ZIP archives containing fake image shortcut files to trick users into launching the infection chain.
- The intrusion chain relied on an obfuscated PowerShell script, a Node.js-based implant, dual registry persistence, and C&C communications over nonstandard ports.
- Post-compromise activity included C&C beaconing, forced shutdowns, and compilation of PE payloads, suggesting preparation for follow-on actions.
- The threat actors abused Calendly email notifications and Google URL redirects to send multilingual phishing emails and evade authentication checks through authentication laundering.
- Microsoft identified 78 network IoCs in total, including 73 domains and five IP addresses, later narrowing the set to 77 IoCs after filtering one legitimate domain.
- Additional analysis linked the campaign to thousands of related artifacts, including victim IPs, email-connected domains, malicious IPs, and string-connected domains.
MITRE Techniques
- [T1204.002 ] User Execution: Malicious File – Users were tricked into launching fake image shortcut files inside photo-themed ZIP archives, starting the attack chain (‘users were tricked into downloading photo-themed ZIP archives… fake image shortcut files that, when launched, started an attack chain’).
- [T1059.001 ] Command and Scripting Interpreter: PowerShell – An obfuscated PowerShell script was used as part of the initial execution chain (‘an obfuscated PowerShell script’).
- [T1027 ] Obfuscated Files or Information – The attack chain relied on obfuscation to hinder analysis and conceal malicious behavior (‘obfuscation and persistence were ensured’).
- [T1547.001 ] Boot or Logon Autostart Execution: Registry Run Keys / Startup Folder – Dual registry persistence was used to maintain access on infected devices (‘dual registry persistence’).
- [T1071.001 ] Application Layer Protocol: Web Protocols – C&C communications were carried out over network services using nonstandard ports, indicating protocol-based command-and-control traffic (‘C&C communications over nonstandard ports’).
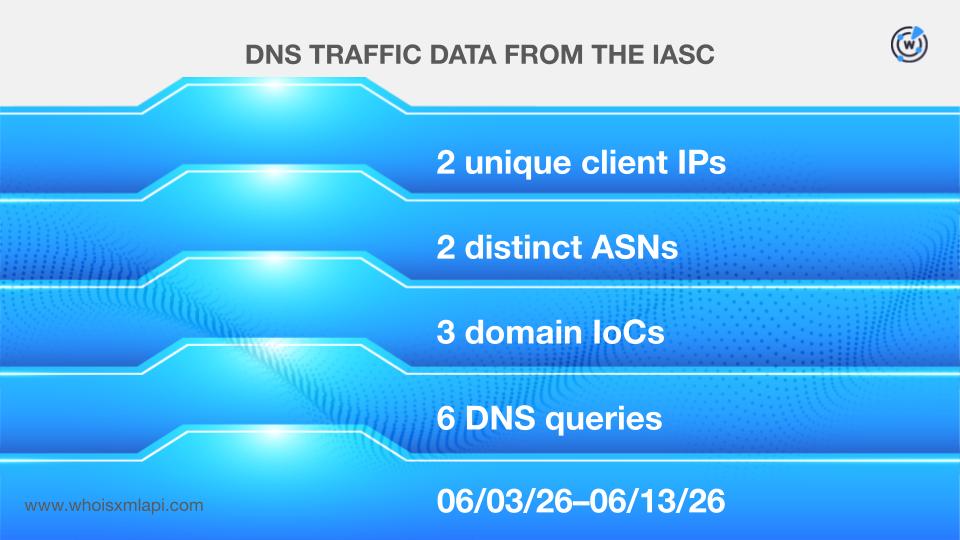
- [T1071.004 ] Application Layer Protocol: DNS – The campaign included DNS-based infrastructure communication and lookups across domains and IPs (‘six DNS queries’, ‘historical domain-to-IP resolutions’).
- [T1583.001 ] Acquire Infrastructure: Domains – The operators registered and used many domains for campaign infrastructure, including typosquatted and likely malicious domains (‘five domain IoCs appeared in four typosquatting groups’, ‘likely registered with malicious intent’).
- [T1566.002 ] Phishing: Spearphishing Link – Phishing emails used multilingual lures and Google URL redirects to deliver links while bypassing checks (‘deliver phishing emails with multilingual lures and subject lines’, ‘Google’s URL redirect functionality’).
- [T1090.001 ] Proxy: Internal Proxy – Authentication laundering through legitimate services was used to obscure the true source of the messages (‘attempted to bypass conventional authentication checks through authentication laundering’).
- [T1105 ] Ingress Tool Transfer – The use of ZIP archives and downloadable artifacts suggests delivery of malicious payloads to victim systems (‘users were tricked into downloading photo-themed ZIP archives’).
Indicators of Compromise
- [Domains] campaign infrastructure and DNS activity – photo-26653[.]cfd, photo-26656[.]cfd, and 2 more domains
- [Domains] typosquatting and related infrastructure – photo-132454[.]cfd, photo-21473[.]xyz, and other 6 items
- [Domains] likely malicious registration – zloapobikahy23[.]bond, heliosup[.]info
- [Domains] historical resolution data and related domains – haobbao[.]com, lestresot[.]info, and other 3 items
- [IP addresses] C&C and victim communications – 172[.]67[.]161[.]215, and 4 more IPs
- [IP addresses] victim-side network activity seen in traffic – 2,357 unique victim IP addresses, including two client IPs under distinct ASNs
- [Email addresses] historical records used to expand related infrastructure – 12 public email addresses and other 63 historical addresses
- [Email-connected domains] additional infrastructure tied to email records – 2,840 unique domains, 26 confirmed malicious
- [String-connected domains] artifacts connected through shared strings – 95 related domains