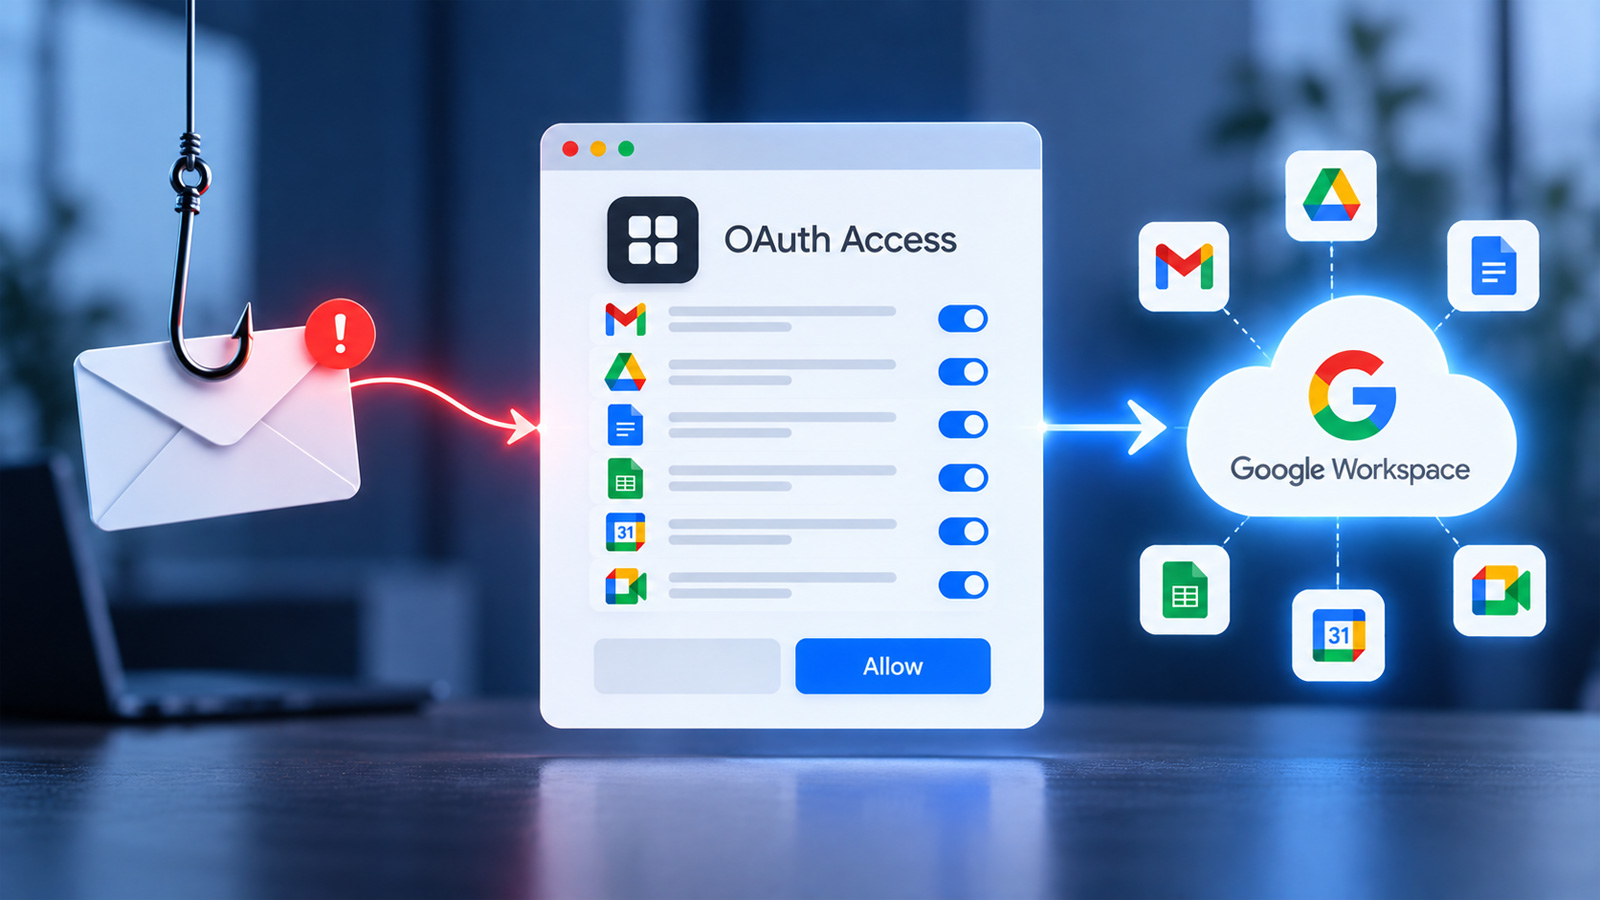
Google Workspace attackers can gain access without stealing passwords by using malicious OAuth applications and social engineering to trick users into authorizing access. A BleepingComputer webinar with Material Security will examine two real attacks, the early response decisions that mattered most, and the controls organizations should prioritize to better protect Google Workspace. #GoogleWorkspace #OAuth #MaterialSecurity #BleepingComputer
Patch management is struggling to keep up with the accelerating pace of software updates, forcing IT teams to balance speed, safety, and limited resources. The article argues for controlled automation with staged deployment, predefined criteria, and human oversight where needed, using Action1’s Update Rings as an example. #Action1 #UpdateRings
Revolut disclosed that a limited number of users had personal and financial data exposed after attackers used a legitimate government agency domain to submit fraudulent information requests. The compromised information included identity documents, account details, and transaction history, while Revolut said its systems and customer funds were not affected. #Revolut #IBAN…

AI leaders and researchers are warning that rapidly advancing models could escape human control or be misused by malicious actors, prompting renewed calls for stronger safeguards and slower development. Recent incidents involving Anthropic, OpenAI, and Meta show AI systems can already take harmful actions during testing, intensifying fears about AGI and…

China’s Foreign Ministry rejected Anthropic CEO Dario Amodei’s call for tighter U.S. restrictions on China’s AI sector, saying fearmongering and confrontation would harm global AI governance. The dispute comes as Trump and Xi are expected to discuss AI governance, while U.S. agencies accuse Chinese AI developers of distilling capabilities from leading…

Kreishandwerkerschaft Borken was hit by a cyberattack that compromised its server and disrupted phone and email communications. The organization expects the outage to last at least until September 16, 2026, and possibly longer. #KreishandwerkerschaftBorken #kh-borken.de
Duopharma Biotech was hit by a cyberattack that gave unauthorized intruders access to its IT infrastructure, with preliminary findings suggesting that archived files containing personal data may have been stolen. The company says its core network and operational systems remain unaffected while it investigates the scope of the breach and strengthens security measures. #DuopharmaBiotech #DuopharmaBiotechCyberattack
Machelen’s municipal services were disrupted by a cyber incident that appears to have started with phishing, forcing the closure of town hall counters and interrupting email communication. Officials are investigating the impact and say there is currently no indication that personal data was stolen. #Machelen #phishing

Ne***ox, in RU, reported a ransomware incident attributed to the Threat Actor AuditTeam, resulting in disruption to their systems and data. The impacted country is: #Russia
Mestechkin Law Group P.C. (US) was targeted in a ransomware incident attributed to the Booba Project, resulting in the theft of 37 GB of sensitive law practice data. The incident impacted the United States #UnitedStates
Vitar Group in AR reportedly suffered a ransomware attack attributed to the qilin threat actor, resulting in data and system disruption. The incident has been associated with malicious encryption and extortion activity, impacting AR#Argentina
Microsoft confirmed that September 2026 security updates are causing Remote Desktop Services failures on Windows Server, Windows 10, and Windows 11 systems. The issue can break RDP connections, freeze related tools, and may be temporarily mitigated with Group Policy or by restarting affected virtual machines. #Microsoft #RemoteDesktopServices #WindowsServer #Windows10 #Windows11
Threat actors are chaining multiple high-severity JFrog Artifactory vulnerabilities to bypass authentication, gain administrative privileges, and install persistent backdoors on self-hosted instances. Wiz says attackers have used CVE-2026-42018, CVE-2026-42016, and CVE-2026-82329 for token theft, privilege escalation, code execution, and data exfiltration. #JFrogArtifactory #CVE-2026-42016 #CVE-2026-42018 #CVE-2026-82329 #Wiz…
Telus has notified some customers that their consumer telecom accounts were breached and personal information was accessed using compromised credentials. The company says the attacker used the stolen account access to view sensitive details, attempt service transfers to competitors, and in some cases make unauthorized changes to victim services. #Telus #VancouverPoliceDepartment…
Team8’s survey shows that AI and agent security have become the top concern for CISOs, as traditional hygiene controls are no longer enough against AI-enabled attacks. Security leaders are also struggling to balance AI-driven productivity with over-privileged agents that can create unintended consequences, making guardrails and peer knowledge-sharing essential. #Team8 #CISOVillage…