
Researchers disclosed DDRop, a cheap hardware attack that silently drops memory writes to break confidentiality and integrity protections in Intel TDX, Intel Scalable SGX, and AMD SEV-SNP. By exploiting the lack of freshness checks in cloud confidential computing memory encryption, DDRop can enable memory tampering, attestation forgery, and other powerful attacks…

geekybunch.com, a U.S.-based organization, reported a ransomware attack attributed to the threat actor “unsafe,” resulting in significant disruption and financial impact estimated at $5 million in lost revenue. The impacted country(s): #UnitedStates
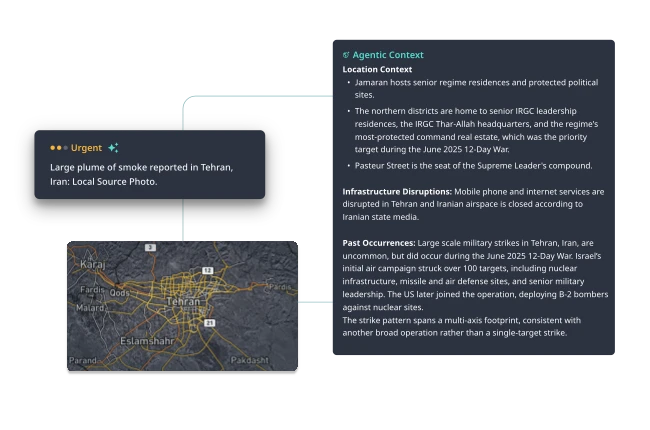
Dataminr has launched Dataminr Advanced for Corporate Security, bringing agentic AI capabilities that help teams corroborate threats, add context, and predict what may happen next in real time. The platform marks a shift from real-time alerting to Autonomous Real-Time Intelligence, with new features powered by Dataminr’s proprietary event archive and task-specific LLMs. #Dataminr #DataminrAdvanced #AgenticCorroboration #AgenticContext #NearTermPredictiveIntelligence

Bitsight is expanding its supply chain risk platform with Beacon, MCP, and agentic capabilities to help security and risk teams detect third-party exposure faster and act with trusted intelligence in AI-driven workflows. The update addresses the growing volume of third-party breaches by unifying exposure monitoring, threat context, and remediation prioritization across the extended supply chain. #Bitsight #BitsightBeacon #ModelContextProtocol #CornerstoneBuildingBrands
Entrust has added new CBOM import and export capabilities to its Cryptographic Security Platform, helping organizations turn cryptographic inventory data into governance, automation, and post-quantum migration actions. The update supports government, finance, healthcare, and critical infrastructure teams as they manage certificate growth, machine and AI identities, compliance demands, and crypto-agility planning. #Entrust #CryptographicSecurityPlatform #CBOM #DORA #NIS2 #SPIRE #Ansible

A forum actor using the name BogotaLeaks is claiming to sell an alleged SIPA database from Argentina containing 38 million pension-related records tied to 9.5 million citizens. The reported data includes highly sensitive personal, banking, and pension details, but the claim remains unverified. #BogotaLeaks #SIPA #Argentina…
A mass-scanning campaign is exploiting CVE-2026-39364 in exposed Vite development servers to steal cloud credentials, configuration files, and other secrets from AWS and Azure environments. F5 observed hundreds of attacks and thousands of events, with activity linked to traversal tricks, multiple Vite access-control flaws, and source IPs that should be blocklisted. #Vite #CVE-2026-39364 #AWS #Azure
The Comune di Prato was hit by a cyberattack on September 8, but the incident was quickly detected and contained by monitoring systems. Early checks found no alteration to databases, archives, or network records, and the municipal council reported the case to the postal police to help identify those responsible. #ComuneDiPrato #PostalPolice
Port of Tanjung Pelepas confirmed a cybersecurity incident that affected its operational systems and temporarily disrupted container terminal operations. A gradual restart began on September 10, but no specific threat actor or malware was identified in the report. #PortofTanjungPelepas #Malaysia
In an incident targeting tpi.tw in Taiwan, the LockBit 5 ransomware group claimed responsibility for disrupting operations and encrypting critical data. The managing a company process was impacted as systems and services were forced into recovery and problem-solving efforts due to the attack on #Taiwan
Eclipse ransomware targeted Rosello et Fils, a FR fruit and vegetable wholesaler based in Saint-Laurent-Blangy, disrupting operations across its Hauts-de-France distribution network. The attack impacted the company’s service to Nord, Pas-de-Calais, and Somme customers, affecting business continuity in France. #France
Eclipse ransomware is claimed to have targeted Dublin City Schools GA, a charter school system in the United States providing academic programs and support services for students and families in Dublin, Georgia. The impact is reported in #UnitedStates

A compromised verified Reddit account for HBO Max was used for 48 hours to run a massive PasteSwitch ClickFix malvertising campaign, pushing 108 deceptive ads that led users to fake macOS and Windows installers. The operation delivered MacSync, AMOS, Amatera Stealer, and cryptocurrency clippers through cross-platform lures, deceptive TLS tactics, and smart contract-based C2 infrastructure. #HBOMax #PasteSwitch #ClickFix #MacSync #AMOS #AmateraStealer #AnimateClipper #ZigClipper #Reddit
Microsoft confirmed that the KB5124008 and KB5124012 September 2026 security updates can cause USB Audio Class 1.0 devices to fail on Windows 11 version 24H2 and later systems. Affected users may see Code 10 errors, no audio output, or broken multichannel playback, while Microsoft is still working on an official fix. #Microsoft #KB5124008 #KB5124012 #Windows11
Revolut disclosed a data breach after sending customer PII, financial records, and verification documents to an attacker who impersonated a government agency using a valid-looking email domain. The company said the incident affected a limited number of customers and that Revolut systems and customer funds were not impacted, while ZachXBT suggested high net worth users may have been targeted. #Revolut #ZachXBT