Panzer ransomware targeted Honda (Peru) in an attack that disrupted the company’s operations and data access. Honda, a global automotive and motorcycle manufacturer founded in 1948, serves customers worldwide, and this incident impacted Peru. #Peru

Foremost Mfg in the US was targeted by the Qilin ransomware threat actor, resulting in disruption to their systems and data. The incident indicates ransomware activity affecting operations in #UnitedStates
Genesis ransomware, attributed to the threat actor genesis, targeted Dorfman Abrams Music, P.C, a full service CPA firm in the US, to disrupt operations and potentially extort data. The impacted country(s): #UnitedStates
Bernath & Rosenberg, a full service CPA firm in the US, reported a ransomware incident attributed to the genesis threat actor. The attack impacted systems and data availability, affecting operations within #UnitedStates
Revolut confirmed a data security incident in which attackers impersonated a government body using a legitimate government-domain email address to trick the company into sharing sensitive customer information. The leaked data may include passports, driving licenses, selfies, account statements, IBANs, and transaction histories, creating long-term risks of identity theft, phishing, and…

This collection of cybersecurity job openings highlights strong demand for professionals across AI security, cloud protection, incident response, governance, and security architecture. Roles span global organizations and critical sectors, with growing focus on securing AI systems, cloud platforms, embedded environments, and emerging threats such as post-quantum risk. #SecNinjazTechnologies #TexasHealthAndHumanServices #IntegerTechnologies #Alice #SouthwarkCouncil #ReserveBankOfAustralia #CypressCreekEnergy #PwC #Adobe #JPMorganChase #Invicti
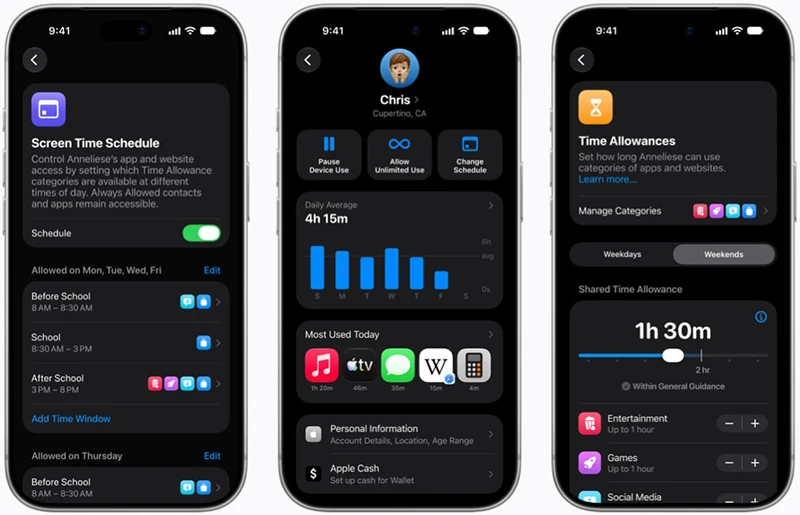
Apple has revamped its child-safety features across iPhone, iPad, and Mac, centering everything on Child Accounts and age-based protections that expand as children mature. The update adds new permission controls, flexible Screen Time allowances, broader Communication Safety, and requires every device in a Family Sharing group to run iOS 27, iPadOS 27, macOS 27, watchOS 27, or visionOS 27. #Apple #ChildAccount #FamilySharing #ScreenTime #CommunicationSafety

Five alleged leaders of Black Axe’s South African wing were extradited to the United States to face wire fraud, money laundering, and identity theft charges tied to romance scams and advance fee scams. The case is part of a wider international crackdown on Black Axe, a hierarchical criminal network accused of using fake identities, threats, and business entities to steal from victims. #BlackAxe #FBI #U.S.SecretService #JusticeDepartment
Hackers hijacked HBO Max’s official Reddit account to run malicious ads that led users to ClickFix pages and infected Windows and macOS devices with information-stealing malware. The campaign, linked by researchers to PasteSwitch, also pushed fake AI tools, developer software, and cryptocurrency wallet apps to steal credentials and wallet recovery phrases. #HBOMax #PasteSwitch #MacSync #AMOS #AmateraStealer #AnimateClipper #ZigClipper
A browser extension named Twitch Enhanced Viewer | JeetBot, available in the official Chrome and Firefox stores, is sending Twitch OAuth session tokens to a commercial bot service through proxy servers. Socket found that the extension captures users’ authorization headers, leaks tokens in cleartext logs, and recommends removing the extension and re-authenticating Twitch sessions. #TwitchEnhancedViewer #JeetBot #Twitch
Homebrew 7.0.0 introduces a built-in vulnerability scanner, a Homebrew-specific advisory database, and stronger sandboxing controls for macOS package installs. It also fully releases the native BrewUI interface on macOS 26 “Tahoe” and later, while improving package installation speed through concurrent operations. #Homebrew #BrewUI #OSV.dev
Japan’s Digital Agency disclosed a breach that may have exposed 246,000 record rows of employee-related personal data after attackers exploited a vulnerability in a VPN device used by the Government Solution Service. The agency says no My Number, bank, or pension data was exposed, and it has not found confirmed misuse so far, but it warned of phishing and impersonation risks. #JapanDigitalAgency #GovernmentSolutionService #VPN
Microsoft released emergency out-of-band Windows updates to fix Remote Desktop Services failures caused by September 2026 security updates, which also affected some Hyper-V and USB audio functionality. The updates restore RDP access and address several Windows Server and Windows 11 issues while Microsoft continues working on remaining USB Audio Class 1.0 problems. #Microsoft #WindowsServer #Windows11 #RemoteDesktopServices #HyperV #USBAudioClass10

A flaw in Telegram Desktop allowed a bot message to hide JavaScript inside HTML chat exports, letting attackers steal exported chat contents or alter what users saw when opening the file in a browser. Telegram fixed the issue in later versions, but older HTML exports made before the patch can still…

Hunt.io found an attacker inside 3BB’s network in Thailand using MeshCentral as a hidden backdoor to keep remote control of internal systems. The intrusion targeted subscriber data, internal portals, and a FortiGate SSL-VPN gateway, with evidence also pointing to possible overlap with the Jasmine network. #3BB #MeshCentral #FortiGate #CVE-2024-21762 #Jasmine…