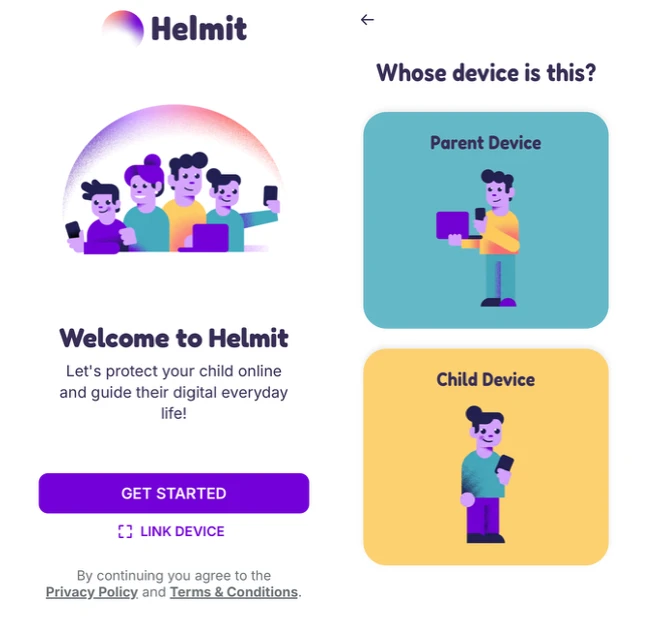
Helmit is a parental control app that combines AI-powered social media monitoring, screen time limits, web filtering, location tracking, and safety alerts to help parents identify online risks. It supports multiple devices and services, including WhatsApp, Instagram, Telegram, Discord, Signal, YouTube, Gmail, and Outlook, while showing only the messages tied to alerts rather than full chat histories. #Helmit #WhatsApp #Instagram #Telegram #Discord #Signal #YouTube #Gmail #Outlook #EUKidsAct
Large companies may choose to stay on ECC past the 2027 deadline and pay SAP for extended support until 2030, often because the real concern is disruption rather than budget. A Central American migration showed that even when every quality gate is met, poor sizing, thin testing coverage, and limited client bandwidth can still make go-live difficult. #SAP #ECC #MIGNOW #CentralAmerica

Newman Tractor (newmantractor.com) in the US reported a ransomware incident attributed to the threeam threat actor. Since 1976, Newman Tractor has served the heavy equipment industry, operating domestically and internationally, and the attack impacted #UnitedStates.
The LockBit 5 ransomware group claimed an attack on siinqeebank.com, a licensed Ethiopian financial institution providing inclusive and innovative banking services. The incident impacted Somalia #somalia
Qilin ransomware claimed to have compromised IKEGAMI TSUSHINKI COMPANY LIMITED in Japan and exfiltrated data, demanding payment to prevent further disclosure. The incident was reported as impacting Japan. #Japan
ShopDunk in Thailand reported a ransomware incident attributed to the qilin threat actor. #Thailand
The ransomware claim targets Zorlu Holding in Turkey, attributed to the qilin threat actor. The attack resulted in data and system disruption across Turkey#Turkey
Maryann Kriger and Bonita Orthodontics in the US were targeted by the incransom ransomware group, despite prior attempts to warn the clinic. The threat actor’s leak threatens to expose minors’ private patient information, following repeated ignored notifications from our team. #UnitedStates
Incransom ransomware reportedly targeted SECOND HOUSE (Second House, S.L.), a privately held Barcelona-based real estate company with over 26 years of experience in property acquisition, renovation, and legalization of building states. The incident impacted operations in #Spain.
Euramex Management Group in the US reported a ransomware incident linked to threat actor Orova, impacting its operations connected to Avila Real Estate, LLC, a vertically-integrated multifamily company headquartered in Atlanta, Georgia. Avila has developed over $800 million across 25 multifamily transactions since 1986 and the attack affected its business services and data availability. #UnitedStates
ACIL (acilnet.com) in Turkey was targeted by the krybit ransomware threat actor, allegedly encrypting company systems and disrupting operations. The incident impacted Turkey #Turkey
A ransomware claim involving ARS Renacer, S.A. (arsrenacer.com), where threat actor dragonforce (AR) allegedly exfiltrated extensive health insurance data including PHI, affiliate identity records, financial details, and access credentials. The dump indicates high-impact exposure across the organization, creating significant risks for patient privacy, financial systems, and regulatory compliance in #DominicanRepublic (AR)

Cybersecurity Threat Research ‘Weekly’ Recap. The roundup covers credential theft, phishing, and session abuse using device-code kit GhostCode, rogue Entra MFA provider TrustSink, and Fast Flux phishing infrastructure, alongside regional lures like Falso Bonus Vacanze and banking malware KREMLIN and RatHat. It also highlights cloud/identity and APT activity (including TraderTraitor, NightEagle, FamousSparrow/SparroWocky/SquawkDoor, and Operation RapidRust) plus crimeware and supply-chain/underground operations such as XMRig, MovieReaper, Evooo1Bot, PhantomRaven, and Tajin Group.
Alabama Woman’s Health Care, a US medical, well-being and aesthetic care organization, reported that threat actor emperador encrypted several thousand employee and client documents as well as an archive of photos. The incident impacted the organization in #UnitedStates
There was 1 defacement incident targeting Vietnam, with the attacker identified as Trenggalek Cyber Army. The content lists Vietnam as the targeted country and names Trenggalek Cyber Army as the attacker. #Vietnam…