Barracuda claims to have obtained complete database dumps from Croatia’s Ministry of Agriculture, Forestry and Fisheries, including personal data of Croatian residents and agricultural registration records. It also alleges access to contracts and confidential documents, despite authorities reportedly stating no breach occurred, and is selling the data for $50,000. #Croatia
BPFDoor is a stealthy Linux backdoor that waits for a “magic packet,” making it unusually hard to detect and especially dangerous in telecom and edge-device environments. Christiaan Beek of Rapid7 Intelligence explains why attackers target mail gateways, VPNs, and other appliances, and how CISOs should report visibility gaps honestly to the board. #BPFDoor #Rapid7Intelligence #Linux

September 2026 Patch Tuesday set a Microsoft record with 973 CVEs addressed, while only two vulnerabilities were known exploited and none were publicly disclosed. The update roundup also highlighted Office end-of-support migration issues, Apple’s macOS 27 Golden Gate release with a zero-day fix, and Windows 11 26H2 arriving alongside other important Microsoft fixes and upcoming support cutoffs. #CVE-2026-85880 #CVE-2026-81963 #KB5002907 #CVE-2026-86950 #Windows11 26H2 #Office2016 #Office2019 #macOS27 #GoldenGate
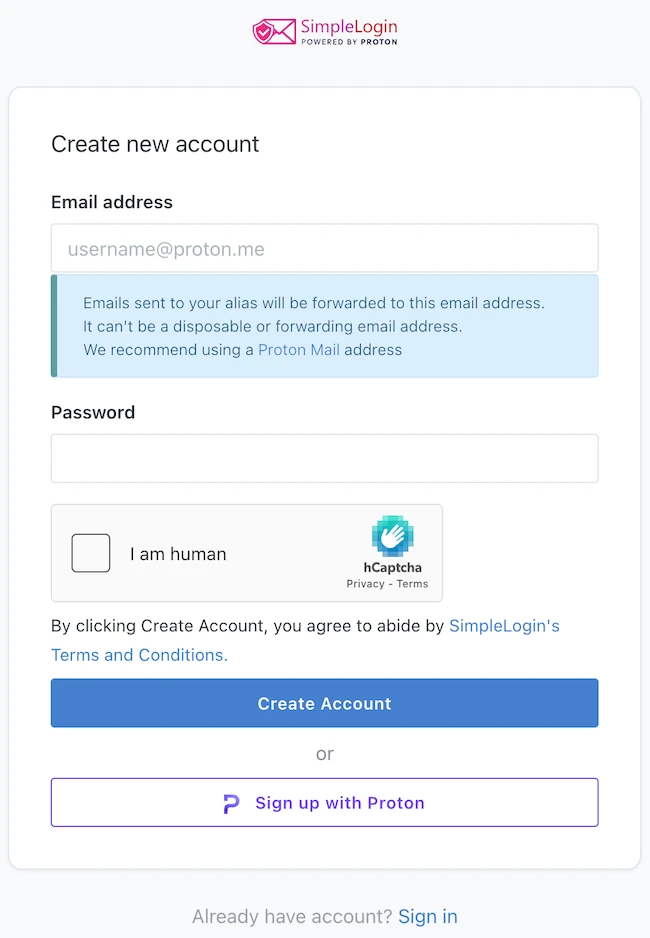
SimpleLogin, a Proton email alias service, lets users create separate forwarding addresses to protect their primary inbox, reduce tracking across websites, and manage unwanted messages more easily. In testing, alias creation, forwarding, and replies worked smoothly, with support for browser extensions, mobile apps, and strong account security options. #SimpleLogin #Proton
Pwn2Own Ireland 2026 ended with researchers earning more than $1.2 million for exploits against phones, printers, smart speakers, smart home hubs, AI infrastructure, coding tools, and cloud databases. Google Pixel 10 hacks brought in the biggest payouts, while Sonos, Oracle, OpenAI Codex, Nvidia Dynamo, LiteLLM, Philips Hue Bridge Pro, Samsung Galaxy…
Citrix has warned that a critical NetScaler flaw, tracked as CVE-2026-107406, could enable remote code execution or denial-of-service and needs immediate patching. The issue affects certain NetScaler ADC, NetScaler Gateway, and Secure Private Access Hybrid deployments, and Citrix says no unmitigated exploits are known at this time. #Citrix #NetScaler #CVE-2026-107406…
Anthropic announced OSS Scanner, a free opt-in service that sends AI-generated vulnerability reports directly to open source maintainers without human review, along with suggested fixes and PoCs. It also launched the Critical Infrastructure Defense Program to help OT providers and their partners identify and remediate long-standing security flaws in essential systems…

nightspire allegedly deployed ransomware against PMG Project Management Group in AE, with the status of data availability currently unknown. The impacted country is #UnitedArabEmirates
The Bernard Osher Foundation in the US reported a ransomware claim involving threat actor nightspire, with data availability currently unavailable. The incident is believed to have impacted users and operations in #UnitedStates
nightspire ransomware impacted Fondy Food Pantry in the US, with the availability of stolen or encrypted data currently not available. The incident is reported in the United States #UnitedStates
Ninety percent of companies want to move toward autonomous IT operations in the next two years, but most still want a human to approve AI decisions and lack the visibility, automation, and governance needed to support that shift. The report also says AI is already changing service desk work, with many teams using it to detect and fix issues before employees notice. #agenticAI #AIcodeSprawl
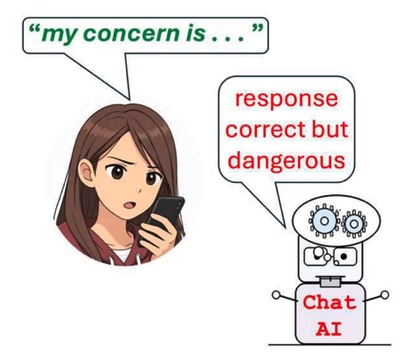
Researchers from George Washington University say they can model when an AI system may tip into producing undesirable outputs by analyzing its attention dynamics and prompt history. Their findings suggest early-warning controls could help reduce rogue behavior in open-weight transformer models, though it cannot be fully eliminated. #GeorgeWashingtonUniversity #NeilJohnson #FrankYingjieHuo…
Nightspire ransomware is claimed to have targeted M,äntelhaus Kaiser GmbH & Co. KG, DE. The claim’s details are not reliably verifiable from available information. #Germany

Anthropic has launched a new critical infrastructure defense program that pairs Claude models and its security expertise with major cybersecurity companies to find and fix vulnerabilities in critical infrastructure and open-source software. The initiative includes a new opt-in scanning service for open source projects, aiming to speed up reporting, suggest patches, and strengthen defenses before weaknesses can be exploited. #Anthropic #Claude #Accenture #BoozAllen #CrowdStrike #Deloitte #Dragos #Hitachi #InsaneCyber #NozomiNetworks #PaloAltoNetworks #PwC #RockwellAutomation

Prasan Nepal, also known as “Trippy,” pleaded guilty to conspiracy to commit sexual exploitation of a child for his role in helping lead the 764 child sextortion network. Prosecutors say he and his co-conspirators used 764 and its 764 Inferno subgroup to groom, extort, and abuse minors across multiple jurisdictions. #764 #764Inferno #PrasanNepal #LeonidasVaragiannis #TheCom