CoE Press Equipment in the US reported a ransomware incident attributed to the Akira threat actor. The attackers claim they will exfiltrate and threaten to leak 25GB of corporate data, including employee personal information such as SSNs and passports, financial records, client documents, NDAs, and HR files. #UnitedStates

GOTTHELF in Moldova reported a ransomware incident in which the Booba Project exfiltrated 2 GB of healthcare data. The claim indicates the attackers targeted compromised systems and stole sensitive information, impacting Moldova #moldova
Tulare Western High School in the US reported data theft and ransomware activity by the Booba Project, with approximately 35 GB of Education Administration Programs data stolen. The incident impacted #UnitedStates
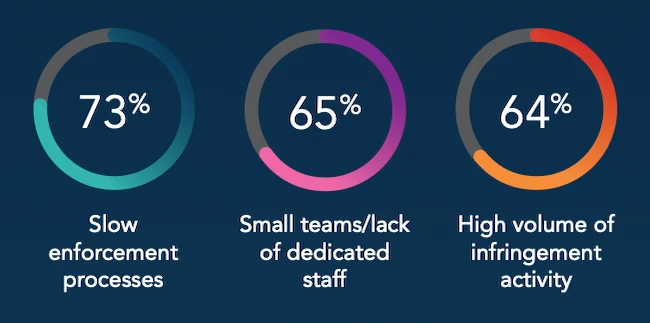
CSC’s State of Online IP Risk 2026 report says impersonation, phishing, and domain-name abuse are the most concerning forms of online intellectual property infringement, with internet branded content, online marketplaces, and paid search being the most targeted channels. The report also highlights how AI, executive impersonation, and large-scale domain registrations are making fraud faster, harder to detect, and more damaging to brands and consumers. #CSC #FIFA #ICANN #LinkedIn #FashionWeek

AI-powered social engineering is helping attackers bypass traditional phishing defenses by using deepfakes, vishing, smishing, and business email compromise across email, calls, and video meetings. Gartner says CISOs should make verification the default for risky requests, harden account recovery and privileged access, and correlate suspicious activity across channels to spot multimodal impersonation. #Gartner #CraigPorter #Deepfake #BusinessEmailCompromise #Vishing #Smishing #HongKong

A new SpyCloud study found that nearly 18% of U.S. water and wastewater organizations have identity data actively exposed by infostealers, with one infected vendor device exposing logins tied to about 167 utility metering tenants. The report warns that stolen credentials can enable cascading supply chain exposure and provide attackers with legitimate access paths into corporate email, VPNs, and operational technology systems. #SpyCloud #CISA #EnvironmentalProtectionAgency
Security researcher Abdelhamid Naceri, also known as Nightmare Eclipse, released BigDiskBuster, a Microsoft Defender zero-day that can block antivirus signature and platform updates on supported Windows versions. The disclosure is part of Naceri’s ongoing series of Windows and Defender exploits, following earlier tools like UnDefend and ShieldCrash, with several flaws still unpatched by Microsoft. #BigDiskBuster #UnDefend #ShieldCrash #NightmareEclipse #MicrosoftDefender
D-Link has warned about a maximum-severity flaw, CVE-2026-86296, in legacy DIR-822A routers that can be exploited without authentication to cause a stack-based buffer overflow in the DHCP server component. The company also said a public proof-of-concept exists and that it is investigating a second public-PoC issue, CVE-2026-86510, while advising customers to keep DIR-822A devices off the internet and restrict management access. #DLink #DIR822A #CVE202686296 #CVE202686510 #CISA
Real Google Workspace breaches often start with social engineering and malicious OAuth apps that trick users into granting access, not with stolen passwords or advanced exploits. This webinar with Material Security will examine how those attacks unfolded, what happened in the first hours of response, and which security controls matter most for fast-growing teams. #GoogleWorkspace #MaterialSecurity #RajanKapoor #RickFitzgerald #OAuth #BleepingComputer
Textile City in Canada reported a ransomware incident attributed to the qilin threat actor, impacting its systems and data. The attack resulted in operational disruption and data compromise. #Canada
Pr***IT in Italy reported a ransomware attack attributed to the threat actor AuditTeam, resulting in unauthorized encryption and disruption of its systems. The incident was claimed to have affected business operations and data availability across Italy. #Italy
AuditTeam ransomware activity targeted vit.ac.in in India, a prominent Indian institution (Vellore Institute of Technology, VIT) known for strong engineering and technology programs. The incident affected systems in India. #India
The U.S. has proposed a new AI incident notification mechanism with China to improve transparency and reduce national security risks tied to advanced AI systems. The talks also advanced plans for a new Board of Trade ahead of the upcoming Trump-Xi meeting, while both sides continued discussions on tariffs and economic…
A joint advisory from Japan, the United States, Australia, and Germany attributes the WaterPlum, or Contagious Interview, operation to a North Korean scheme that impersonated companies to recruit developers and IT professionals. The campaign infected at least 30,000 devices in more than 100 countries, stole funds from over 7,000 cryptocurrency wallets,…

WordPress patched 11 vulnerabilities last week, including Click2Shell, a flaw that could allow remote code execution through specially crafted theme-preview URLs. pwn.ai found that an unauthenticated attacker could force installation of an attacker-selected theme and potentially execute PHP code on the server, earning a $300 bug bounty for the report. #Click2Shell…