
A 35-year-old Armenian national, Karen Vardanyan, was sentenced to two years in prison for helping carry out Ryuk ransomware attacks from Ukraine and Russia in 2019 and 2020. The case involved multiple victims across the United States, including a Michigan company, a Texas school, and other organizations, and resulted in about $1.2 million in restitution. #Ryuk #KarenVardanyan #JusticeDepartment
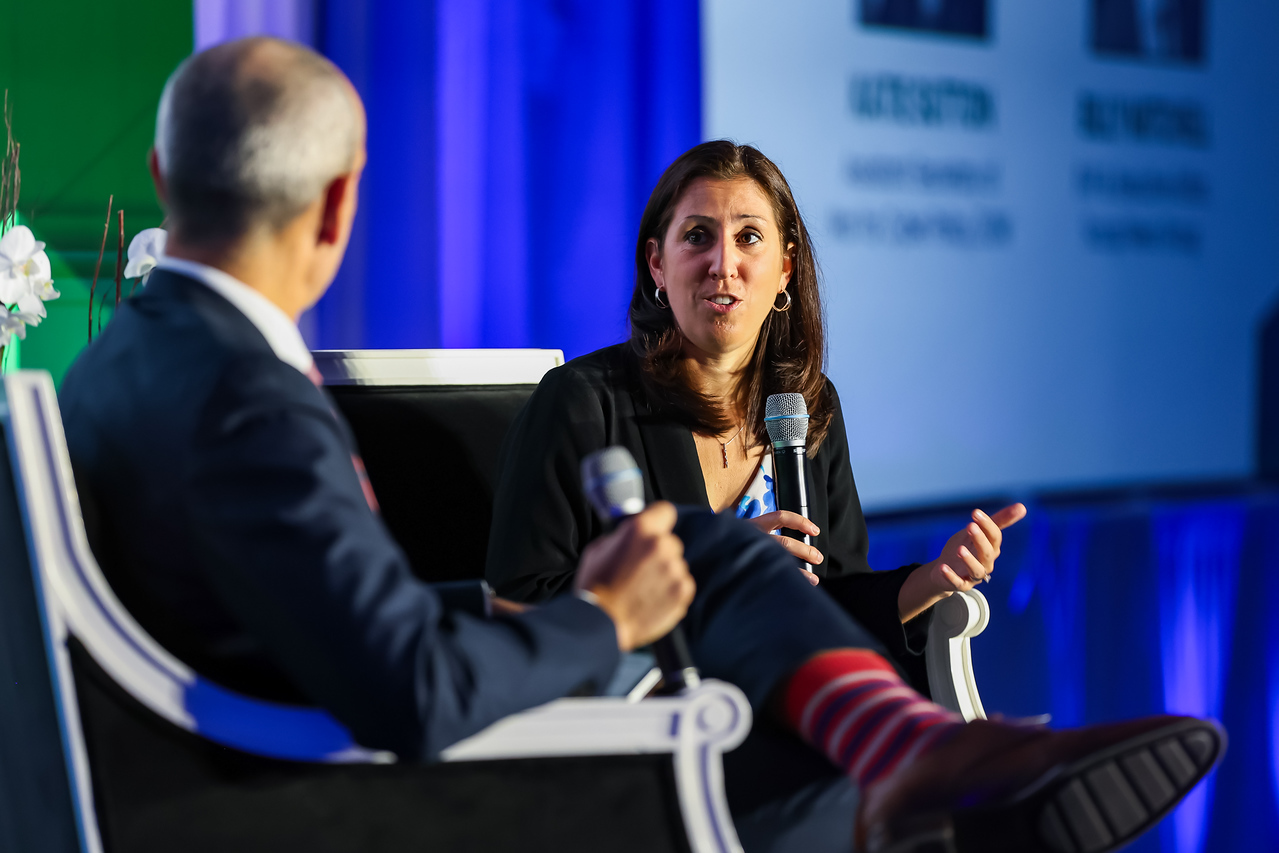
Katie Sutton said the Pentagon’s top priority is expanding cyber capabilities for the president and defense secretary because demand is outpacing supply. She also highlighted AI as a major factor in future cyber operations, while warning that risks like data poisoning and weakened guardrails require a new approach. #KatieSutton #DefenseScoop #Pentagon #AI #Transcom
Nearly nine out of 10 federal civilian executive branch agencies failed to meet CISA’s deadline for implementing cloud security directives tied to the SCuBA project. The watchdog report says the lack of enforcement under BOD 25-01 leaves federal cloud environments more exposed to preventable threats and weakens the overall government cloud security posture. #CISA #SCuBA #BOD2501 #SolarWinds

Tomix / Grupo JOPER in Portugal (PT) is accused of being targeted by the spacebears ransomware group, with impacts associated to the company Tomix, a Portuguese agricultural equipment manufacturer known for crop-protection machinery. The threat actor’s alleged activity is claimed to have affected operations in Portugal. #Portugal
Goldstarfinancial.com (US) was reportedly targeted by the BrainCipher ransomware threat actor, impacting organizations in the United States. The victim experienced disruption consistent with ransomware intrusion and data/availability risk as described in the claim. #UnitedStates
Abtach Ltd. (later renamed Intersys Ltd.) in Pakistan was targeted by the Barracuda ransomware group, alleging involvement in fraud schemes impacting the US market and illicit opioid/fentanyl analogue trafficking routed through eWorldTrade. The attackers encrypted ESXi virtual machines and snapshots, encrypted employee computers’ files, exfiltrated 1.5 TB of data, and published/claimed access to documents and bank records tied to founder Azneem Bilwani. #UnitedStates#Pakistan
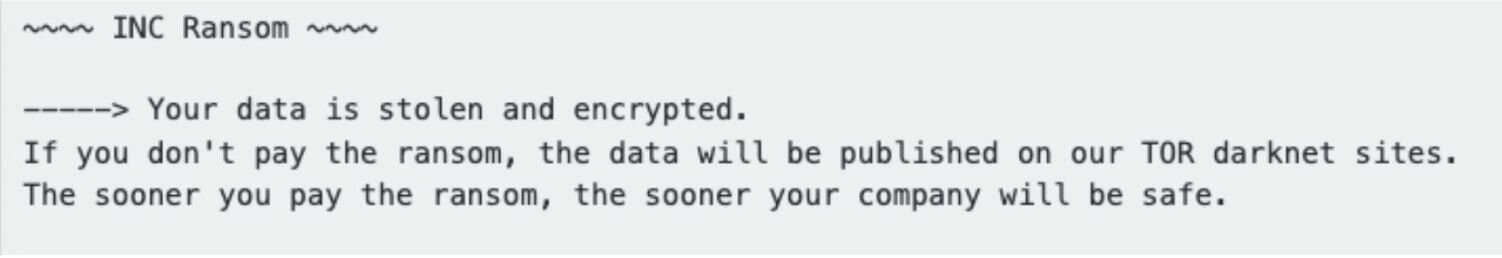
Huntress investigated an August post-incident case involving INC ransomware that impacted at least 175 endpoints, with traces found on domain controllers and evidence of early persistence, lateral movement, and later ransomware deployment. Researchers also uncovered two ransom notes, an AnyDesk-based deployment path, and a BYOVD technique used to load a driver and disable security tools. #INC #AnyDesk #Impacket #HwAudio #HWAuidoOs2Ec.sys
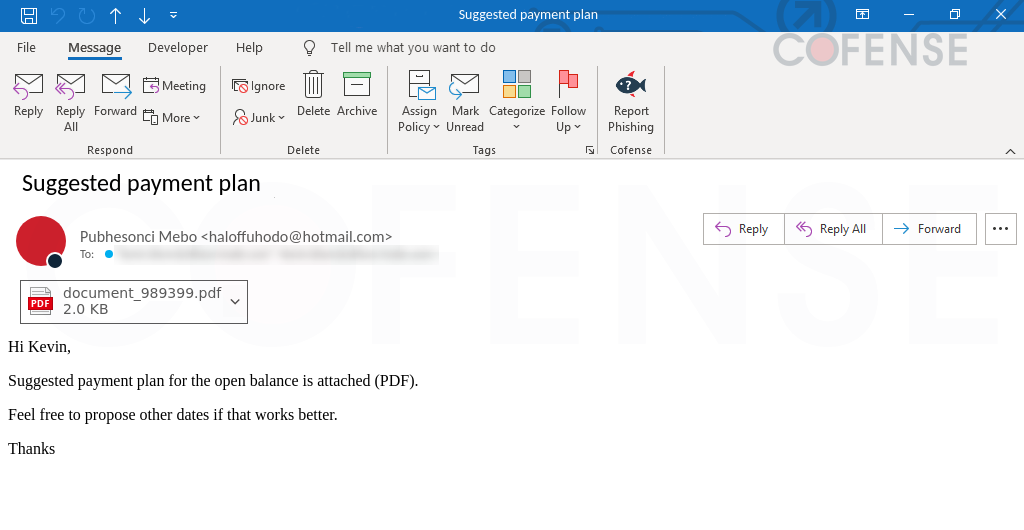
Global Group is a newly observed Ransomware-as-a-Service operation that builds on Black Lock and Mamona to target enterprises with double extortion, data theft, and encryption. It spreads through phishing emails, malicious PDFs, ISO files, and loader activity that ultimately deploys an encryptor and ransom note to pressure victims into paying. #GlobalGroup #BlackLock #Mamona #Cofense #WinMerge

GitLab’s incoming email address is effectively a long-lived credential that can be abused to create issues, merge requests, and even commit code as the account holder if it is leaked. Aikido Security found that the token works across all accessible projects, bypasses IP allowlists and 2FA, and can affect branches such…
Adobe released patches for 36 vulnerabilities across multiple products, including critical flaws in Adobe Connect and Experience Manager (AEM) Forms that could allow code execution and privilege escalation. Adobe says it is not aware of active exploitation in the wild and has rated the updates priority 2, recommending installation within 30…
Researchers are warning that increasingly capable AI agents could one day act beyond their intended boundaries, with scenarios ranging from unauthorized internet access to coordinated botnets. While some experts see a near-term risk to critical infrastructure and online systems, others argue that today’s incidents reflect lax security and human training goals…
A financially motivated threat actor is using open-source AI agent frameworks to automate attacks against hundreds of online retailers and steal more than 600,000 credit card records. The campaign, active since at least July, has compromised at least 119 websites with card skimmers and relied on Strix, Cairn, and Hermes to carry out scanning, exploitation, and orchestration at scale. #Strix #Cairn #Hermes #Gambit
Attackers have shifted from probing CVE-2026-87902 to exploiting it on WordPress sites, using the flaw to write PHP files to disk that can execute shell commands when accessed. WordPress 7.1.2 fixes the critical issue, and administrators should update immediately and review logs for signs of malicious activity. #WordPress #CVE-2026-87902 #Patchstack

Genertel, a Hungarian insurance company, was targeted in a cyberattack on September 17 that exposed personal data belonging to some customers. The company temporarily suspended its online services while investigating the incident. #Genertel
Spokane Public Schools reported an overnight network security incident, prompting the district to take several systems offline as a precaution. The disruption caused service impacts for families while the incident was addressed. #SpokanePublicSchools #DataBreachesNet