Maileva, a service of La Poste, suspended its operations after unauthorized access attempts were detected and a cybercriminal tried to abuse the platform for illegitimate mailings. No personal data breach has been reported so far, and a complaint has been filed. #Maileva #LaPoste

Stevens Point is investigating a possible cyberattack after multiple municipal servers went offline, disrupting phone and email services. City officials say there is no public confirmation of the cause yet and no evidence that customer data has been compromised, while emergency services remain operational. #StevensPoint

Daily Recap, Exploited critical flaws are driving active attacks across Roundcube, TeamCity, Check Point VPN, and WordPress, while SolarWinds and Adobe push urgent patches for RCE and other serious issues. In parallel, criminals target users and organizations with threats like RemControl, ClickFix infrastructure abuse, and AI-driven skimmers, alongside ongoing policy and security operations focus from CISA updates to new Windows 11 and Google AI compute changes. #Roundcube #TeamCity #CheckPoint #WordPress #SolarWinds #Adobe #RemControl #ClickFix #Terraform #MikroTik #AI #skimmers #AstranaHealth #GitLab #KB5124010 #FileHistory #agenticremediation #PrivateAICompute #IonQ #Ryuk #KarenVardanyan
Bitget said suspected North Korean hackers stole $351.6 million from its hot and warm wallets after unauthorized transfers were detected on Thursday evening. The exchange paused withdrawals, is investigating with law enforcement and security firms, and says its User Protection Fund will cover the losses. #Bitget #NorthKoreanHackers #Mandiant #SlowMist
Microsoft confirmed a known issue causing black screens and desktop loading problems after the August 2026 preview and later updates, mainly impacting Azure Virtual Desktop hosts using FSLogix. A temporary workaround is to manually launch explorer.exe, while enterprise customers can use Known Issue Rollback through specific Group Policy updates. #Microsoft #AzureVirtualDesktop #FSLogix #KB5120996 #KB5120998 #KB5124008 #KB5122880
A Kosovar national has pleaded guilty for helping run Rydox, a major illegal marketplace that sold stolen identities, login credentials, credit card details, and cybercrime tools. The operation was dismantled after an international law enforcement action that arrested administrators, seized infrastructure, and shut down the Rydox marketplace. #Rydox #ArditKutleshi #JetmirKutleshi #ShpendSokoli
Researchers at Graz University of Technology showed that file-change notifications in Linux, Android, Windows, and macOS can leak user activity such as typing rhythms, website visits, and app interactions. They also found serious impacts on Linux, Android, and Windows, including keystroke inference, WhatsApp file monitoring, and full path disclosure, with a…
GUTcert has informed the relevant data protection authority about the incident and is continuing to assess which individuals and data may have been affected, with updates provided as new facts emerge. Organizations should independently review whether the breach triggers reporting duties under BSIG, NIS2, DORA, or critical infrastructure rules, especially if sensitive security-related information may have been exposed. #GUTcert #BSIG #NIS2 #DORA
There were 3 defacement incidents targeting Georgia, the United States, and Thailand. The attackers involved were Trenggalek Cyber Army and Dr.Nexusec-Cyber. #Georgia #UnitedStates #Thailand…

Inversiones Bol,ívar in Colombia reported a ransomware incident attributed to the qilin threat actor, resulting in disruption of business operations. The attackers’ actions impacted data availability and likely caused encryption-related damage within the organization. #Colombia
All Tech Machine & Engineering, US, reported a ransomware attack involving the Qilin threat actor. The incident resulted in encryption and disruption of systems, impacting #UnitedStates
Qilin ransomware targeted Dao Group, deploying malicious encryption to disrupt operations. The actor’s actions resulted in data loss and operational downtime affecting organizations in #N/A
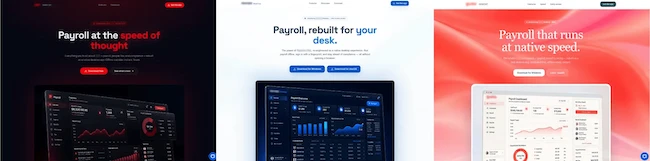
An attacker created fake desktop app pages for three major US payroll and HR platforms that do not offer desktop apps, then used them to install ScreenConnect for hidden remote access. The campaign used AI-generated lure pages, GitHub-hosted installers, and a single command-and-control server to potentially divert or drain payroll accounts. #ScreenConnect #Lovable #Vercel #GitHub

Docker has introduced Docker Cloud Sandboxes, a secure cloud-based environment for running AI agents and long-lived workflows without relying on a developer’s laptop or custom infrastructure. The release also adds next-generation Kits as standard OCI images, giving organizations a portable way to package agent logic, tools, and access controls with consistent policies across local and cloud execution. #Docker #DockerCloudSandboxes #OCI #CNCF
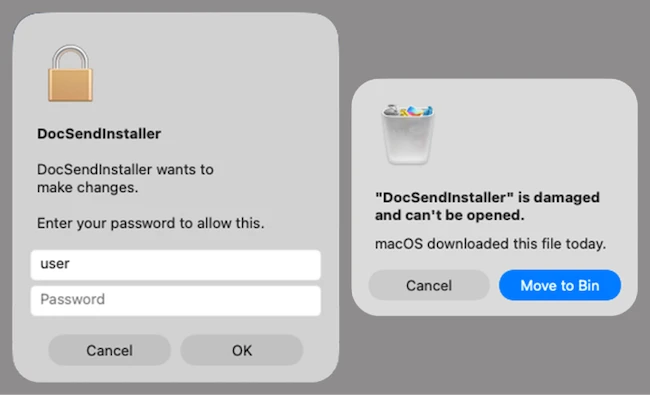
Kaspersky has uncovered a new MacSync variant that uses an infostealer and a persistent backdoor to steal credentials, crypto wallet data, files, and developer-related information from Mac users. The campaign spreads through a fake crypto wallet app called Toria and uses advanced infection chains, disguised prompts, and a backdoor posing as Finder to target developers and crypto enthusiasts. #MacSync #Kaspersky #Toria #Finder #Ledger #PAM #Keychain