
The report says roughly 1,280 third-party products now embed AI, but most agents remain invisible to identity infrastructure because they do not authenticate through traditional enterprise controls. It argues that agent security must focus on identity, permissions, connectivity, and activity, with platforms like Reco Graph providing a live view of human…
Daniel Rhyne, a former core infrastructure engineer, was sentenced to 32 months in federal prison for sabotaging his employer’s systems and attempting to extort 20 bitcoin from the company. The attack used scheduled tasks on a domain controller to disable accounts, change passwords across thousands of servers and workstations, and demand…

AnyTech365, a Spanish IT security and remote tech support provider, claimed it was targeted by ransomware activity attributed to thegentlemen in the UK. The incident impacted United Kingdom. #UnitedKingdom
Aquatech (US) reported a ransomware incident involving the threat actor “thegentlemen,” claiming that attackers accessed or encrypted company systems affecting its operations. Aquatech International Corporation is a US-based global water treatment technology provider (aquatech.com) with extensive international projects and operations. #UnitedStates
Saskatoon Tribal Council (STC) in Canada, a non-profit uniting seven First Nations with 14,000+ members and major operations in health, housing, and community development, reported a ransomware incident attributed to thegentlemen. The claim highlights potential impacts to its Canadian services and operations, including critical programs and administrative systems supporting Indigenous communities. #canada
The ransomware claim alleges that thegentlemen targeted D.W. McMillan Memorial Hospital (dwmmh.org) in Brewton, Alabama, US, causing disruption to a small rural hospital that provides 24/7 emergency care, ICU, surgery, obstetrics, outpatient chemotherapy, lab, imaging, and rehabilitation. The incident is described in the context of DW McMillan Memorial Hospital’s recent financial strain and ongoing recovery efforts within the county healthcare system. #UnitedStates
On fleetworksinc.com, the ransomware claim alleges the US-based Fleetworks Inc. was targeted by the threat actor threeam, potentially disrupting the company’s heavy-duty truck repair and fleet services across California. The impacted country is #UnitedStates
rhysida ransomware actors claimed to have compromised Anne Arundel County, a US governmental body established in 1964, by exfiltrating 814,500 files totaling 2.6 TB, including sensitive medical, background-check, and Methadone clinic records governed by strict confidentiality rules. The stolen data allegedly spans medical faxes (2022–2026), medical-assistance documents containing SSNs and financial information, payroll/HR records, and jail gang-intelligence files. #UnitedStates
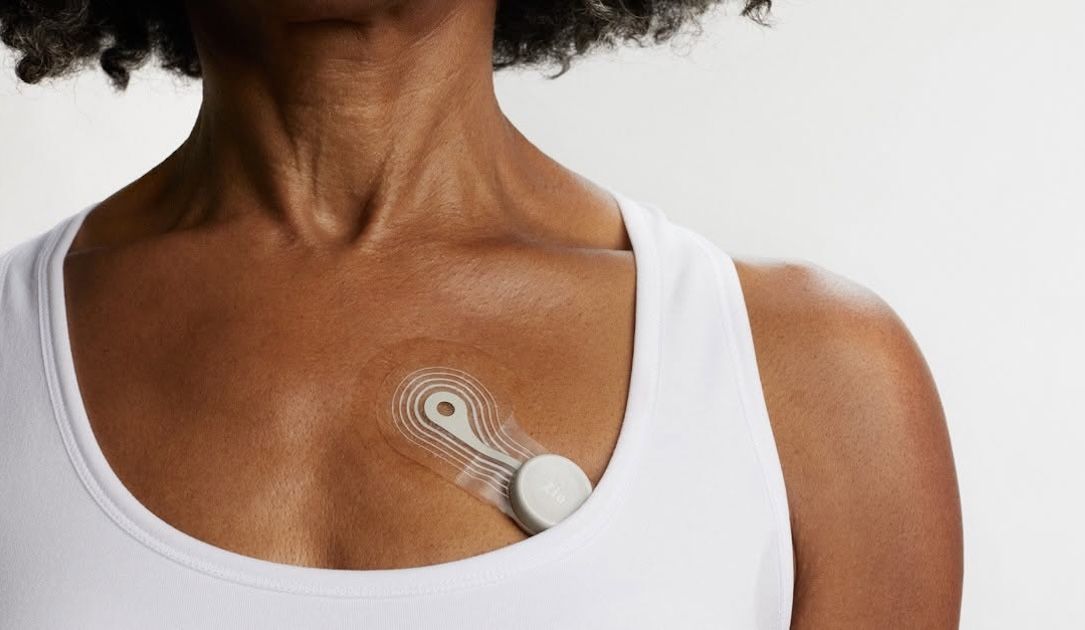
iRhythm disclosed that a June 8 cyberattack exposed the data of at least 360,000 people after attackers accessed third-party-hosted business applications through social engineering. The breach did not affect iRhythm clinical systems or medical devices, but it involved stolen patient and insurance information and followed a threat actor demand for payment….
Japan’s National Police Agency confirmed the arrest and extradition of a Russian national suspected of helping the Qilin ransomware gang in an attack on a German company. Qilin has remained highly active across Europe, Japan, and the U.S., with notable victims including Asahi, Die Linke, and the ATF. #Qilin #Asahi #DieLinke…

Researchers uncovered P7 DarkSword, a stealthier iOS exploit kit variant that adds on-device keychain and crypto-wallet theft along with two-way command-and-control communication. The kit has been used by multiple threat actors against targets in Saudi Arabia, Turkey, Malaysia, Ukraine, and China, while Censys also linked related infrastructure to Coruna and a…
Vadeto Group in Sweden reported a ransomware incident attributed to the qilin threat actor, with threats involving encryption and disruption of operations. The claim indicates data and system impact consistent with ransomware tactics in the impacted environment. #Sweden
Northshoresun.timesreview.com in the US was targeted by the settra threat actor, associated with the NEWSPAPER ransomware family, as part of a campaign continuing to compromise media organizations. The attack involved encrypting or disrupting access to files, impacting services for readers in the US #UnitedStates
The ransomware incident targeting solutend has been attributed to the Panzer threat actor, impacting a Bolivian technology company providing audiovisual systems, digital signage, interactive displays, and business computing solutions. The impacted country is #Bolivia
Panzer ransomware targeted Supreme Energy, an Indonesian renewable-energy company developing geothermal power projects, attempting to disrupt operations and compromise systems. The impacted country(s): #Indonesia