
Cisco warned that attackers are actively exploiting CVE-2026-76504, a critical zero-day in Cisco Catalyst SD-WAN Manager that can let a remote unauthenticated attacker use the API as the admin user. Cisco has released fixed versions and advised customers to restrict internet exposure, check for signs of compromise, and upgrade immediately. #CVE-2026-76504…

Microsoft warned of phishing campaigns that distribute a legitimate MSP360 Remote Monitoring and Management installer under deceptive lures such as meeting invitations, PDF-themed files, and software update prompts. After installation, the attackers use MSP360 and then ScreenConnect to maintain persistent remote access, collect credentials, and stage additional tools. #MSP360 #ScreenConnect #FaronicsDeployAgent…

Microsoft reported that threat actors exploited the patched Zimbra Collaboration Suite flaw CVE-2026-73570 to deploy web shells, gain persistence, and collect mailbox and authentication data across affected organizations. The activity also involved lateral movement, credential theft, and attempted exfiltration using tools such as Zimclient2 and AzCopy, prompting urgent patching and hardening…

Orth Automobile in Germany was targeted by the ransomware group “play,” as claimed by the threat actor. The incident impacted Germany. #Germany
Airtech Mechanical Services in the United States was claimed by the play ransomware threat actor to have been affected by a ransomware attack. The impacted country(s) is/are #UnitedStates
Titus in Germany was targeted by the play ransomware threat actor, resulting in malicious encryption and disruption of access to impacted files and systems. The incident is attributed to play, impacting Germany #Germany
Cisco has released security updates for CVE-2026-76504, a critical zero-day in Catalyst SD-WAN Manager that is being actively exploited to gain admin privileges. The flaw affects all deployments and lets unauthenticated attackers bypass authentication through crafted HTTP requests, with Cisco urging customers to upgrade and check logs for signs of compromise. #Cisco #CatalystSDWANManager #CVE202676504
CISA has warned about CVE-2026-84411, a critical pre-authentication integer underflow in MikroTik RouterOS that can allow unauthenticated attackers to execute code as root or trigger a denial of service with a single crafted request. The agency says no active exploitation is known yet, but it urges MikroTik router owners to restrict internet exposure, segment networks, and update affected systems. #CVE-2026-84411 #MikroTik #RouterOS
Google’s Mandiant and GTIG reported ongoing exploitation of NetScaler zero-days CVE-2026-88771 and CVE-2026-88772, which attackers used to gain root access and deploy web shells. The campaign, active since at least early September, affected organizations across multiple sectors in North America and Europe, with more than 100 victims potentially impacted. #CVE-2026-88771 #CVE-2026-88772…
WatchGuard released fixes for 15 vulnerabilities in Fireware OS, including CVE-2026-86131, a critical RCE flaw that could let a remote attacker controlling a VPN server execute commands as root on a Firebox appliance. The update also addresses multiple high-severity issues and recent Access Point flaws in WatchGuard AP, with no known…
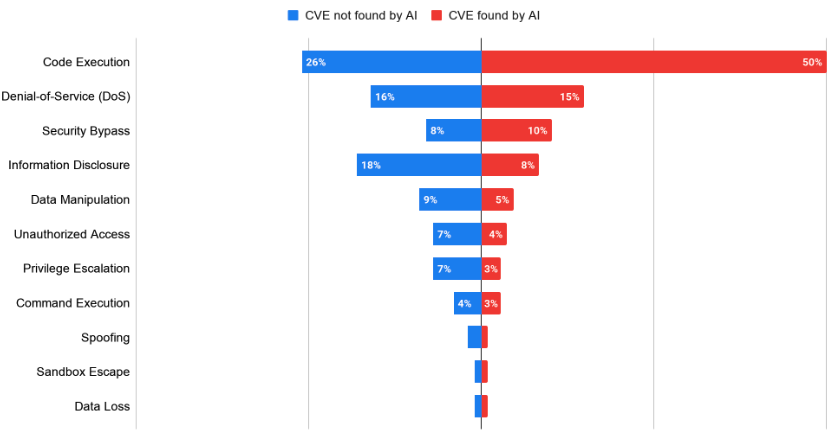
Google Threat Intelligence Group says vulnerability disclosures and real-world exploitation both surged in 2026, with AI increasingly affecting how flaws are discovered and weaponized. The report highlights faster n-day exploitation, more high-risk findings, and growing exposure in AI-related systems such as BeyondTrust Privileged Remote Access, LiteLLM, and Langflow. #GTIG #CVE-2026-1731 #BeyondTrust…
Ransomware claim targeting dfiretailgroup.com in the US by threat actor settra, advertising DFI RETAIL GROUP 27 years of email archives, 397 illegal stores, and 40,000 medical files. #UnitedStates
Threat actor emperador claims it breached SitePro Rentals and alleges no response has been received from the company, citing a law firm investigation into the incident. The claim includes threats to leak active employee details (72 hours to contact the attacker) and the data reportedly contains sensitive employee information, including SSNs and addresses. #countryname
The netrunner ransomware group allegedly targeted P***** M***** I** to encrypt files and disrupt operations. The impacted country(s): #Unknown

The City of Radford is dealing with an internet outage and service disruptions following a possible data incident that has affected several municipal departments. The city has brought in cybersecurity experts, legal advisers, and state and federal law enforcement as the investigation continues. #CityofRadford