UK health-tech firm Craneware (thecranewaregroup.com) claimed following the chaos ransomware attack that the incident exposed only “non-sensitive” data, including information they said was already public regulatory content. The breach and associated deception efforts were reported as affecting organizations in the United Kingdom. #UnitedKingdom
SSO improves convenience and centralizes access, but the 2025 University of Pennsylvania breach shows how a compromised PennKey account can expose many internal systems and large amounts of data. Strong passwords, phishing-resistant MFA, and tighter control over identity provider assets, certificates, OAuth secrets, and delegated permissions are essential to secure SSO. #UniversityofPennsylvania #PennKey #FIDO2 #WebAuthn #passkeys #SAML #OIDC

Oklahoma Manufacturing Alliance in the US reported that ransomware attributed to the Booba Project exfiltrated and stole 10 GB of data. The incident impacted #UnitedStates
Deadlock ransomware claimed to have targeted Pasello Trattamenti Termici Srl, an Italian specialist company for the heat treatment of metal alloys. The impacted country(s) is #Italy
The ransomware incident attributed to Threat Actor Deadlock involved DIATER, a Spanish biopharmaceutical company specializing in allergy diagnostics and allergen immunotherapy (ASIT), and impacted the organization’s systems and operations. The impacted country is #Spain
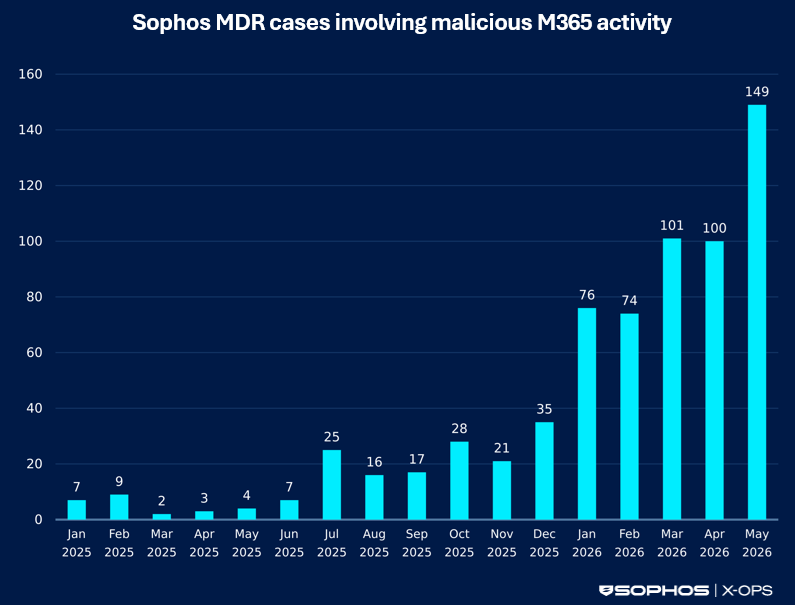
Sophos tracked STAC4749, a Microsoft Teams vishing campaign that impersonated IT support using themed cloud domains and personas to gain access to dozens of North American organizations. The operators used a modular backdoor toolset, remote access utilities, and evolving evasion tactics, with several intrusions ending in Chaos ransomware deployment. #STAC4749 #Chaos #MicrosoftTeams #Sophos #RemSupp #QuickAssist
Frenos raised an additional $1.52 million in seed funding, bringing its total to $6.4 million, with support from Momenta, Exposition Ventures, and Riptide Ventures. The OT security startup also launched SAIRA Co-Work, an AI reasoning agent that helps deliver evidence-based insights during complex investigations. #Frenos #SAIRACoWork #Momenta #ExpositionVentures #RiptideVentures…
Apple released major security updates across iOS, iPadOS, macOS, watchOS, tvOS, visionOS, and Safari, fixing hundreds of vulnerabilities that could enable sensitive data access, arbitrary code execution, privilege escalation, and other attacks. The most notable issue highlighted was CVE-2026-43810, which could allow remote kernel memory corruption, though Apple did not report…

Cyera has agreed to acquire Oasis Security in a $1 billion deal, combining data security with agentic access management for enterprise AI environments. The acquisition will unify identity and data security to govern what human users, machines, and AI agents can see and do across critical systems. #Cyera #OasisSecurity #AgenticAccessManagement…
Officials in Minnesota cities said cyberattacks targeted water systems in Braham, Plymouth, and South St. Paul, causing a temporary outage in Braham’s water system. The attacks were carried out by unknown actors targeting computerized systems. #Braham #Plymouth #SouthStPaul
Newton County Schools in Georgia took its systems offline after detecting unauthorized network activity shortly before the start of the school year. The district has brought in cybersecurity specialists to investigate and restore operations, while the nature of the incident and any possible data exposure remain unconfirmed. #NewtonCountySchools
Unitel, Angola’s telecommunications operator, was hit by a targeted cyberattack that disrupted voice, mobile data, and internet services nationwide. The company has mobilized its cybersecurity teams to reduce the impact, but the origin and nature of the attack have not yet been disclosed. #Unitel #Angola
More than 24,000 internet-exposed servers are leaking authentication password hashes because of CVE-2013-4786, an old IPMI 2.0 flaw in Baseboard Management Controller interfaces. Researchers also found evidence of weak factory and dictionary-based credentials, and an exposed HPE iLO 4 page showing a ransom note, suggesting active abuse of these systems. #CVE-2013-4786 #IPMI #BMC #Supermicro #HPEiLO4
Incredible Technologies in the US reported a ransomware incident involving the Booba Project threat actor, with 25 GB of entertainment provider data stolen. The claimed breach impacts the United States #UnitedStates
Deadlock ransomware targeted Takis srl, an Italian biotechnology company focused on contract research and development of genetic vaccines and therapeutic antibodies. The attack compromised the company’s systems and data, resulting in disruption and data theft risks. #Italy