Columbia University Information (Dental) in New York, US, reported ransomware activity targeting its 296 GB network footprint (283,387 files across 11,268 folders), with the threat actor “Global Secret Group” linked to the incident. The attack against a US higher-education institution utilizing columbia.edu impacted organizations and data in the United States. #UnitedStates

France’s tax authority, DGFiP, confirmed that hackers accessed its systems in late June and extracted data on individuals and businesses. The attack was later claimed by ZeroBytes, though the extent of the stolen information and the number of affected victims are still being investigated. #DGFiP #ZeroBytes #FrenchBreaches…
SOCRadar says most of the 2,500 organizations initially linked to the LiteLLM incident were actually exposed earlier through the TeamPCP-led Trivy compromise, which spread downstream across packages and CI/CD systems. The attack used a worm-like payload to steal credentials and secrets, and the collected data is now being brokered on Telegram….

SecurityWeek’s weekly roundup covers major cybersecurity developments, including a controversial Defense Department AI contract, a North Korean IT worker investigation, and new findings on Boeing 737 and commercial refrigeration system vulnerabilities. It also reports on LexisNexis probing a possible breach, Uber Freight investigating unauthorized access, CISA warning about Gunra ransomware, and…
Shell has confirmed it is investigating a potential security incident after the Clop gang claimed it stole 89GB of data, including engineering drawings, facility testing reports, photos, and project plans. The alleged theft is linked to attacks against Internet-exposed PTC Windchill and FlexPLM instances exploiting CVE-2026-12569, with Shell, General Electric, and Philips among the claimed victims. #Shell #Clop #PTC #Windchill #FlexPLM #CVE-2026-12569 #GeneralElectric #Philips
Defused says attackers are already targeting CVE-2026-58231, a critical unauthenticated RCE flaw in SAP Commerce Cloud that was patched just three days earlier. The issue affects a widely used e-commerce platform for major global brands, and Shadowserver has identified over 4,200 exposed SAP Commerce Cloud IPs worldwide. #CVE-2026-58231 #SAPCommerceCloud #Defused #Shadowserver
The Vercel and Composio breaches show a repeated attack pattern where stolen OAuth grants, not email, become the entry point into Google Workspace, enabling access to Gmail, Drive, and downstream systems. The same workspace chain can also be followed by AI agents operating with legitimate permissions, making full-chain defenses essential. #Vercel #Composio #GoogleWorkspace #OAuth
The Netherlands’ National Cyber Security Centre says CVE-2026-65400 in macOS Screen Sharing is being actively exploited after public exploit code appeared. Attackers are using exposed port 5900 to gain root access and install a Monero miner on affected systems. #CVE-2026-65400 #macOS #NCSC #Monero

Sweet Water Holdings was targeted by the ransomware threat actor coinbasecartel, which likely encrypted files and disrupted operations as part of its extortion activity. The impacted country(s): #countryname
Coinbasecartel ransomware actors claimed to have targeted Serruya Private Equity in Israel, alleging unauthorized access and data theft as part of their extortion demands. The impact is reported for #Israel
Turner and Townsend in GB is reported to have been targeted by the ransomware threat actor coinbasecartel, impacting its operations through malicious encryption. The impacted country is #UnitedKingdom
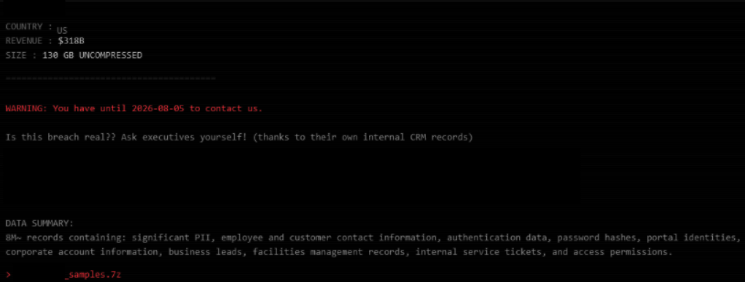
Starknex reported a widespread default-configuration exposure in Microsoft Dataverse and Microsoft Power Pages that could allow unauthenticated or guest users to read sensitive records, including Microsoft Entra ID user data, PII, documents, tickets, and portal credentials. The advisory also linked the issue to active threat actor activity by Exfilsquad, while detailing remediation steps such as Conditional Access, auditing, Web API shutdown, and table-permission reviews. #MicrosoftDataverse #MicrosoftPowerPages #Exfilsquad #BillGate
ShinyHunters claimed responsibility for a breach at RingCentral that exposed personal information from 1.6 million accounts, according to Have I Been Pwned. RingCentral said its core platform was not affected and that the incident stemmed from a sophisticated social engineering campaign, while the group allegedly leaked stolen data after the company refused to pay ransom. #ShinyHunters #RingCentral
Beacon said its recent breach likely began with a compromised AWS access key, allowing an attacker to export customer database backups from its CRM platform for charities and nonprofits. The incident may affect more than 1,000 customers, with some UK charities warning that supporter contact details were exposed, while no financial…
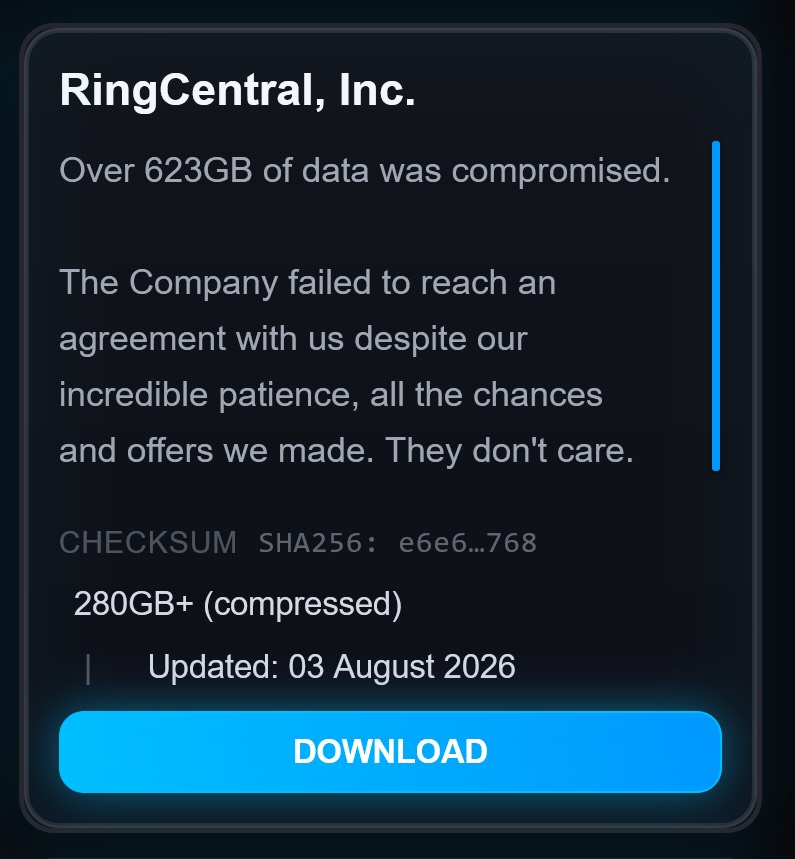
A data breach tied to RingCentral appears to have exposed personal information belonging to about 1.6 million individuals after a sophisticated social engineering campaign in July. The ShinyHunters extortion group later leaked stolen data that reportedly included email addresses, names, addresses, and phone numbers. #RingCentral #ShinyHunters #HaveIBeenPwned…