The French Ministry of the Economy and Finance disclosed a breach at DGFiP after an attacker using the ZeroBytes handle accessed and stole data tied to 678,000 individuals and professionals. The attacker also claimed access to the SPDC platform and offered stolen records for sale on PwnForums, adding to a wave of recent French government data breaches. #DGFiP #ZeroBytes #SPDC #PwnForums
General Electric and Philips are investigating claims that the Clop gang breached their systems and stole internal data, while Shell is also reviewing a separate alleged incident. The attacks are linked to exploitation of CVE-2026-12569 against PTC Windchill and PTC FlexPLM, which Clop has used to target enterprise platforms and steal sensitive files. #Clop #GE #Philips #Shell #PTC #Windchill #FlexPLM #CVE-2026-12569

A Vermont XCenter, no Brasil, foi alvo de ransomware alegadamente conduzido pelo grupo dragonforce, visando interromper e comprometer suas soluções de Contact Center e Tecnologia. A ação teria explorado a infraestrutura e os processos do Centro das Decisões da empresa para causar impacto e indisponibilidade aos sistemas afetados. #Brazil
Otter Tail County, Minnesota (US) reported a ransomware incident in which the threat actor incransom allegedly targeted its systems via https://ottertailcounty.gov/. The attack resulted in disruption to county operations and impacted services across the affected organization. #UnitedStates
Lloyd Coils Europe (GB) reported a ransomware incident involving the aurora threat actor, impacting its operations in the United Kingdom. As a Czech-headquartered heat exchanger manufacturer trading in the UK, the attack disrupted its international manufacturing and OEM customer support capabilities, with impact in #UnitedKingdom.

There were 3 defacement incidents in total, targeting sites in Indonesia and India. The attackers involved were D4LGH4CK_TM and Demon King. #Indonesia #India…
Twal Family IT Lab’s personal home lab in the twalfamily.com AD environment was impacted by the medusalocker ransomware, disrupting operations across VMware vSphere and multiple Active Directory domains. No evidence indicates a corporate/enterprise target, but prior reporting mistakenly referenced forces/forces.gc.ca, with the victim tied to Canada. #Canada
Threat actor settra allegedly compromised the corporate archives of tiltstudio.com in Germany and leaked data from an entertainment network, as described in “The Tilt Studio Archives Investigation of a Corporate Archive Leak from an Entertainment Network PRO.” The incident affected organizations and individuals by exposing sensitive archive material in #Germany
Ransomware claim targeting airoyal.biz by threat actor settra, where internal documents of an American industrial components distributor were reportedly taken and threatened for release. Impacted country(s): #UnitedStates
settra compromised galmack.com.ec (GALMACK S.A.) in Ecuador, accessing internal Prologue documents including monthly billings. The incident affected the victim in #Ecuador
Moores, a GB kitchen solutions provider for housing developers, reported a ransomware incident attributed to the bravox threat actor. The attacker reportedly compromised files and demanded a ransom, impacting Moores in the United Kingdom #UnitedKingdom
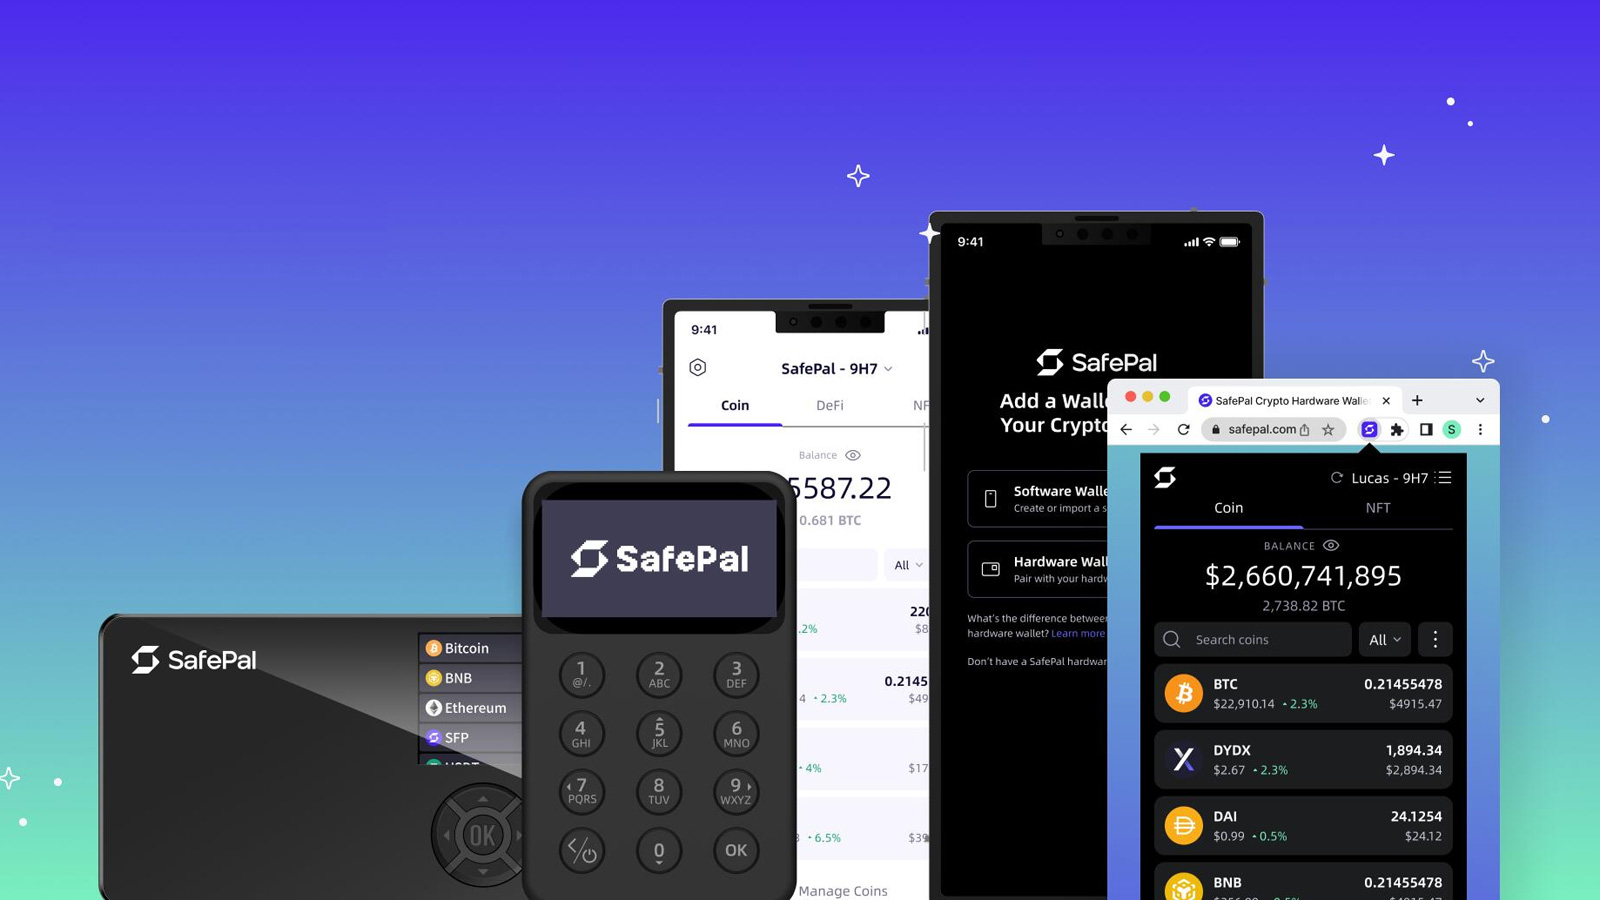
SafePal says a flaw in its order-tracking system exposed customer order details for about 39,798 customers and that a threat actor is now claiming to sell the stolen data. The company says wallet seed phrases, private keys, and funds were not compromised, but it warns the exposed information could be used for phishing and social engineering attacks. #SafePal #DarkWebInformer
WEBA Meubelen in Belgium was targeted by the qilin threat actor with ransomware that encrypted files and disrupted operations. The impacted country is Belgium#Belgium
Spoonful of Comfort in the US reported a ransomware incident allegedly linked to the qilin threat actor, resulting in unauthorized access and disruption of operations. The attack impacted #UnitedStates
Albania’s official national teacher training portal was targeted by the emperador ransomware threat actor, disrupting access to centralized professional development resources and accredited programs for educators nationwide. The leak reportedly includes approximately 100k full national ID numbers, full names, and teacher certificates in PDF, impacting Albania. #Albania