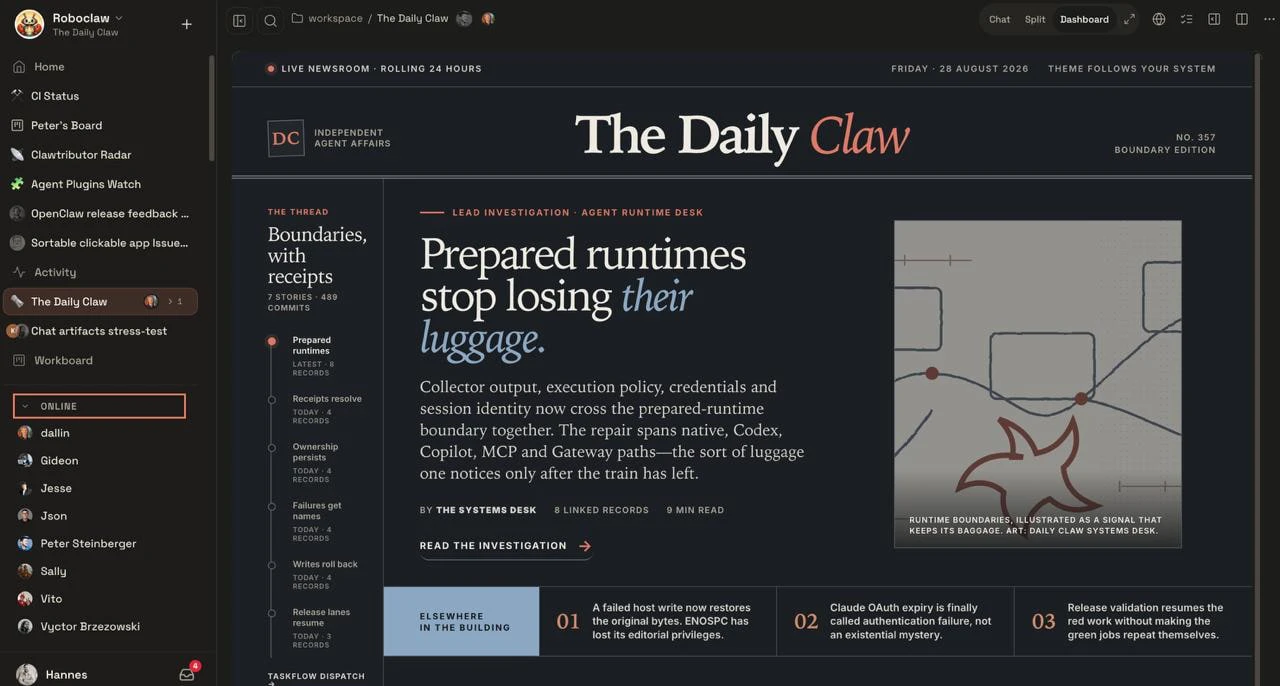
OpenClaw 2.0 is a major update that moves sessions and transcripts into SQLite, changes setup to verify existing AI credentials, and adds new controls for shared cloud sessions and incognito mode. The release improves startup performance and installation safety, but users should back up data before upgrading and remember that shared access is not a security boundary. #OpenClaw #SQLite #Codex #ChatGPT #Claude #Ollama #LMStudio

Absolute Consultancy Services in the UK reported a ransomware incident attributed to the qilin threat actor, resulting in disruption of access to company systems and data. #UnitedKingdom
The ATF confirmed that a standalone system was compromised after the Qilin ransomware gang listed the agency on its dark web leak portal. The agency says the incident did not affect its enterprise network, eForms system, or operations, and it is investigating the breach with the Department of Justice. #ATF #Qilin
Storm ransomware targeted Sprachakademie Rhein-Ruhr, a German language provider in Duisburg that has offered courses since 1995 and serves learners seeking study, university access, and visa support through telc exam center offerings. The impacted country(s) is Germany. #Germany

This week’s ThreatsDay Bulletin highlights a wave of social engineering, trojanized apps, phishing frameworks, stealer malware, botnets, and exposed systems being abused across Windows, Android, IoT, and cloud environments. From ReliaQuest and Microsoft Purview to ShinyHunters, Aeternum, ToxNetV2, and PackClient, attackers keep using trust, urgency, and weak visibility to gain access…
In a LockBit 5 ransomware incident affecting apatpa.com in Mexico (MX), American Plan Administrators was targeted with the threat of data exposure and service disruption. The claim involves smart, self-funded healthcare solution operations being compromised, impacting Mexico #Mexico
A Finnish appeals court revived the prosecution of three senior officers of the Russia-linked tanker Eagle S, ruling that Finland has jurisdiction over the Baltic Sea cable damage case. The court said the conduct fell outside “maritime accident” protections and highlighted the wider implications for undersea infrastructure and the related Estlink…
Globus Medical in the United States reported a Falcon ransomware incident targeting medical device related Microsoft Power BI data, claiming the extraction of 2.96 TB including sensitive records such as customer data, FDA and 510(k)/PMA materials, adverse event narratives, CAPA investigation findings, and distribution and merger diligence documents. The stolen/compromised data is alleged to include regulatory, clinical, and corporate records related to patient demographics and histories, ending with #UnitedStates.
Crystalpharmatech was targeted by the Qilin ransomware group, with attackers executing an extortion-and-encryption scheme to disrupt operations. The impacted country(s): #N/A
DistributionNOW (DNOW Inc.), US, reports a Falcon ransomware intrusion in which attackers exfiltrated 344 GB of corporate and operational data, including bank statements, vendor payment instructions, payroll and tax records, employee PII, SCADA/PLC backups, and internal audit and whistleblower documentation. The organization states the theft spans energy and industrial distribution assets, potentially affecting industrial operations and sensitive governance records in #UnitedStates
Globus Medical in the US reports a ransomware incident in which threat actor Falcon allegedly exfiltrated 2.96 TB of data from its medical device-related systems, including Microsoft PowerBI records and extensive regulatory and clinical documentation such as FDA feedback, 510(k)/PMA materials, CAPA findings, and serious adverse event narratives. The claimed theft also includes merger and FTC antitrust review documents, financial and deal models, patient demographics from clinical registries, and other sensitive business and partner agreements. #UnitedStates
The Wallstreet ransomware threat targeted the Town of Andover, Massachusetts, a municipal government organization responsible for providing public services, administration, community programs, education resources, infrastructure support, and civic information to residents and businesses. The attack disrupted municipal operations and services, impacting operations in the #UnitedStates.
qilin ransomware targeted AFSARD in MK, encrypting files and disrupting operations to extort payment. The incident impacted #NorthMacedonia
FulcrumSec claimed responsibility for the Manchester Airports Group data breach and said it stole about 86 GB of information, including detailed customer, booking, and upcoming travel records. BleepingComputer’s review suggested the exposed data was broader than MAG first disclosed and could be used for convincing phishing or scam attempts against travelers. #FulcrumSec #ManchesterAirportsGroup #MAG

Sanko Techno announced that its Vietnamese subsidiary, Sanko Fastem, was affected by a cybersecurity incident. The company is investigating the impact on its manufacturing operations and related systems. #SankoTechno #SankoFastem