Threat actors are actively exploiting CVE-2026-9586, a critical unauthenticated SQL injection flaw in Sangoma Switchvox that can lead to remote code execution. Horizon3 and CISA have confirmed exploitation in the wild and added the issue to the KEV catalog alongside other recently abused vulnerabilities in Starlette, Kestra, and LiteLLM. #CVE-2026-9586 #SangomaSwitchvox…
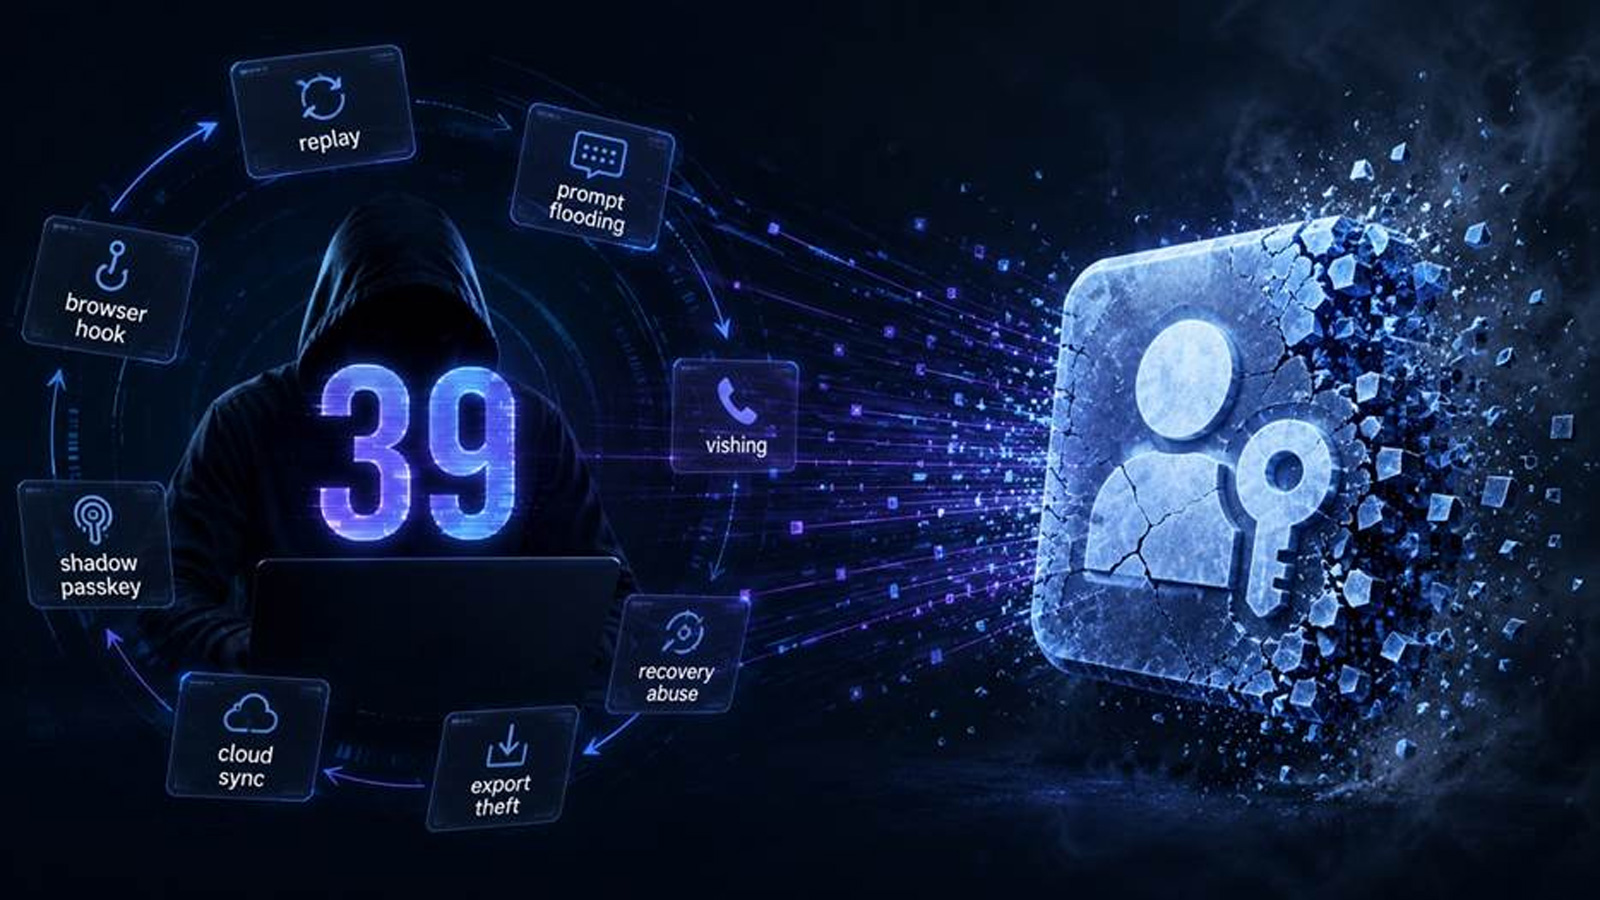
Passkeys strengthen authentication with public key cryptography, but 39 publicly documented attack methods show that threats now focus on the surrounding software, enrollment, recovery, and user-interface layers. Dedicated biometric hardware, combined with strict service configuration, can greatly reduce the attack surface and better protect enterprise identities. #SpecterOps #PassThePasskey #FIDO2 #WebAuthn #Token
Microsoft is working to fix a known issue that can delay or block some users from opening the Microsoft Teams desktop client on Windows, with affected users advised to use the web or mobile apps as a workaround. The company is also investigating a separate Mac issue that can prevent users from joining Teams calls and meetings, while continuing to review logs and telemetry to identify the root causes. #MicrosoftTeams #TM1466820 #TM1466659

Plex is urging users to update Plex Media Server and Plex Desktop after releasing fixes for multiple security flaws, with CVE identifiers still pending. The alert follows past Plex issues, including CVE-2025-34158 and CVE-2020-5741, which were tied to account exposure and the LastPass breach. #Plex #PlexMediaServer #PlexDesktop #CVE-2025-34158 #CVE-2020-5741 #LastPass…

Wordfence says threat actors are exploiting critical file upload flaws in the Super Forms and Elementor Pro WordPress plugins, with both issues enabling unauthenticated remote code execution. Site owners are urged to patch immediately, check for compromised PHP files, and review their installs for signs of abuse linked to Mushr00w_upl.php and…

Google released Chrome 152 security updates that fix 12 vulnerabilities, including CVE-2026-85046, a high-severity zero-day in the V8 JavaScript and WebAssembly engine that is already being exploited in the wild. The release also addresses nine other high-severity flaws and two medium-severity issues across Windows, macOS, and Linux. #Chrome #CVE-2026-85046 #V8…

Rand Water, South Africa’s largest water utility, confirmed a cybersecurity incident affecting some of its computer systems, but said critical operations such as water treatment, quality control, and bulk supply remain fully operational. The incident was disclosed to Rand Water’s debt holders on 2026-09-03, and the company stated that water quality has not been affected. #RandWater
The State Legal Council was hit by a cyberattack carried out by an unknown hacker group that demanded a cryptocurrency ransom to return database files. The incident is being treated as one of the most significant attacks against a public body in Greece in recent months, with the investigation led by the Electronic Crime Directorate and Europol. #Europol #ElectronicCrimeDirectorate

Complete Packaging Solutions was hit by the qilin ransomware, resulting in encrypted files and disruption to business operations. The impacted country(s) is: #countryname
EDIF S.p.A. in Italy, a wholesale distributor of electrical equipment, plumbing, and lighting systems, was targeted by the aurora ransomware threat actor, resulting in exposed internal data and compromised credentials. The breach includes passwords and transfers for customer systems, certified email and warehouse device information, leaked copies within source code and setup packages, and sensitive customer/employee records such as invoices, tax IDs, addresses, shipment details, and related logs, exposing files tied to Italian operations. #Italy
Occidental in Venezuela reported a ransomware incident attributed to the gunra threat actor, disrupting operations and triggering response and recovery activities. The reported exposure involves the Insurance sector with estimated revenue at US$ 157,000,000, impacting Venezuela #Venezuela

August 2026 Patch Tuesday delivered 398 resolved CVEs, highlighting the ongoing Patch Apocalypse and the pressure created by rapid AI-driven vulnerability discovery. SharePoint, Exchange Server, Azure Arc, Microsoft Defender, and Chrome all featured high-risk issues, including actively exploited and publicly disclosed flaws that demand fast patching and layered network defenses. #SharePoint #ExchangeServer #AzureArc #MicrosoftDefender #Chrome #ShieldBreak #CVE-2026-55040 #CVE-2026-63520 #CVE-2026-62911 #CVE-2026-69414 #CVE-2026-85046
Microsoft Teams is adding a safeguard that obscures QR codes sent by external users, requiring people to reveal them before viewing or scanning. The change, expected to roll out in October 2026, aims to reduce QR code phishing and fraud by slowing down risky interactions. #MicrosoftTeams #Microsoft365Roadmap

The 2025 VPN Exposure Report finds that traditional VPNs are increasingly risky and operationally unsustainable, with organizations facing frequent attacks, poor user experiences, and growing confidence in Zero Trust alternatives. Key trends include the rise of VPN-related breaches, the adoption of ZTNA and SSE, and the shift toward replacing VPNs entirely in modern remote access strategies. #Ivanti #ConnectSecure #ZTNA #SSE #ZeroTrustNetworkAccess #SecurityServiceEdge
Thomson Reuters disclosed a breach of its C-Track court records platform that exposed sealed court information and sensitive personal data across at least 12 U.S. states, the U.S. Virgin Islands, and Canada. The company said the intrusion occurred within its own environment, affected data may include Social Security numbers and medical…