
Check Point Research reported that a single hidden instruction in a ChatGPT conversation could make ChatGPT silently exfiltrate data from a user’s connected Gmail and conversation context while still replying normally. The researchers said the issue used a hidden communication channel between ChatGPT containers via internal JFrog Artifactory metadata, and that…

The Liquid Network suffered a major incident in which nearly 4,000 bitcoin were withdrawn from its federation wallet, prompting a pause of the sidechain and concern over L-BTC backing. After on-chain negotiations, 3,400 bitcoin were returned, while about 598.5 bitcoin remains unreturned amid debate over whether the actors were white hats…

The ransomware incident targeted cannonpuntana.com in Argentina, with Threat Actor safepay claiming responsibility, affecting an enterprise historically connected to the manufacture and distribution of fragrances, toiletries, and personal-care products. The attack disrupted operations and data availability for the victim in #Argentina
The ransomware claim targets reichenau.at in Austria, attributed to the threat actor safepay. The official website, reichenau.at, serves as the municipality’s central digital information and service platform for residents, businesses, and visitors. #Austria
Ransomware by safepay targeted palmettoeyeinstitute.com in the US, impacting the ophthalmology practice founded by Dr. Prat Itharat, a board-certified cataract surgeon and provider of comprehensive eye care. The incident disrupted operations and threatened data availability, culminating in consequences for patients and staff in #UnitedStates
GT Distributors in the United States reported a ransomware incident involving the threat actor play, resulting in unauthorized access and disruption of operations. The affected systems and data were impacted by the attack, United States #UnitedStates
Red Star Oil in the United States was targeted by the play ransomware group, resulting in an attack impacting the organization’s systems and data availability. The incident reportedly involved encryption and disruption of operations affecting the victim. #UnitedStates

A previously undocumented threat actor called Slim Spider has been targeting Brazilian financial institutions since at least March 2026, with a focus on cloud environments, cryptocurrency assets, and Pix payment infrastructure. CrowdStrike also linked Slim Spider and Breeze Comet to sophisticated operations that steal credentials, deploy backdoors, and abuse Brazilian payment…

Adobe has released fixes for more than 170 vulnerabilities across its products, including a critical zero-day in Adobe Commerce and Magento Open Source that was actively exploited in the wild. The exploited flaw, tracked as CVE-2026-75650 and dubbed StyleSmuggler, enabled unauthenticated remote code execution, prompting urgent guidance to patch systems and…
Microsoft’s September 2026 Patch Tuesday addresses a record 974 CVEs, including two zero-days in Windows ALPC and the Windows Update Stack that can let local attackers gain SYSTEM privileges. The update also fixes major flaws in Exchange Server, SharePoint, SQL Server, Remote Desktop Services, and other Microsoft products, with several issues…
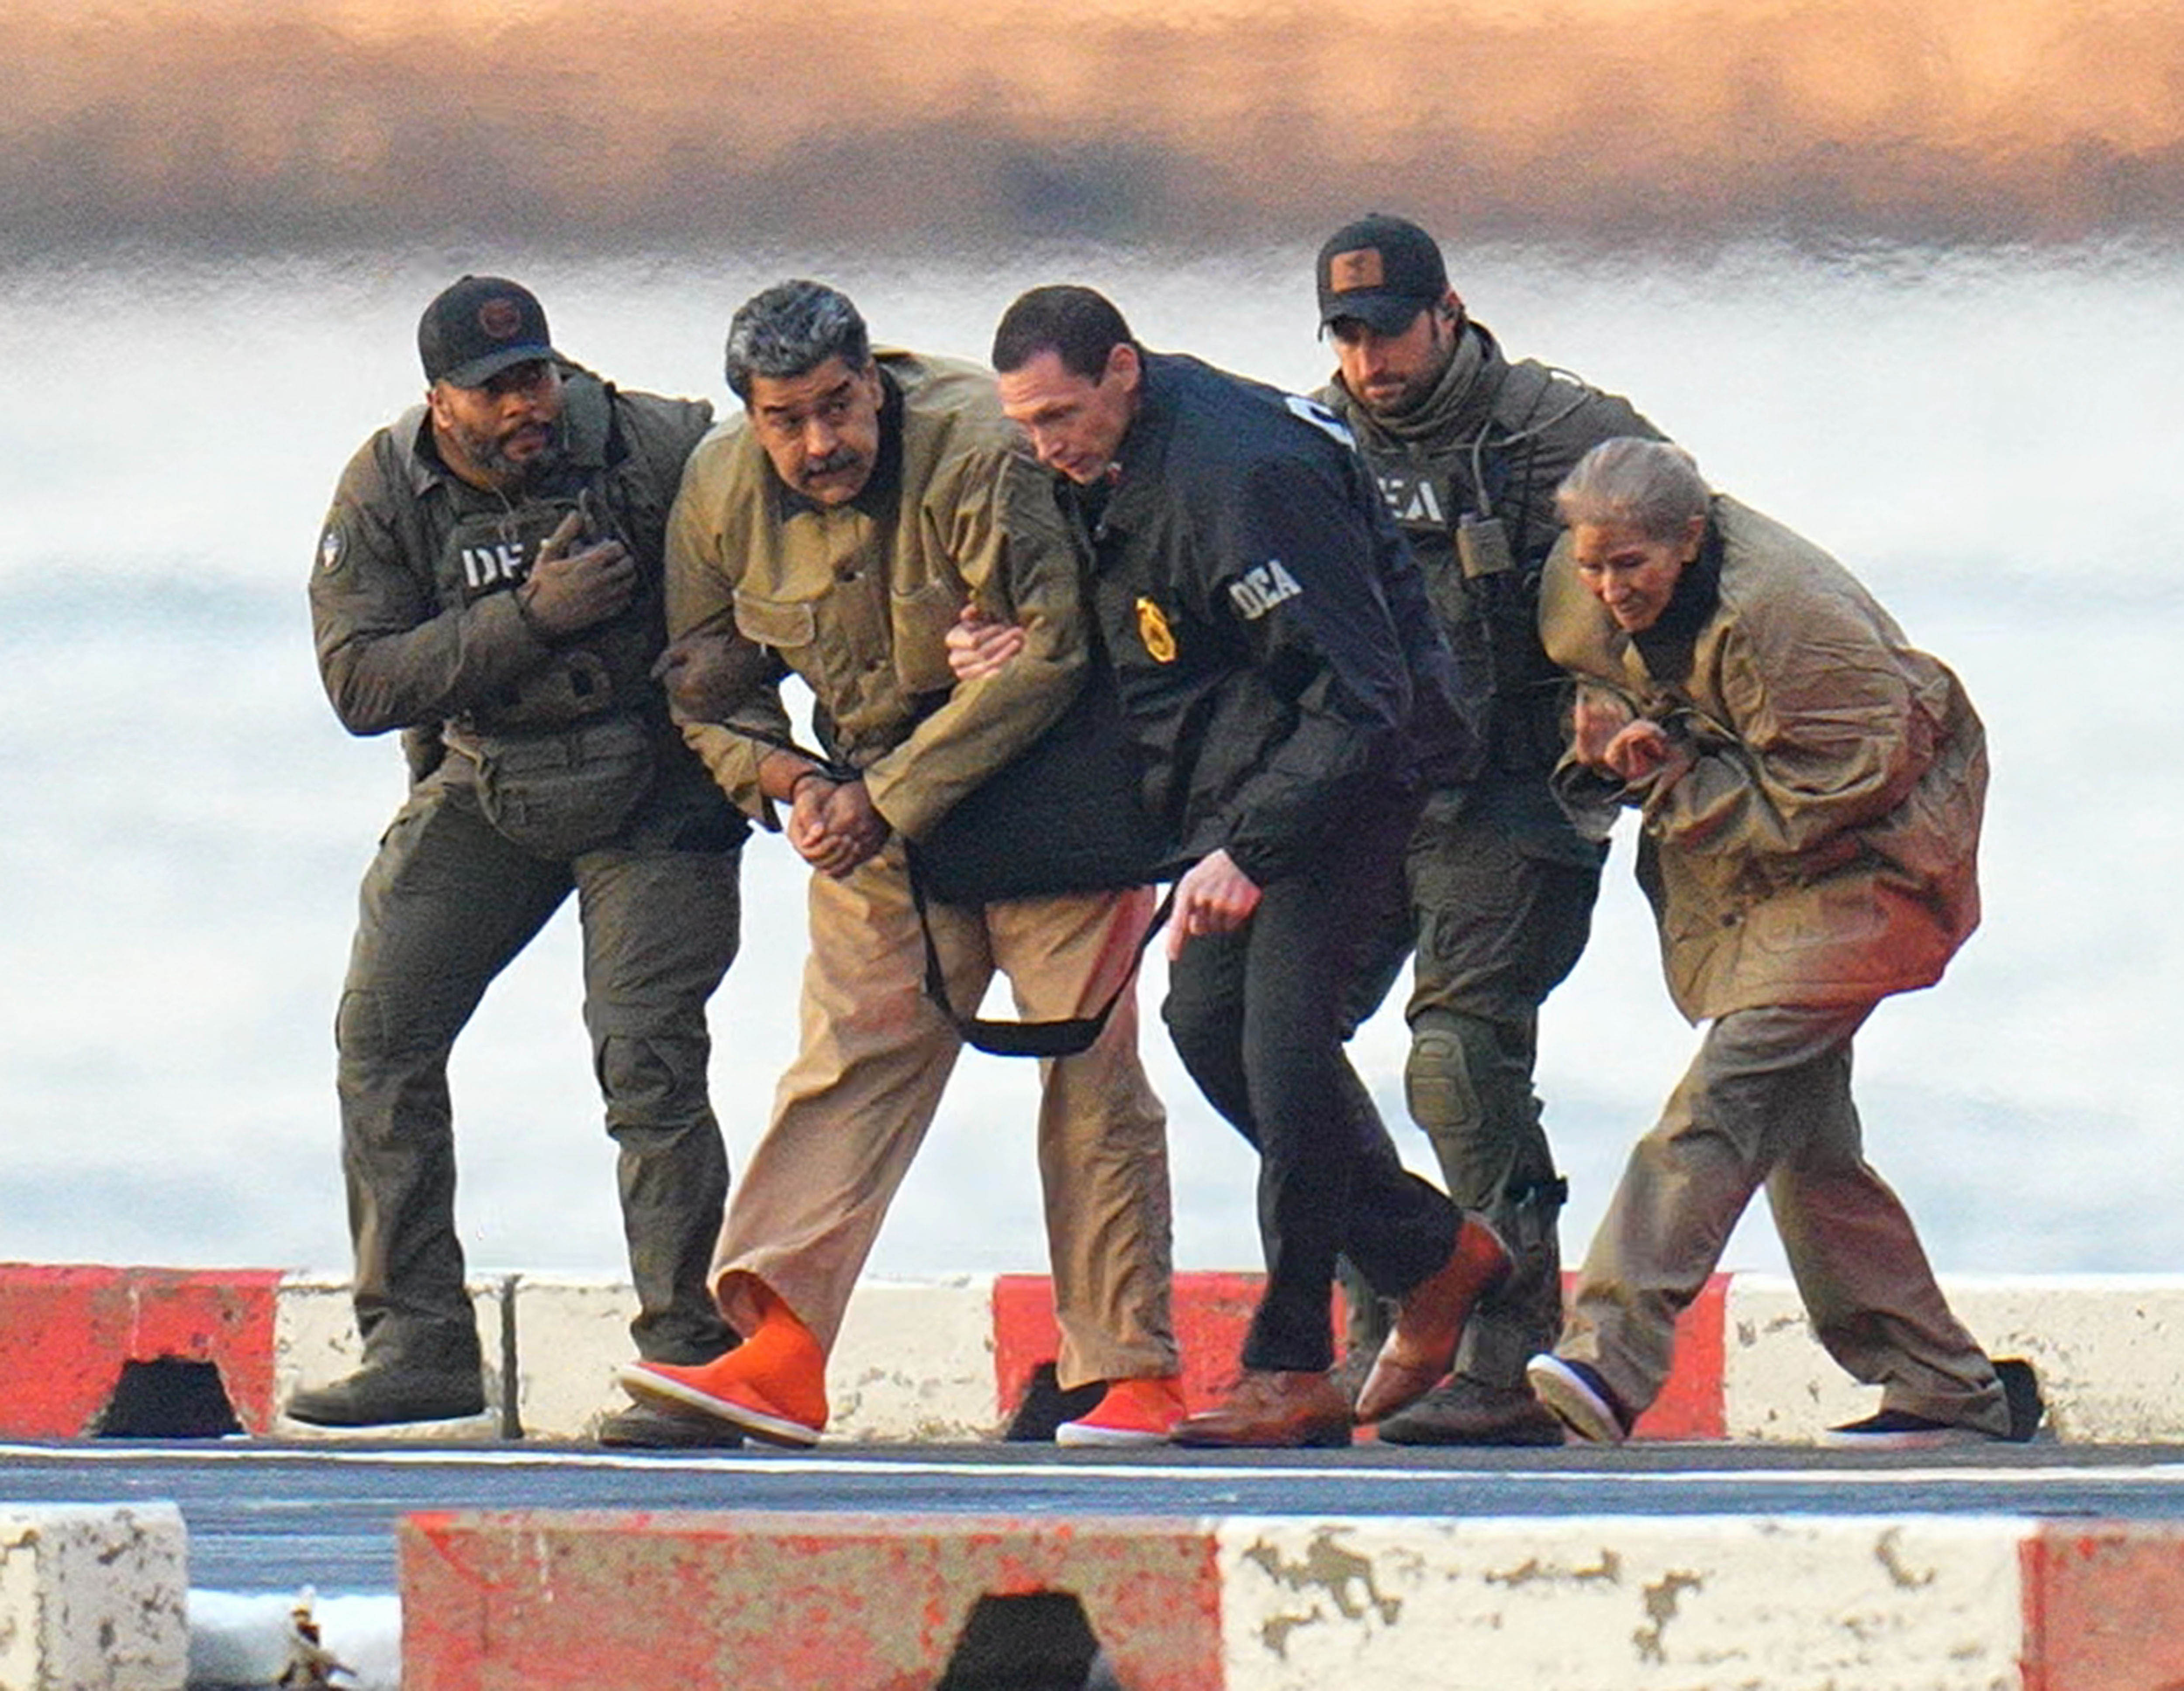
CIA Deputy Director Michael Ellis said Operation Absolute Resolve shows cyber operations are now central to intelligence collection and mission execution, helping U.S. forces locate and apprehend Nicolás Maduro. He also highlighted the CIA’s reorganization to elevate its Center for Cyber Intelligence and speed technology delivery through its new Directorate of Mission Systems. #CIA #OperationAbsoluteResolve #NicolásMaduro #CenterforCyberIntelligence #JohnRatcliffe

Authorities extradited Sergei Anatolyevich Filimonov from Georgia over an alleged bank-account takeover scheme that targeted victims through spoofed bank domains and stole more than 5,000 login credentials. Prosecutors say the operation attempted to divert millions from two banks, with alleged losses exceeding $6.3 million and possible attempted losses far higher. #SergeiAnatolyevichFilimonov #NorthernDistrictOfGeorgia #FBI #Atlanta #Cumming
The U.S. government says Chinese AI firms are running a systematic campaign to distill capabilities from frontier U.S. models, using billions of tokens and millions of exchanges since late 2024. The advisory names DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun, and Z.AI, and says the companies used the resulting data to strengthen domestic models while trying to avoid detection. #DeepSeek #MoonshotAI #Alibaba #MiniMax #StepFun #ZAI #Claude #ChatGPT #Gemini #Grok
Microsoft’s September 2026 Patch Tuesday is its largest ever, fixing 966 flaws and two actively exploited zero-days, CVE-2026-81963 in the Windows Update Stack and CVE-2026-85880 in Windows ALPC. The update spans major products including Windows, Office, SQL Server, Exchange Server, Entra ID, Azure services, and Microsoft Edge, with 105 Critical vulnerabilities addressed overall. #WindowsUpdateStack #WindowsALPC #EntraID #MicrosoftExchangeServer #MicrosoftOffice #SQLServer #MicrosoftEdge
Microsoft has released Windows 10 KB5122878 for ESU and Enterprise LTSC users, bringing September 2026 Patch Tuesday security fixes and several bug fixes. The update advances systems to build 19045.7725 or 19044.7725 and includes corrections for Secure Boot, Morocco Standard Time, OMA DM logging, Windows Code Integrity policies, Remote Desktop audio redirection, and a BitLocker Group Policy issue. #Microsoft #Windows10 #KB5122878 #PatchTuesday