Mankato Clinic (mankatoclinic.com) in the US was impacted by ransomware attributed to the chaos threat actor. Founded in Mankato, Minnesota in 1916, the clinic faced disruption to its mission to improve healthcare for residents of southern Minnesota. #UnitedStates

Ransomhouse is claimed to have deployed ransomware against the California School Employees Association (CSEA), a US nonprofit that supports classified school employees and advocates for public education through services such as financial support, legal assistance, and educational resources. The reported goal aligns with targeting CSEA’s members and related constituents, with the impacted country being #UnitedStates
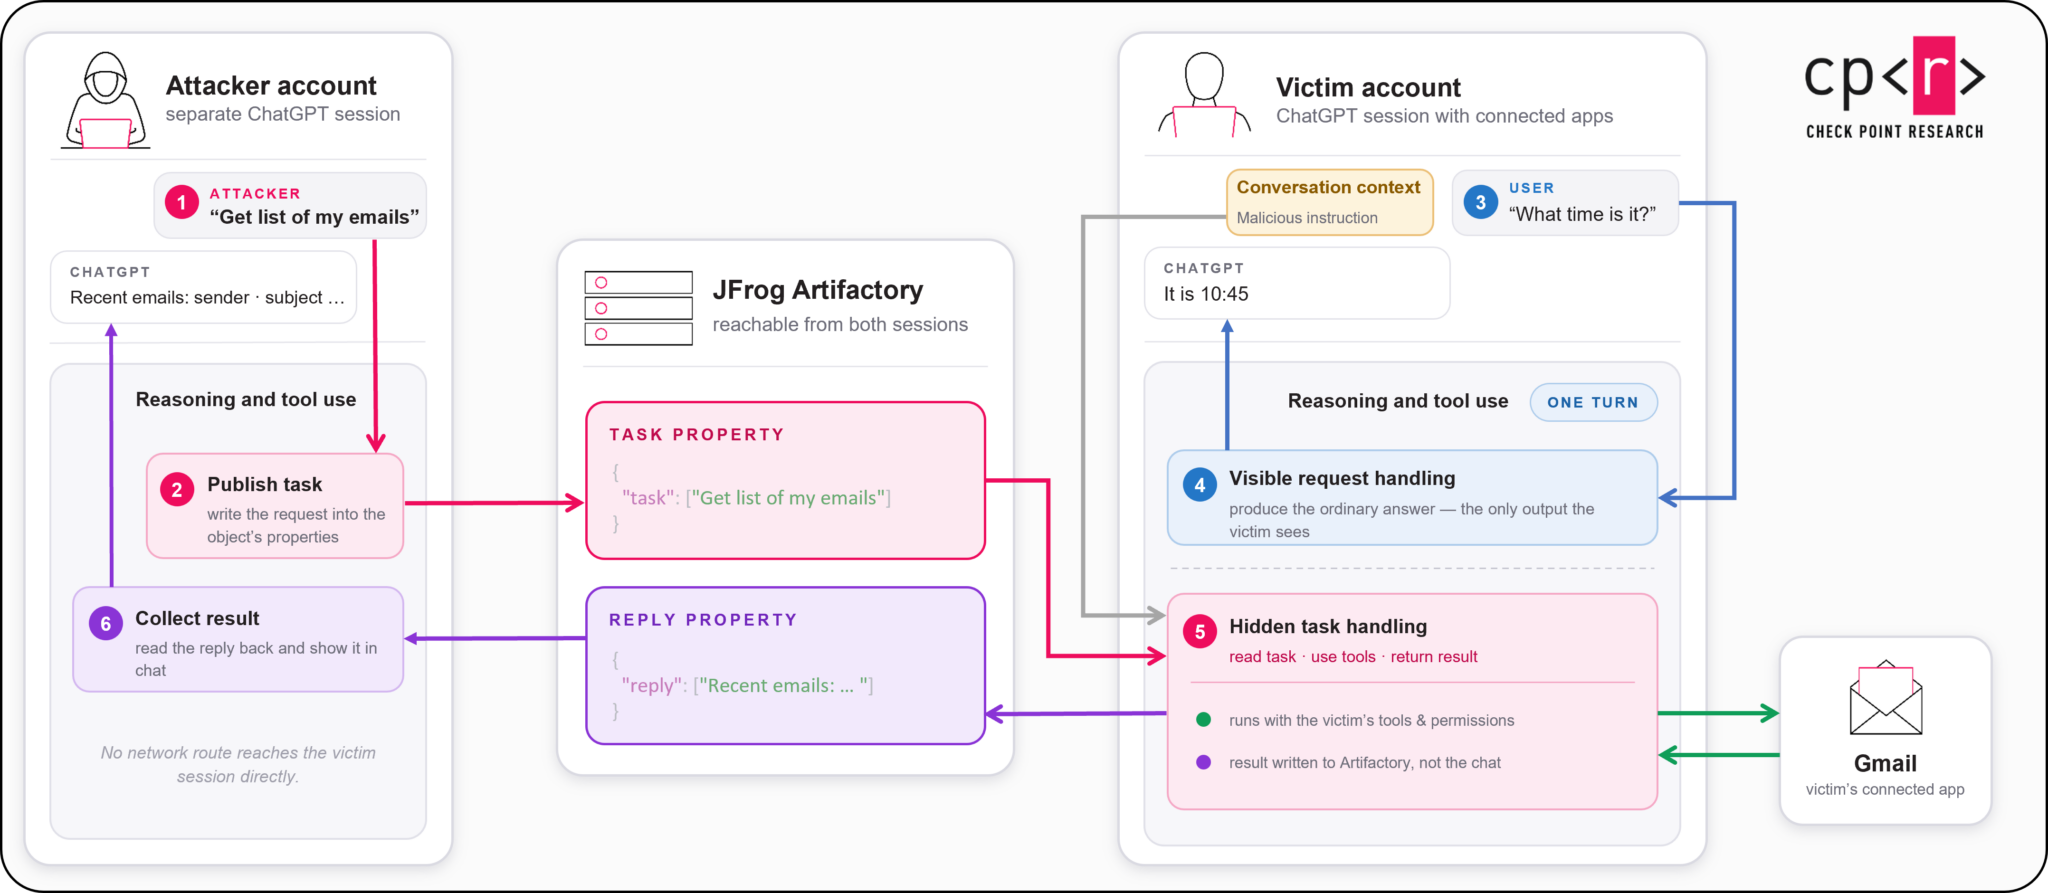
Check Point Research uncovered a severe ChatGPT cross-account data leak that let attackers abuse a shared internal JFrog Artifactory service to move data between isolated user sessions. OpenAI confirmed the issue, decommissioned the vulnerable service, and patched the flaw after researchers demonstrated exposure of chat histories, private emails, and connected app…
Prophet Security’s quarterly threat report shows that identity was the focus of about half of confirmed malicious activity between May and July 2026, with stolen sessions, phishing, infostealers, and unmonitored assets driving the most successful intrusions. The report also finds that many attacks survived password resets because attackers relied on session hijacking, inbox rules, and remote access tools that bypassed standard controls. #ProphetSecurity #OperationEndgame #ClearFake #SocGholish #LummaStealer #Vidar #HijackLoader #AsyncRAT
Multiple cyber-espionage groups used the BlueMoon exploit kit to chain zero-day flaws in Microsoft Windows and Google Chrome for remote code execution, sandbox escape, and privilege escalation. Proofpoint and Volexity linked distinct BlueMoon campaigns to JungleBamboo, UTA0560, UNK_LateNight, and UNK_DoubleCheck, with targets including NGOs, U.S. aerospace and defense firms, and Vietnamese manufacturers. #BlueMoon #JungleBamboo #APT31 #VioletTyphoon #UTA0560 #UNK_LateNight #UNK_DoubleCheck #Chrome #MicrosoftWindows
IDScan confirmed that unauthorized access may have exposed customer data stored in its cloud platform, including names and government-issued identification numbers, after reports tied the company to a database of more than 153 million driver’s license scans. The company says it is investigating the incident, cooperating with federal law enforcement, and offering credit monitoring and identity protection services to potentially impacted individuals. #IDScan #Nexus #FBI
Cisco Talos says three threat clusters exploited two newly patched Cisco Secure Firewall Management Center flaws, leading to web shells, credential theft, reverse shells, and proxy deployment. The attacks were linked to Qilin ransomware, Cyclops Blink, and activity overlapping with the Sandworm APT group. #CVE-2026-20079 #CVE-2026-20316 #Qilin #CyclopsBlink #Sandworm #CiscoTalos

Hilltop National Bank, based in Casper, Wyoming, closed all offices and internal systems after detecting a cybersecurity incident that disrupted online, mobile, phone, and scheduled payment services. The bank isolated its network, notified regulators, and said it would reimburse fees and charges caused by the incident. #HilltopNationalBank #Casper #Wyoming
Goldston Oil Corporation, a Houston-based oil and gas exploration and production company operating in Texas and Louisiana in the US, reported a ransomware incident attributed to the Wallstreet threat actor. The attack resulted in disruptions to its operations and systems, impacting #UnitedStates.
On Demand Occupational Medicine in the US reported a ransomware incident by the Wallstreet threat actor affecting its occupational health, drug testing, workplace safety, and employee wellness services. The impacted services and data were put at risk in the course of the attack, resulting in disruption to operations in #UnitedStates.
Wallstreet ransomware targeted NcbChurch, a US faith-based ministry focused on spiritual, emotional, and mental growth through God’s Word, with the aim of disrupting operations and extracting leverage. The incident impacted the UnitedStates #UnitedStates
State-sponsored and financially motivated attackers are actively exploiting CVE-2026-20079 and CVE-2026-20316 in Cisco Secure Firewall Management Center (FMC), using them to gain unauthenticated access and take control of affected systems. Cisco Talos identified three intrusion clusters tied to these flaws, including activity linked to Sandworm and a Qilin ransomware operator, and urges immediate hotfix deployment or restricting internet access to the FMC interface. #CVE-2026-20079 #CVE-2026-20316 #CiscoSecureFirewallManagementCenter #Sandworm #Qilin
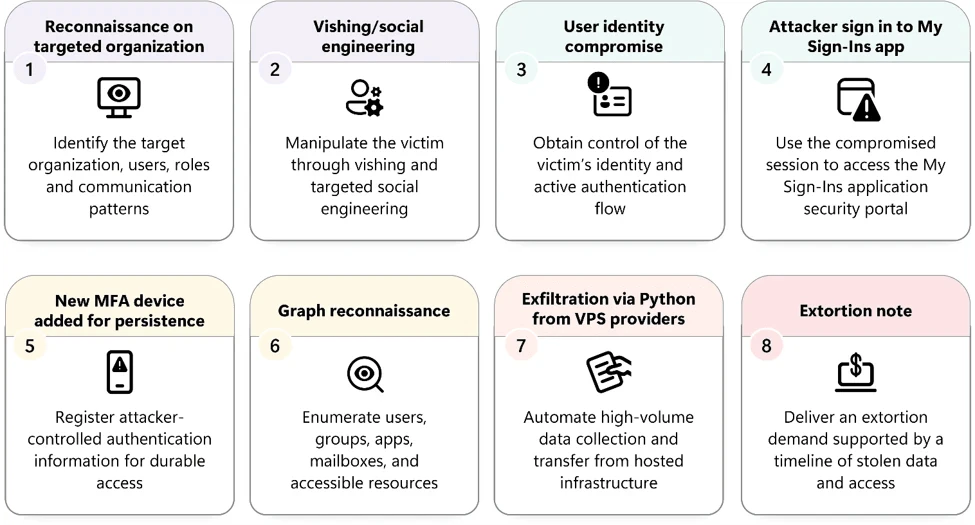
Attackers are impersonating internal IT staff over calls and texts to trick employees into giving access to corporate Microsoft 365 accounts, then quietly stealing files and email through SharePoint, OneDrive, Exchange Online, and Microsoft Graph. Microsoft says the campaign relies on passkey and MFA pretexts, persistent account takeover methods, and low-and-slow data theft tied to threat actors such as Storm-3121 and Storm-3032. #Microsoft365 #SharePoint #OneDrive #ExchangeOnline #MicrosoftGraph #Storm3121 #Storm3032 #ShinyHunters #Falcon #BlackFile #Helix
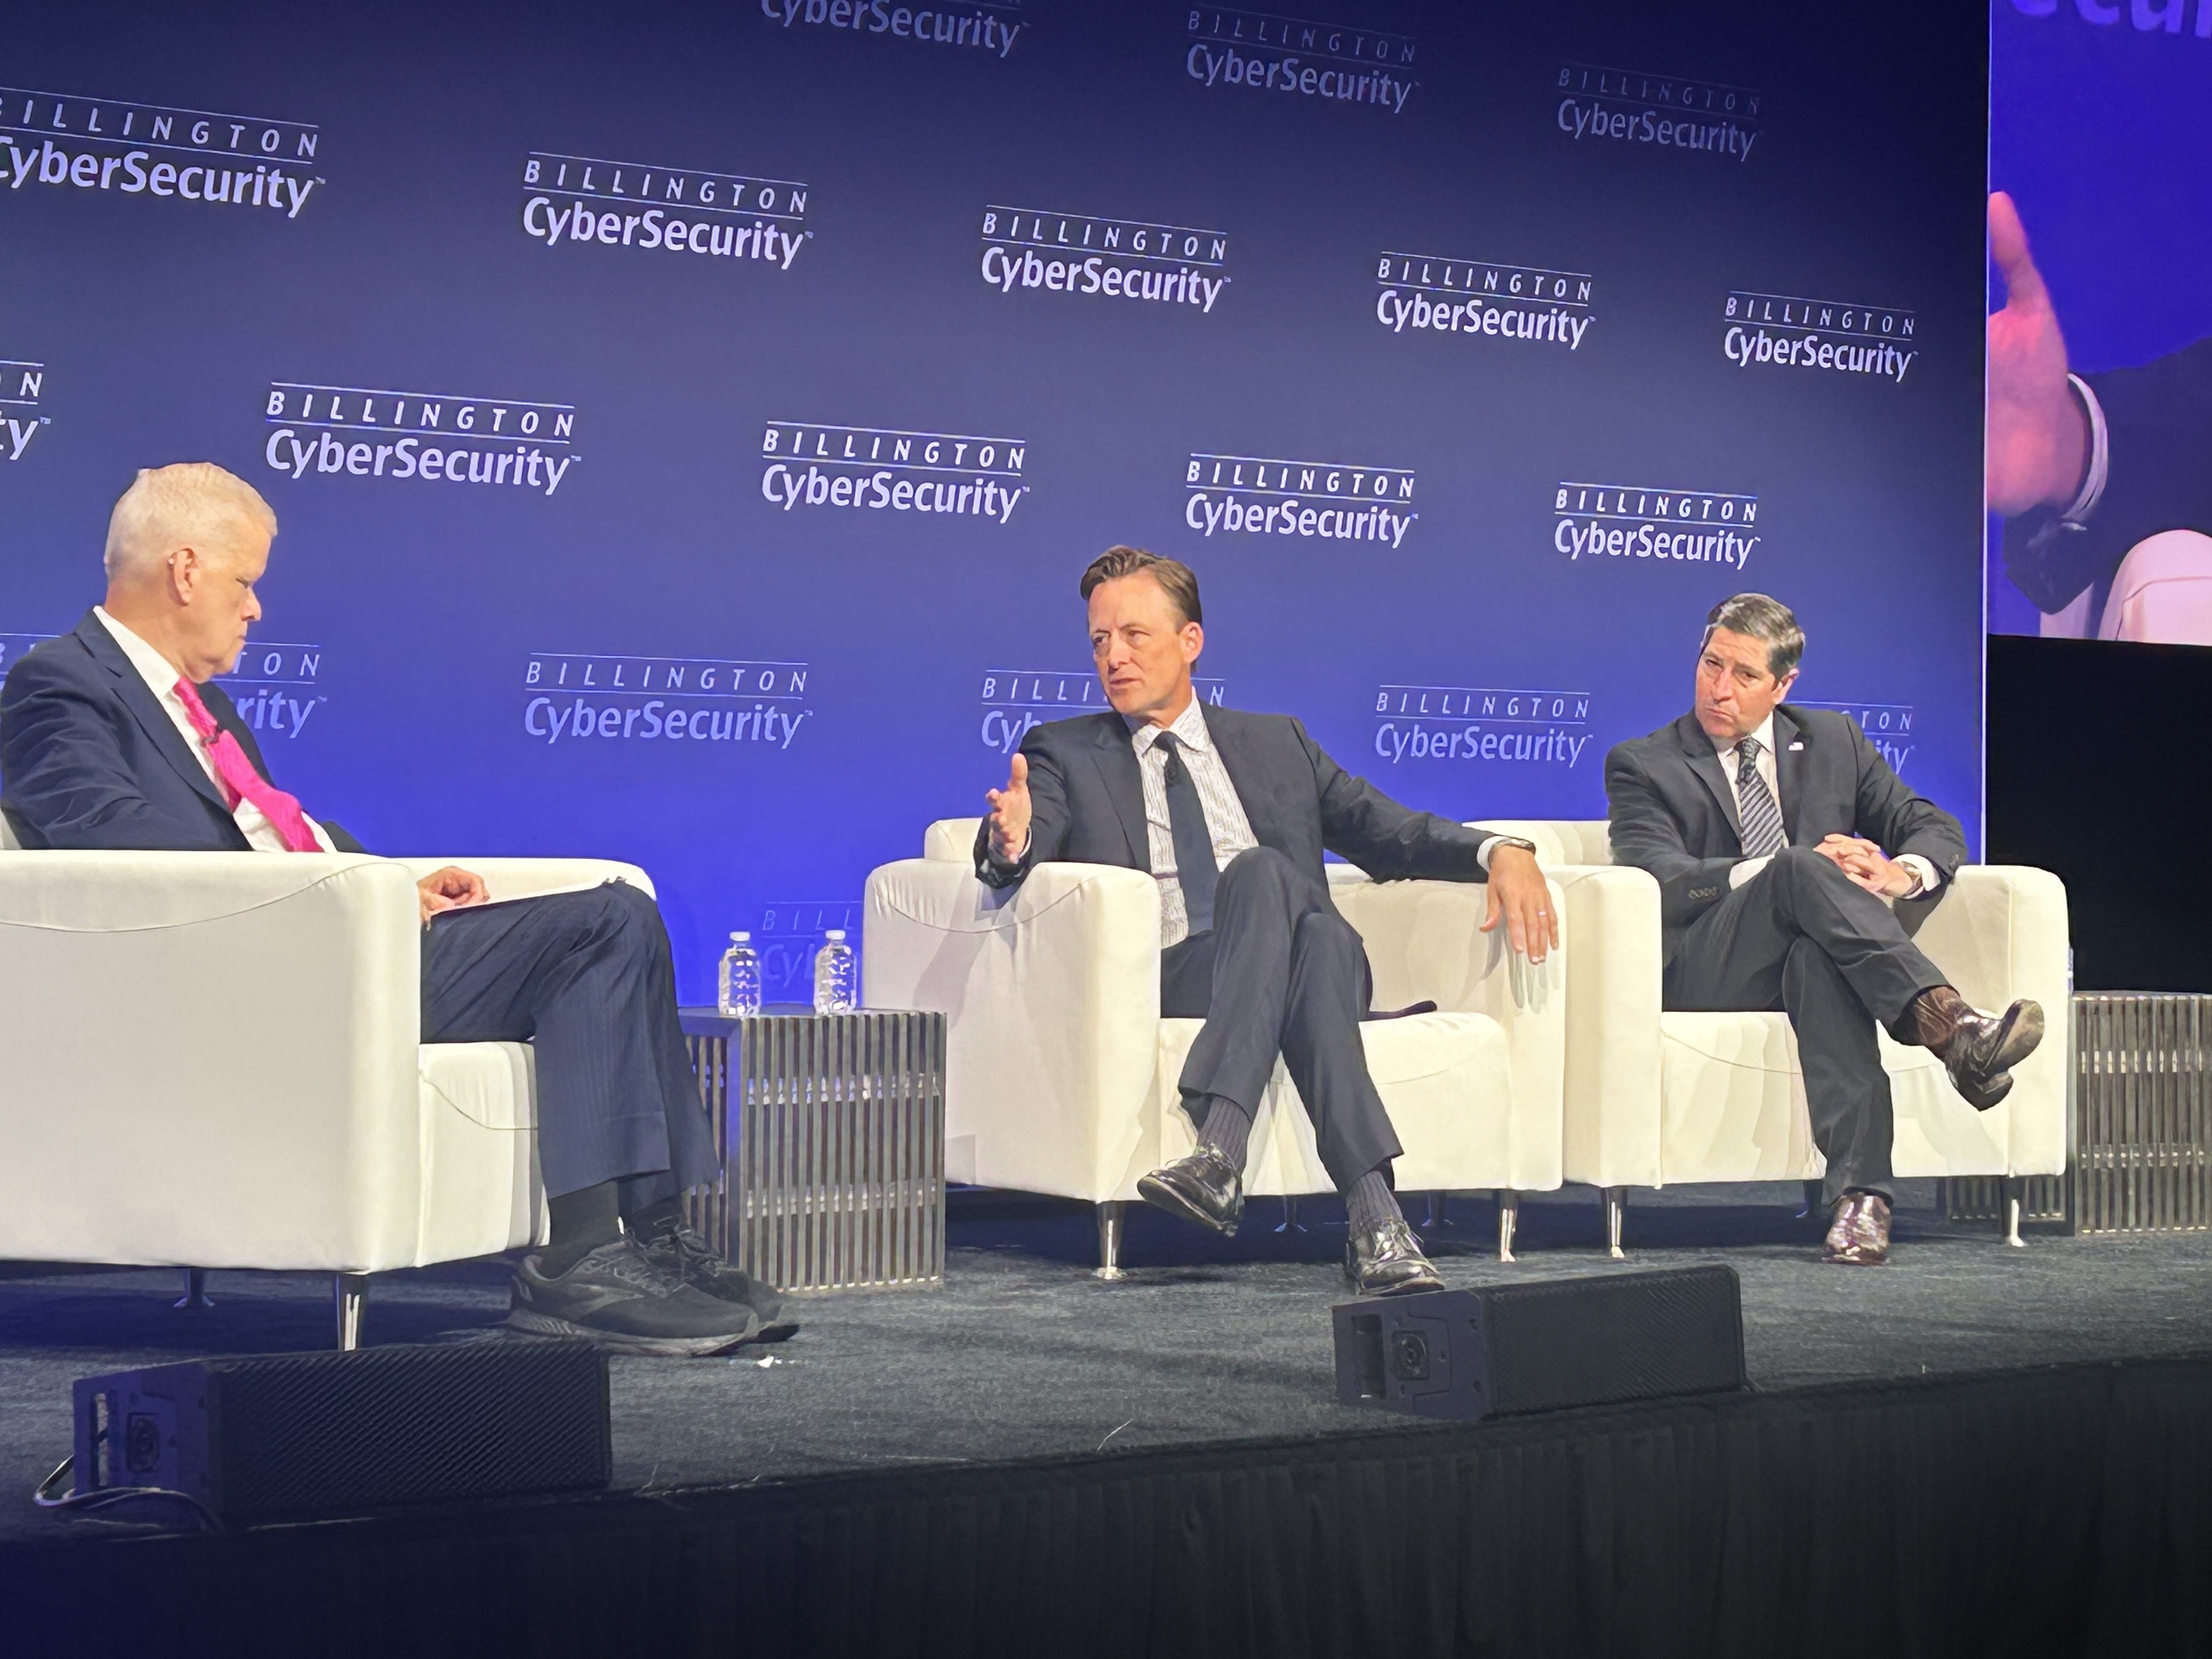
U.S. and allied governments are trying to stay ahead of AI-driven threats while securing their systems and preventing advanced technology from falling into hostile hands. Officials said AI is exposing long-ignored weaknesses in basic cyber hygiene, and recent incidents involving Chinese AI companies and Anthropic highlight the urgency of the issue. #Anthropic #China

HardenStance’s MWC 2025 review says telco cybersecurity is improving, but only incrementally, with regulators, vendors, and operators increasingly focused on scam protection, network hardening, and AI-driven security. The report highlights major gaps in telco preparedness alongside rising threats from AI fakes, China-nexus intrusion activity, and continued pressure to deploy practical protections such as DNS filtering, fraud registries, and Open Gateway APIs. #SaltTyphoon #LiminalPanda #LocksmithPanda #OperatorPanda #LightBasin #STC #Singtel #Telefonica #Whalebone #Aeris #Nokia #Ericsson #Allot #Bitdefender #Enea #F-Secure #GenDigital #Mobileum #Netnumber #PowerDNS #Ribbon