Oracle Health’s legacy Cerner systems were reportedly breached early last year, exposing personal and medical information tied to nearly 20 million people. The incident involved stolen customer credentials, extortion demands from an individual threat actor known as “Andrew,” and notifications that revealed sensitive data such as Social Security numbers and medical…
Zohar Pinhasi, the owner of MonsterCloud, was charged with wire fraud after allegedly deceiving ransomware victims by claiming his company could decrypt encrypted data without paying attackers. Prosecutors say he actually paid the ransomware groups, then billed clients for recovery services, including one case where an $8,200 ransom led to a…
Four US states have sued TP-Link Systems, alleging the router maker misled consumers about both the security of its products and its ties to China. The complaints also cite multiple router vulnerabilities, alleged exploitation by Volt Typhoon and Flax Typhoon, and concerns over TP-Link’s disclosure of Chinese legal obligations and supply…

On lockbit5 hit grunenwald.com (DE), deploying ransomware to encrypt files and disrupt operations. The incident impacted Germany #Germany
Storm targeted TheraCare, a US-based multi-service healthcare and educational organization founded in 1991 and headquartered in White Plains, New York, disrupting services across its clinical and educational programs. The incident impacted organizations in #UnitedStates.
Cooperative Des Techniciens Ambulanciers De La Monte (CETAM), based in Greenfield Park, Quebec, Canada, providing prehospital emergency care to nearly 20,000 calls annually with over 400 ambulance technicians and paramedics, was impacted by ransomware attributed to Storm. The threat actor’s activity affected CETAM’s operations in Canada #Canada
LockBit5 ransomware targeted capitalbankhaiti.biz, a Haiti-based organization providing traditional and online banking services. The incident likely disrupted financial operations and access to services in #Haiti
LockBit5 ransomware is alleged to have targeted consilio.com, a global legal software and services company based in the US. The impacted country is #UnitedStates
Scarlettgroup ransomware targeted yalebooks.yale.edu, the Yale Books website operated by Yale University Press, disrupting access to scholarly, academic, and general-interest book sales and content. The attack is attributed to Scarlettgroup and affected users in #UnitedStates

Arizona’s court system said hackers accessed and copied backup court files, exposing sensitive information tied to more than 1.3 million people. The breach also affected foster care reports and protective order records, and investigators believe it began when a court employee clicked a malicious phishing link. #FARE #FosterCareReviewBoard #FBI #AnnScottTimmer…
Lawmakers are urging Congress to provide $11 million in additional funding for mental health and resilience training for personnel at U.S. Cyber Command after several suicides this summer at the command and NSA. They say the investment is needed to reduce burnout, improve care access, and protect readiness for staff working…
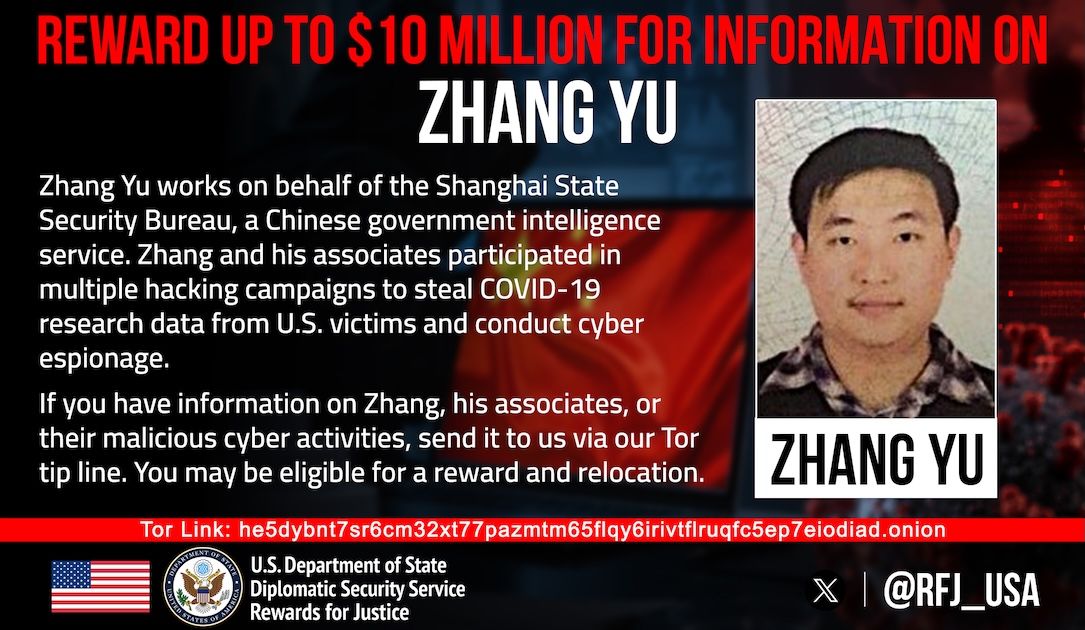
The U.S. State Department is offering $10 million for information on Zhang Yu, who is accused of helping carry out the Hafnium hacking campaign on behalf of the Chinese government. Prosecutors say Zhang and Xu Zewei stole data from U.S. universities and a law firm, including COVID-19 research, while acting under…
T-Mobile (US) is reportedly affected by ransomware activity attributed to the BYOD threat actor. The claim warns the organization that communication will be established before the attackers take further action and states the threat continues until that contact is made. #UnitedStates
In Brazil, ransomware claims targeting Petrosul Distribuidora, Transportadora e Comércio de Combustíveis Ltda. highlight disruption at the fuel storage terminal operator founded in 1994 and operating since 2015 with real-time control and modern infrastructure. Threat actor dragonforce is reported to be responsible for the attack impacting critical operations across Petrosul’s terminals in Sorocaba, Paulínia, and Senador Canedo. #Brazil
K… in an unspecified country was targeted by SilentRansomGroup ransomware, with the full company name redacted pending disclosure under the active FULL DATA TIMER. The incident impacted #countryname