Microsoft has released the Windows 10 KB5120249 ESU for versions 22H2 and 21H2 to address security vulnerabilities, fix bugs, and deliver the August 2026 Patch Tuesday updates. The update resolves a File History backup issue over SMB and expands the rollout of new Secure Boot certificates. #Microsoft #Windows10 #KB5120249 #SecureBoot
Category: Cyber Security News
DeadLock ransomware uses a decentralized setup with the Polygon blockchain, the Session network, and Wasabi cloud storage to hide its communication and data-leak operations. Microsoft says the group, active since mid-2025, has already listed 80 victims and relies on double extortion to pressure organizations into paying. #DeadLock #Polygon #Session #Wasabi
Hackers are targeting social media accounts to steal explicit content and sell it on criminal marketplaces, according to a new FBI alert. The FBI says attackers use social engineering, password guessing, fake support scams, and cloned login pages, then often extort and harass victims with the stolen material. #FBI #Snapchat #UniversityofMichigan…

A newly disclosed flaw in OpenAI, Anthropic, and Google reasoning APIs let researchers replay encrypted reasoning objects across sessions and recover hidden content from public logs, including API keys and passwords. The paper also showed how opaque reasoning blocks could be used to hide prompt injections and extract proprietary traces, with…

Lazarus Group is exploiting a recently patched Windows zero-day, CVE-2026-68820, to deliver a new backdoor called Troy against defense and aerospace targets in France, Germany, Brazil, and India through Operation Dream Job. The campaign uses fake recruiter lures, trojanized PDF software, and compromised legitimate sites and servers to spread MISTPEN, ForestTiger,…
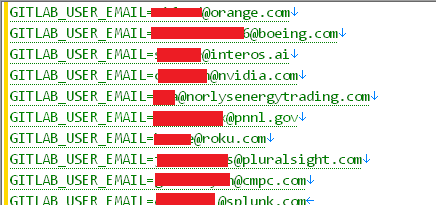
TeamPCP orchestrated a multi-ecosystem supply chain attack that began by compromising Trivy’s GitHub Actions pipeline and ended with malicious LiteLLM packages silently stealing secrets from CI/CD environments worldwide. The leak exposed 153GB of data from 118,829 pipeline runs tied to 2,488 domains, affecting organizations including AWS, Samsung, Cisco, Salesforce, ServiceNow, Siemens, and others. #TeamPCP #Trivy #LiteLLM #HudsonRock #Cavalier #Orange #Boeing #Roku #AdsWizz
Attempts to exploit CVE-2026-71362 in Adobe Commerce and Magento are being blocked by Sansec’s Shield WAF, even though Adobe says it is not aware of active exploitation in the wild. The flaw can let attackers hijack customer sessions and access private account data without authentication, while Adobe has also patched six additional vulnerabilities in the same update. #AdobeCommerce #Magento #CVE-2026-71362 #Sansec
WindRelay, an Android NFC relay malware, is being used with the SpyNote RAT to steal payment card data and enable real-time fraudulent transactions. Group-IB says attackers impersonated bank staff, tricked victims into sideloading a malicious app, and completed the fraud in a 13-minute call. #WindRelay #SpyNote #GroupIB
Researchers unveiled “Plug and Pwn” attacks that abuse Windows Plug and Play and RDP USB redirection to force automatic installation of vulnerable vendor packages, enabling attackers to gain SYSTEM privileges. The demonstrations used emulated USB devices and affected software from Sierra Wireless, Sony FeliCa, Intel RealSense, Wacom, and Atheros, showing that even fully updated Windows systems can be exposed. #PlugandPwn #SierraWireless #SonyFeliCa #IntelRealSense #Wacom #Atheros
More than 737 Chrome Web Store extensions impersonated major VPN and proxy brands while secretly routing user traffic through SOCKS5 proxies controlled by a single provider. The campaign, linked to 40 publisher accounts and nearly 75,000 downloads, used deceptive tactics to push users toward a likely subscription-based VPN service in Russia. #ProtonVPN #NordVPN #Surfshark #ExpressVPN #Cloudflare #ChromeWebStore

Suspected Chinese hackers used open-source AI frameworks Hermes and OpenClaw to launch a near-autonomous cyberattack against the Taiwanese government, marking the first publicly known AI-driven attack to hit a government target. The operation extracted more than 2,500 personnel records and expanded to vendors, a nuclear safety agency, a government email system, and energy companies while adapting through “Learning Cycles” without human intervention. #TaiwaneseGovernment #Hermes #OpenClaw #Dream

Daily Recap, CISA and allied agencies warned that Gunra is targeting government and critical infrastructure, while StormEncryptor has been linked to a former Medusa affiliate and likely ties to an N-central flaw; at the same time, Microsoft SharePoint and SonicWall SMA1000 vulnerabilities are being actively exploited by ransomware groups. The update also covered OpenAI’s ChatGPT 5.6 Cyber and Daybreak expansion, the BdThemes supply-chain compromise creating rogue WordPress admin accounts, plus new patching and vulnerability-tracking efforts alongside rising DDoS activity.
#Gunra #StormEncryptor #Medusa #N-central #CISA #Microsoft #SharePoint #SonicWall #SMA1000 #OpenAI #ChatGPT5.6Cyber #Daybreak #BdThemes #WordPress #SAP #Mozilla #GPG #Firefox #Thunderbird #Corma #FTC #CVE #NATO #Metabase #MCP #TheCom #DDoS

A large campaign involving 737 free VPN and proxy extensions targeted Russian-speaking users by impersonating trusted brands and silently routing browser traffic through attacker-controlled SOCKS5 infrastructure. Separately, the Chrome extension “AI Sidebar with Deepseek, ChatGPT, Claude, and more” resurfaced with a new monetization payload after a prior removal, showing how malicious…
Mindgard has raised $30 million in a Series A round led by Album VC, bringing its total funding to nearly $42 million. The London and Boston-based startup will use the investment to expand its AI red-teaming platform, which has already found over 150 vulnerabilities in products including Cursor IDE, Google Antigravity,…
A SharePoint vulnerability, CVE-2026-55040, is now being actively exploited in the wild shortly after Rapid7 published technical details and a proof-of-concept script. Microsoft has also patched CVE-2026-63520, which could be chained with CVE-2026-55040 to enable unauthenticated remote code execution on SharePoint servers. #CVE-2026-55040 #Rapid7 #CVE-2026-63520 #Microsoft #SharePoint…