Evooo1Bot is a new Mirai-based modular Linux botnet that targets internet-facing gateway devices to turn them into SOCKS5 relay nodes while also enabling credential theft, SSH brute-forcing, and DDoS attacks. It has been observed exploiting multiple known vulnerabilities across devices from Alcatel, NETGEAR, Tenda, Mitsubishi Electric, Telesquare, D-Link, and other platforms, with newer builds targeting Hikvision, Confluence, Zyxel, TP-Link, WSO2, Kubernetes ingress-nginx, and PHP-CGI systems. #Evooo1Bot #Mirai #Alcatel #NETGEAR #Tenda #MitsubishiElectric #Telesquare #DLink #Hikvision #AtlassianConfluence #Zyxel #TPLink #WSO2 #Kubernetes #ingress-nginx #PHP-CGI
Category: Cyber Security News
German and Brazilian authorities arrested multiple suspects linked to a late-2023 scheme that stole about €30 million from German bank accounts by exploiting a payment provider vulnerability and using cloned payment cards. The investigation spanned Europe and Brazil, led to major asset seizures, and also uncovered that one suspect allegedly used…
Four cybercriminals were arrested in Brazil and three others were charged in Europe after exploiting a vulnerability at a service provider to withdraw money from Commerzbank customer accounts. The operation, linked to losses of about €30 million and dubbed Operation Klonen, involved laundering the funds through a network spanning Brazil and several European countries. #Commerzbank #OperationKlonen #BKA

Daily Recap, Microsoft, Fortinet, and Adobe Commerce rushed critical patches as attackers weaponized newly disclosed flaws, while SharePoint authentication bypass issues were exploited shortly after proof-of-concept release. Lazarus also leveraged a Windows zero-day to obtain SYSTEM access and deploy a backdoor, and multiple AI security concerns surfaced alongside fraud, mobile threats, and ongoing data-breach reporting from Trezor.
#Microsoft #Fortinet #AdobeCommerce #SharePoint #Lazarus #Windows #Trezor

France’s tax authority, DGFiP, confirmed that hackers accessed its systems in late June and extracted data on individuals and businesses. The attack was later claimed by ZeroBytes, though the extent of the stolen information and the number of affected victims are still being investigated. #DGFiP #ZeroBytes #FrenchBreaches…
SOCRadar says most of the 2,500 organizations initially linked to the LiteLLM incident were actually exposed earlier through the TeamPCP-led Trivy compromise, which spread downstream across packages and CI/CD systems. The attack used a worm-like payload to steal credentials and secrets, and the collected data is now being brokered on Telegram….

SecurityWeek’s weekly roundup covers major cybersecurity developments, including a controversial Defense Department AI contract, a North Korean IT worker investigation, and new findings on Boeing 737 and commercial refrigeration system vulnerabilities. It also reports on LexisNexis probing a possible breach, Uber Freight investigating unauthorized access, CISA warning about Gunra ransomware, and…
Shell has confirmed it is investigating a potential security incident after the Clop gang claimed it stole 89GB of data, including engineering drawings, facility testing reports, photos, and project plans. The alleged theft is linked to attacks against Internet-exposed PTC Windchill and FlexPLM instances exploiting CVE-2026-12569, with Shell, General Electric, and Philips among the claimed victims. #Shell #Clop #PTC #Windchill #FlexPLM #CVE-2026-12569 #GeneralElectric #Philips
Defused says attackers are already targeting CVE-2026-58231, a critical unauthenticated RCE flaw in SAP Commerce Cloud that was patched just three days earlier. The issue affects a widely used e-commerce platform for major global brands, and Shadowserver has identified over 4,200 exposed SAP Commerce Cloud IPs worldwide. #CVE-2026-58231 #SAPCommerceCloud #Defused #Shadowserver
The Vercel and Composio breaches show a repeated attack pattern where stolen OAuth grants, not email, become the entry point into Google Workspace, enabling access to Gmail, Drive, and downstream systems. The same workspace chain can also be followed by AI agents operating with legitimate permissions, making full-chain defenses essential. #Vercel #Composio #GoogleWorkspace #OAuth
The Netherlands’ National Cyber Security Centre says CVE-2026-65400 in macOS Screen Sharing is being actively exploited after public exploit code appeared. Attackers are using exposed port 5900 to gain root access and install a Monero miner on affected systems. #CVE-2026-65400 #macOS #NCSC #Monero
ShinyHunters claimed responsibility for a breach at RingCentral that exposed personal information from 1.6 million accounts, according to Have I Been Pwned. RingCentral said its core platform was not affected and that the incident stemmed from a sophisticated social engineering campaign, while the group allegedly leaked stolen data after the company refused to pay ransom. #ShinyHunters #RingCentral

Beacon said its recent breach likely began with a compromised AWS access key, allowing an attacker to export customer database backups from its CRM platform for charities and nonprofits. The incident may affect more than 1,000 customers, with some UK charities warning that supporter contact details were exposed, while no financial…
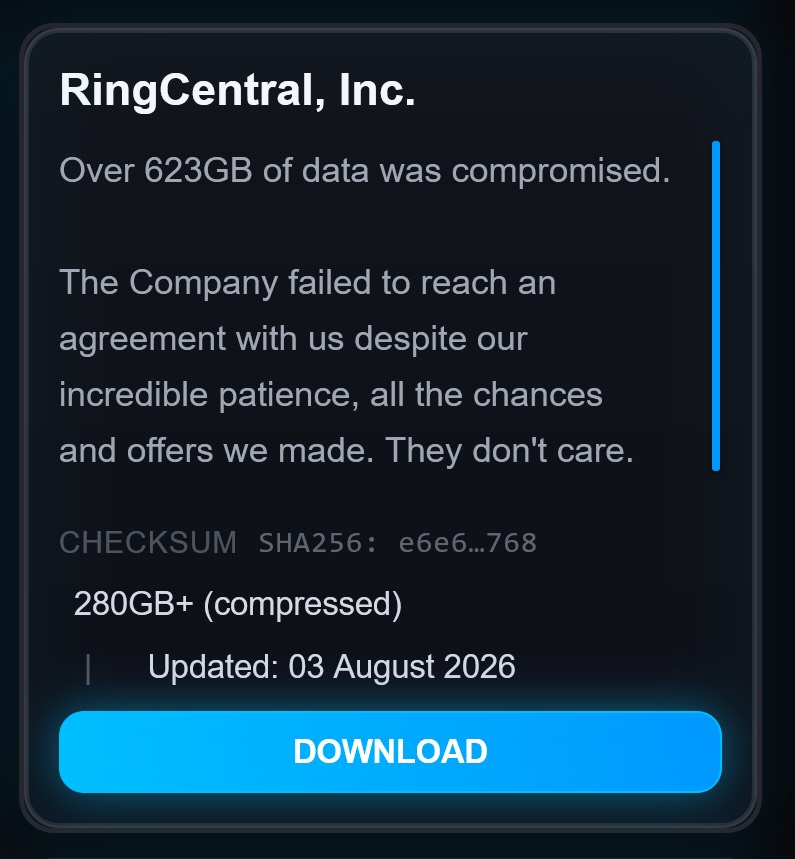
A data breach tied to RingCentral appears to have exposed personal information belonging to about 1.6 million individuals after a sophisticated social engineering campaign in July. The ShinyHunters extortion group later leaked stolen data that reportedly included email addresses, names, addresses, and phone numbers. #RingCentral #ShinyHunters #HaveIBeenPwned…
Google Cloud has updated its post-quantum cryptography roadmap, aiming for full readiness by 2029 while continuing some work into the 2030s. The plan focuses on reducing Store Now Decrypt Later risk, strengthening signatures and identity protections, and expanding quantum-safe infrastructure across services like Google Cloud KMS, Cloud VPN, and BigQuery. #GoogleCloud…