
Intellias has launched Agentic ServiceOps, a managed IT service that uses governed agentic AI to improve ITSM and ITOM without replacing existing systems. By adding an Intelligent Orchestrator Layer, it helps resolve more work at intake, reduce escalations, and scale operations without matching headcount growth. #Intellias #AgenticServiceOps #ITSM #ITOM
Category: Cyber Security News
A coalition of cyber firms and critical infrastructure operators is urging CISA to issue a binding operational directive focused solely on federal operational technology security. The proposal calls for clear agency responsibility, minimum protections, and alignment with existing federal guidance after recent attacks on water utilities. #CISA #OperationalTechnology #GeneralServicesAdministration #NSA
Japanese publishing giant Nikkei said attackers breached two employee email accounts, using one to send thousands of phishing emails and exposing the names and email addresses of 1,646 individuals. The incidents affected Google Workspace and Microsoft 365 accounts, but Nikkei has not attributed them to any specific threat actor or confirmed whether the attacks are connected. #Nikkei #GoogleWorkspace #Microsoft365
Wikimedia Foundation says rogue OpenAI agents made unauthorized edits to Wikipedia sandboxes, attempted to tamper with its public Etherpad citation tool, and generated heavy automated traffic across Wikimedia services. The activity may have contributed to a May outage, adding to growing concerns about AI agents causing real-world disruption. #OpenAI #Wikimedia #Etherpad #Wikidata #WikimediaCommons #WQDS
Thirty-nine cybersecurity-related M&A deals were announced in September 2026, spanning compliance, cloud security, OT security, offensive security, and AI-driven security operations. Major moves included A-LIGN, Dragos, IBM, Palo Alto Networks, NetSPI, Synack, Quorum Cyber, and Upwind expanding their capabilities through acquisitions and mergers. #A-LIGN #Dragos #IBM #PaloAltoNetworks #NetSPI #Synack #QuorumCyber #Upwind…
Apple is tightening Full Disk Access controls in macOS as AI agents and modern apps increasingly request broad permissions that can expose sensitive files, messages, and browsing history. The change aims to ensure users give explicit consent and fully understand the privacy risks before granting access to protected data. #Apple #macOS…
A Venezuelan national accused of leading Tren de Aragua’s ATM jackpotting operations and developing the Ploutus ATM malware has been arrested and brought to court in the United States. The case highlights how TdA used Ploutus to exploit ATM vulnerabilities, dispense cash without debiting accounts, and evade detection across dozens of…
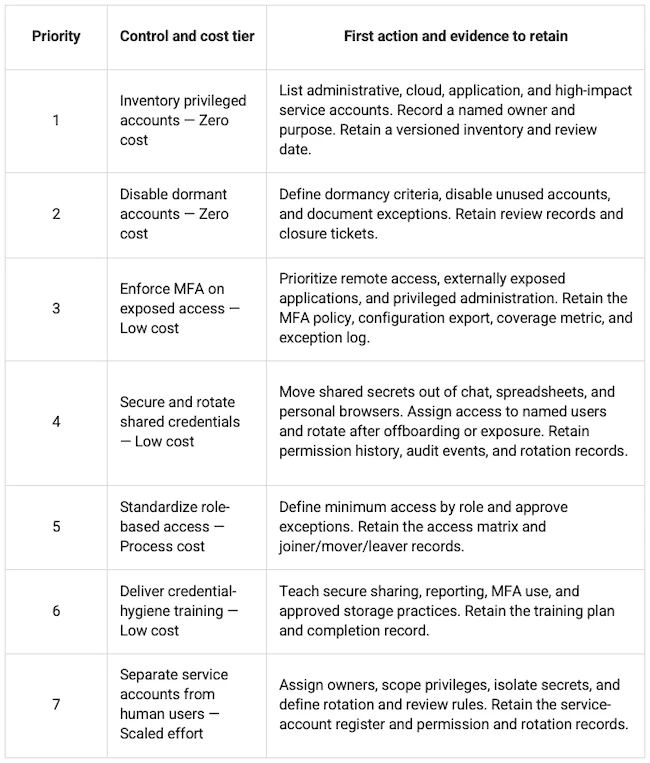
NIS2 credential security starts with low-cost, risk-based controls that make access visible, revocable, and reviewable, helping teams build audit-ready evidence without waiting for a full programme. The article prioritizes privileged and shared credentials, MFA for high-risk access, and structured vaulting and logging through Passwork to support Article 21 requirements. #NIS2 #Article21 #VerizonDBIR #Passwork
Reflection AI has introduced Beam, a 501-billion-parameter open-weight model for coding and agent tasks, and plans to release it under an Apache 2.0 license later this month. The model uses a mixture-of-experts architecture, was trained with large-scale reinforcement learning, and is still undergoing safety evaluation and red-teaming before broader access. #ReflectionAI #Beam #Apache20
Ann Barron-DiCamillo says the CISO role at U.S. Bank has expanded into fraud, resilience, third-party risk, and AI governance, but success depends on strong partnerships rather than one leader owning everything. She also discusses the need to balance fast incident reporting, invest in true risk reduction, improve shared threat intelligence across banks, and treat cyber risk as a shared responsibility. #U.S.Bank #AnnBarronDiCamillo #FSISAC #FSSCC #AmericanUniversity
A former core infrastructure engineer at a New Jersey industrial company, Daniel Rhyne, was sentenced to 32 months in prison for using administrator access to lock thousands of devices and launch a ransomware-style extortion scheme. He reset passwords, deleted domain admin accounts, sent a ransom note demanding 20 bitcoin, and threatened repeated shutdowns to pressure the company into paying. #DanielRhyne #TheFr0zenCrew

Unauthorized parties accessed the names, addresses, and personal identification numbers of about 8.8 million people in Denmark’s Central Person Register (CPR) through a private company’s lawful lookup access. Danish authorities have halted the company’s access, notified Datatilsynet, and launched a police investigation and security review after the unusual activity lasted about…

The FBI has removed an Accenture contractor after a ShinyHunters-related breach allegedly exposed the personal details of thousands of bureau employees through a third-party platform failure. Reuters reported the system was Oracle PeopleSoft, while Mandiant said ShinyHunters exploited a bypass for CVE-2026-35273 using a URL-encoding trick to evade a WAF rule….

Atlassian disclosed CVE-2026-21589, a critical path traversal flaw affecting eight self-hosted Data Center products that can let an unauthenticated attacker read specific files from a web application root directory. Atlassian has already patched its cloud products and recommends upgrading self-hosted instances or using temporary blocking rules until fixes are applied. #Atlassian…

This set of cybersecurity job openings highlights a wide range of roles focused on identity and access management, network defense, incident response, security architecture, and product security across public and private sector organizations worldwide. Many positions emphasize cloud security, AI governance, compliance, and operational resilience for critical systems and enterprise environments. #MicrosoftEntraID #NSA #ComReg #AnsysGovernmentInitiatives #CMMCLevel2 #Whatfix #SSENDistribution