Former U.S. Army General Paul M. Nakasone has launched the Nakasone Group, a boutique advisory firm focused on national security, cybersecurity, geopolitical, and personal protection services for governments, corporations, and private clients. The firm offers private cyber defense, fraud and impersonation protection, travel security, and threat intelligence, drawing on a team…
Category: Cyber Security News

Daily Recap, critical flaws in Elementor Pro, Cisco Crosswork/Secure Workload, and MLflow are being actively abused or patched, enabling RCE and potential compromise of WordPress and enterprise environments, while additional issues allow unauthenticated PHP uploads through another Elementor Pro weakness. Clop’s PTC zero-day campaign continues with further impact on PTC products, and separate reports highlight AI security policy momentum, OpenAI model safeguards, major breaches at Sakura Internet and CareCloud, and threat activity including SilkParasite RATs and Spectre data leakage from Cloudflare Workers.
#ElementorPro #CiscoCrosswork #SecureWorkload #MLflow #RCE #WordPress #Clop #PTC #Windchill #FlexPLM #OpenAI #Sandboxing #SakuraInternet #CareCloud #SilkParasite #Dahua #CloudflareWorkers #Spectre #JWT #MSPs #TinaPeters
Apollo Global Management confirmed that attackers used social engineering to gain unauthorized access to some of its cloud platforms between July 6 and July 10, exposing personal data including names, dates of birth, contact information, home addresses, and Social Security numbers. Google has attributed the broader campaign to BlackFile, a threat group linked to The Com and its extortion brands Redact, Pink, Helix, and Falcon. #ApolloGlobalManagement #BlackFile #TheCom #Redact #Pink #Helix #Falcon
SynkLoader is a newly identified malware family spread through Microsoft Teams phishing campaigns that impersonate a company’s IT help desk and trick victims into installing a fake “PowerShell Cleaner” MSI from Microsoft Azure. It uses a fake Windows lock screen to steal credentials and can deploy modules for persistence, traffic redirection, remote shell access, and desktop control, with activity suggesting possible ransomware preparation. #SynkLoader #MicrosoftTeams #PhishLocker #PowerShellCleaner #Expel #MarcusHutchins
Sen. Ron Wyden and Rep. Greg Casar are urging the Government Accountability Office to investigate how U.S. federal agencies use hacking tools and spyware against Americans, and to publish the findings. Their request focuses on the scope of government hacking, safeguards against abuse, and cases involving firms like Paragon and tools tied to Rule 41 requests. #RonWyden #GregCasar #GAO #Paragon #Rule41
Microsoft says the August 2026 Windows updates may be causing games to crash, freeze, or fail to launch on Windows 11 24H2 and 25H2 systems. The issue appears linked to RGB-lit peripherals or internal components that install drivers such as inpoutx64, affecting titles like ARC Raiders, MARVEL Tōkon: Fighting Souls, and The Finals. #Microsoft #ARCRaiders #MARVELTokonFightingSouls #TheFinals #inpoutx64
North Korean hackers conducted a supply chain attack against the Rust ecosystem by poisoning the popular arrayref crate and related packages on crates.io. Wiz linked the operation to Sapphire Sleet, noting infrastructure overlaps with earlier Axios and Mastra NPM campaigns and a malicious dependency impersonating proc-macro2. #SapphireSleet #arrayref #proc-macro2 #crates.io…
A critical type confusion flaw in the isolated-vm Node.js library could let attackers achieve remote code execution on the host by abusing the ExternalCopy transfer process across V8 isolates. The issue affects embedders running untrusted JavaScript with shared References and was fixed in isolated-vm versions 6.2.0 and 7.0.1. #isolated-vm #ExternalCopy #V8…
iAuthFlow V2 is a high-end phishing toolkit sold on a Russian-language cybercrime forum that can maintain access to a victim’s account even after a password reset. Abnormal’s analysis suggests the toolkit silently registers an attacker-controlled passkey during a phishing flow, making traditional recovery steps insufficient. #iAuthFlowV2 #Abnormal #Google #Gmail #passkeys…
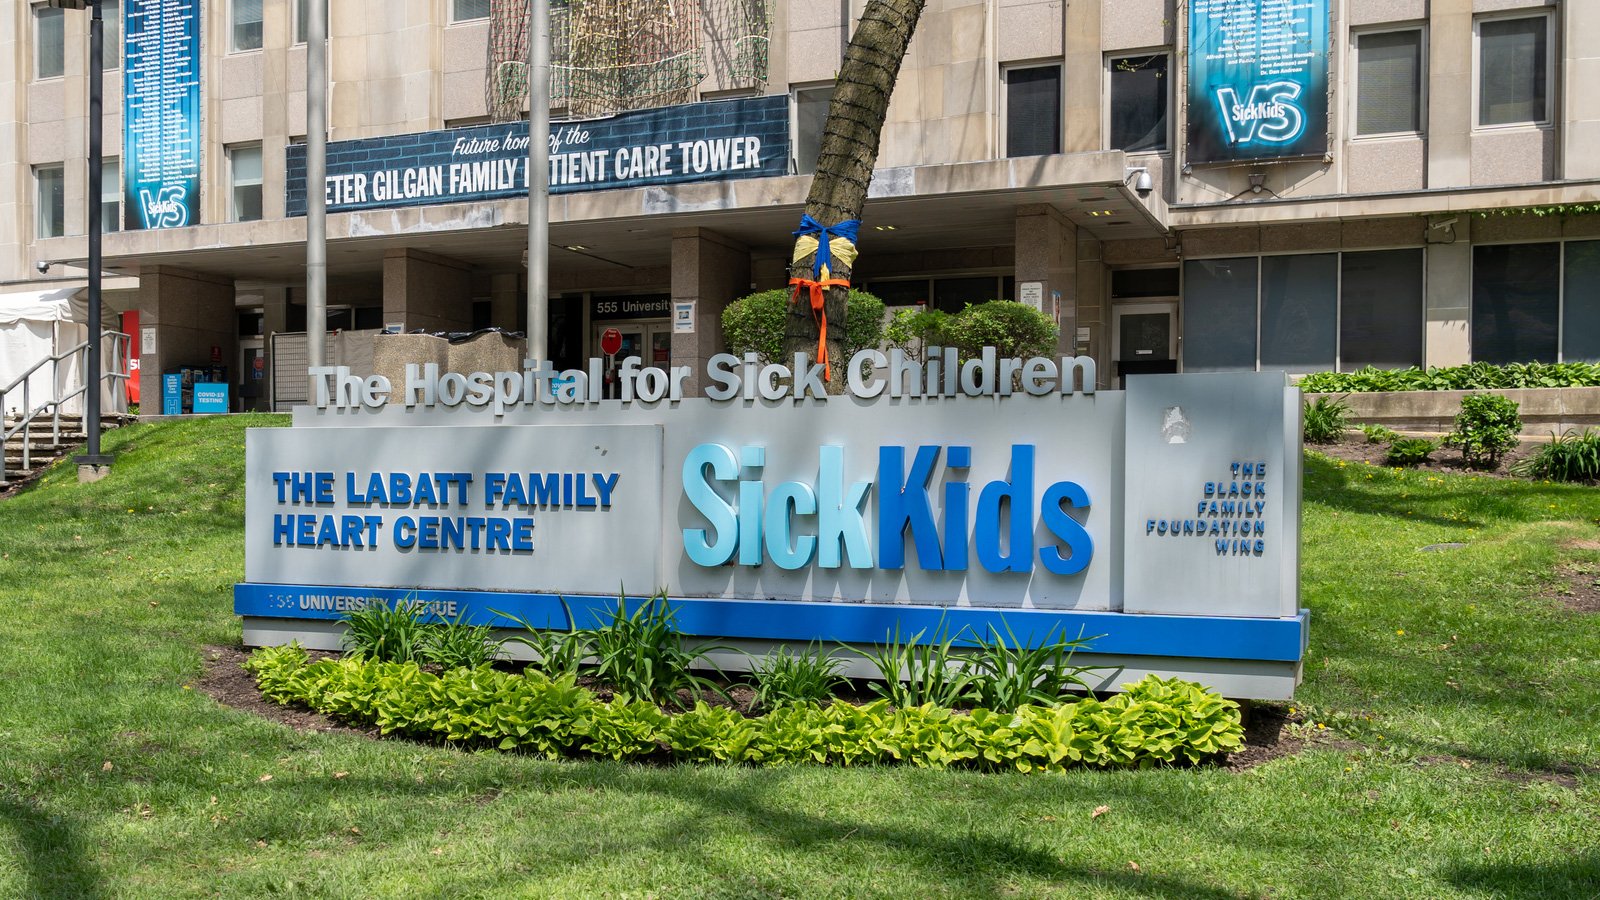
SickKids said a cybersecurity incident exposed personal information belonging to some current and former employees, as well as job applicants, due to a flaw in third-party software. The hospital says clinical systems and patient records were not affected, and it has restored the Careers website while continuing its investigation with outside experts. #SickKids #Boomerang #SickKidsFoundation #MOVEitTransfer #LockBit

Threat actors are abusing FTP server banners as dead-drop resolvers to deliver commands that install two previously undocumented remote access trojans, E4del and PINHOLE. The campaign likely begins with phishing-delivered ZIP and LNK files, while PINHOLE and E4del use unusual C2 and execution techniques to maintain access and evade detection. #E4del #PINHOLE #SOCRadar #MalwareHunterTeam
Microsoft has patched CVE-2026-69836, a maximum-severity flaw in Entra ID that allowed unauthenticated attackers to execute code over the network in low-complexity attacks. Microsoft says the issue has been fully mitigated and no user action is required, while also addressing several other critical flaws across Azure Arc, Exchange Online, and Azure Managed Instance for Apache Cassandra. #EntraID #CVE-2026-69836 #AzureArc #ExchangeOnline #AzureManagedInstanceforApacheCassandra
CareCloud reported that a March data breach affected 3,756,469 people after a hacker accessed one of its AWS electronic health record environments for eight hours and exfiltrated sensitive data. The exposed information included Social Security numbers, ID numbers, payment card details, medical records, and insurance data, prompting notifications to regulators and…

Two U.S. senators are pressing TikTok for answers after reports alleged the company disabled safety features for some users to study the impact on engagement, including minors. The controversy centers on internal testing tied to harmful content exposure and has renewed scrutiny of TikTok’s practices amid broader concerns over child safety…

Bitdefender uncovered SilkParasite, a China-linked espionage campaign targeting government bodies across Central Asia with seven malware families, including the newly observed DriveSilkRAT. The operation used spearphishing documents, Google Drive-based command traffic, and signs of AI-assisted malware development to hide its activity across the region. #SilkParasite #DriveSilkRAT #Bitdefender #Uzbekistan #Turkmenistan #Kyrgyzstan #Tajikistan…