Boston Scientific disclosed a cyberattack that disrupted parts of its IT environment, affecting access to business applications and the ability to process and ship customer orders worldwide. The company is still investigating the incident with external cybersecurity experts and has not yet determined when full restoration will be completed. #BostonScientific
Category: Cyber Security News
Shasta County registrar Clint Curtis said he offered former Mesa County clerk Tina Peters a consulting role to help prepare for the 2026 elections, but she has not yet accepted because she is consulting her legal team. The proposal has raised concerns because Peters was convicted in a Mesa County election-related case, while California election officials say any hire must comply with state law and preserve election integrity. #TinaPeters #ClintCurtis #MesaCounty #ShastaCounty #ShirleyWeber
Attackers are actively exploiting CVE-2026-60004, a critical code injection flaw in Gitea that can let authenticated users run arbitrary shell commands on vulnerable servers. Because default Gitea installations allow open registration, unauthenticated attackers can create accounts and repositories to abuse the flaw, prompting CISA to order urgent patching and Gitea to release version 1.27.1. #Gitea #CVE-2026-60004 #CISA
Microsoft is testing new Windows 11 privacy controls that let users manage camera, microphone, and precise location access for individual desktop apps. The company is also preparing smartphone-style permission prompts to improve transparency, consent, and user control over sensitive resources. #Windows11 #Microsoft
Google released Chrome 152 with fixes for 327 vulnerabilities, including 10 critical flaws and 61 high-severity issues, most of which were found internally using AI. External researchers also uncovered important bugs, including a critical vulnerability tracked as CVE-2026-79282, but Google did not report any in-the-wild exploitation. #Chrome152 #CVE-2026-79282 #Goodluck #Google…
MFA is essential, but it only proves control of authenticators at a point in time, not that the person is truly the legitimate identity. Attackers can exploit enrollment, recovery, help desks, session theft, and authenticator replacement to pass MFA while remaining impostors. #NISTDigitalIdentityGuidelines #IdentityThreatDetection #SessionHijacking…
CISA says more than 100 internet-exposed water and wastewater systems were targeted in July, with the attacks linked to Iranian threat actors and aimed at disrupting OT environments. The agency is urging critical infrastructure operators to reduce exposure of PLCs and other ICS devices, especially those reachable through cellular modems or…
Nutex Health Inc. disclosed that unauthorized attackers accessed its network, exfiltrated files from some servers, and may have taken confidential information tied to patients, employees, providers, business operations, finances, and intellectual property. The company said it does not currently believe the incident will materially affect its business, while warning that the…
AnonyMousKIT is a phishing-as-a-service platform that automates stealing Apple device unlock codes, bypassing Activation Lock, and harvesting Apple IDs, iCloud backups, and Keychain credentials. SOCRadar linked the operation to 506 domains and 168 reseller storefronts, with campaigns focused heavily on Brazil and reaching victims in multiple countries. #AnonyMousKIT #SOCRadar #Apple #ActivationLock
Threat actors are abusing npm packages and mirrors like UNPKG and npmmirror to host malicious HTML pages that impersonate Cloudflare CAPTCHAs and redirect users to attacker-controlled destinations. The campaign uses legitimate infrastructure as free hosting for phishing pages, with some redirects pointing to Microsoft login themes, ChatGPT, or dynamically controlled URLs. #Cloudflare #npm #UNPKG #npmmirror #Turnstile
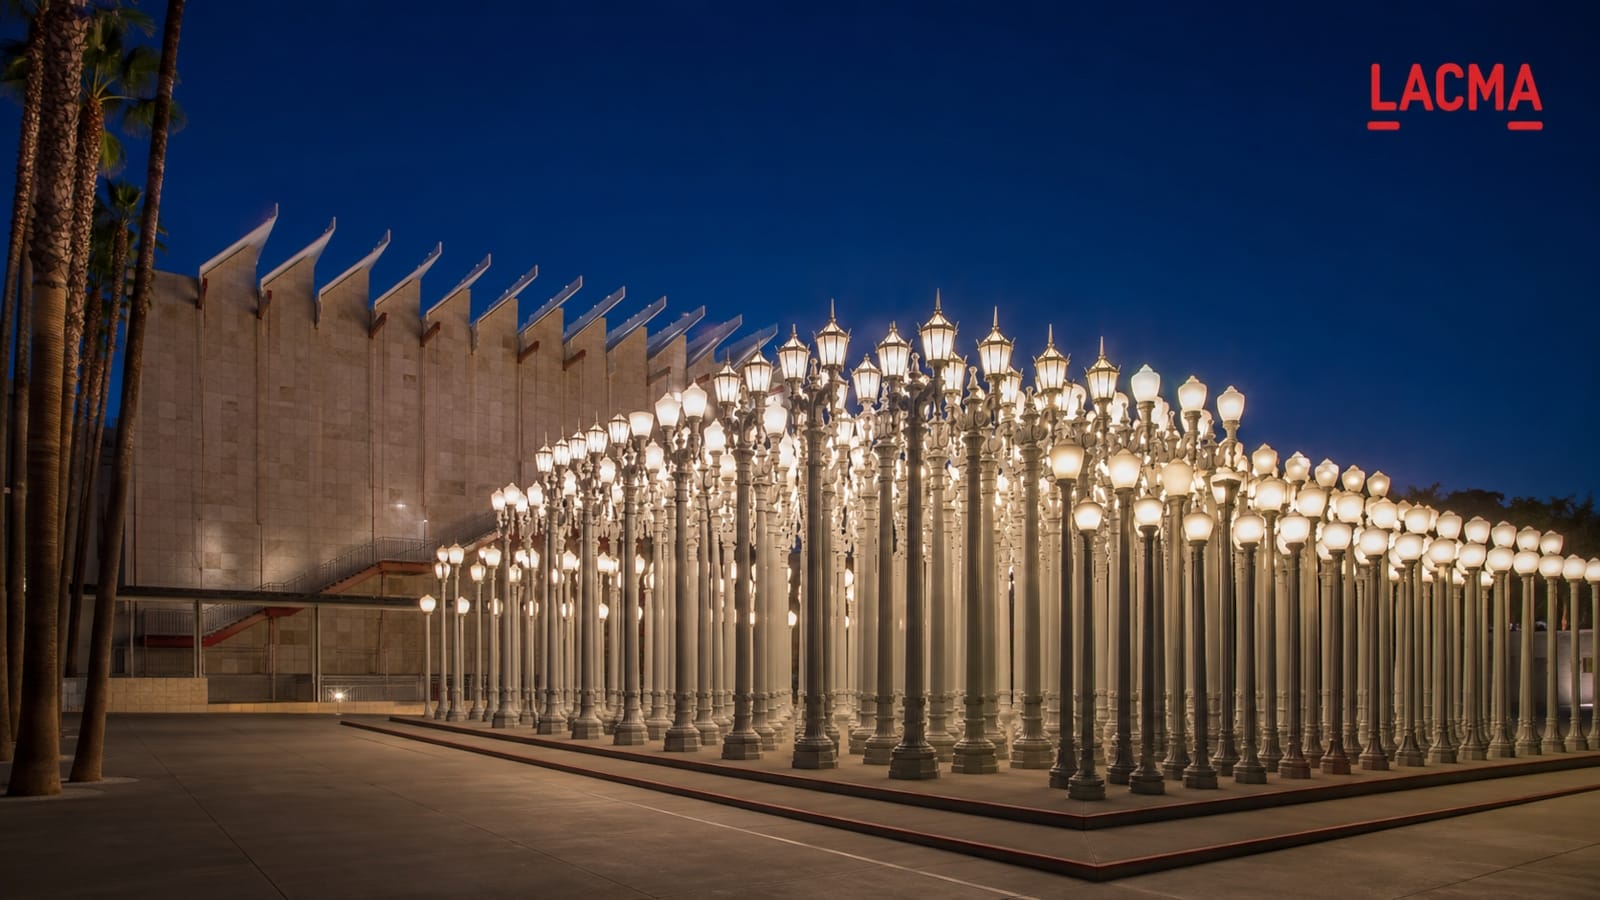
LACMA disclosed a breach that exposed customer and employee information after suspicious activity was detected on its systems in July 2025. The museum later determined that attackers may have accessed highly sensitive data, including Social Security numbers, government IDs, financial details, and health information. #LACMA

Colorado police arrested Joshua Culver, also known as “Maverick Young,” for allegedly impersonating Supreme Court Chief Justice John Roberts and an NSA TAO leader. The indictment says he used forged court documents and false federal authority to try to influence cases in Indiana, including demands to dismiss charges and quash warrants. #JohnRoberts #NSA #TailoredAccessOperations #JoshuaCulver
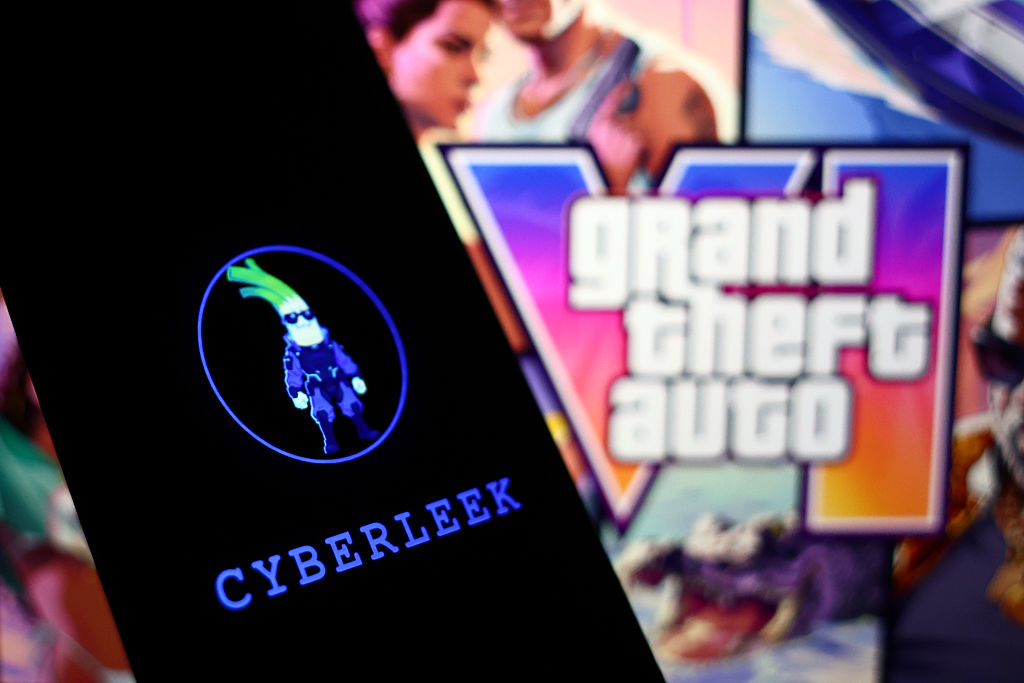
Grand Theft Auto VI faced a major leak after the persona CyberLeek released gameplay footage early, triggering a high-profile investigation that may involve insider access or stolen proprietary data. Take-Two Interactive and Rockstar Games responded with DMCA subpoenas and copyright notices while the leaks continued to spread, turning the incident into both a legal fight and an unwanted marketing campaign. #GrandTheftAutoVI #CyberLeek #RockstarGames #TakeTwoInteractive #Discord #Google #Microsoft #X

Daily Recap, South Korean startup platform breach coverage highlighted major key management and secret-handling failures, while Uber was fined nearly $1 billion by Dutch regulators over automated driver-account suspensions and related privacy concerns. On the patching and vulnerability front, Spring received fixes for 91 vulnerabilities and Microsoft warned about August update compatibility issues affecting WPF printing/PDF export and shared a temporary workaround for Windows 11 gaming problems, plus a Venezuelan defendant received a record federal prison term for ATM jackpotting. #SouthKorea #KeyBreach #Uber #DutchRegulators #SpringApplicationFramework #WPF #Windows11 #ATMJackpotting
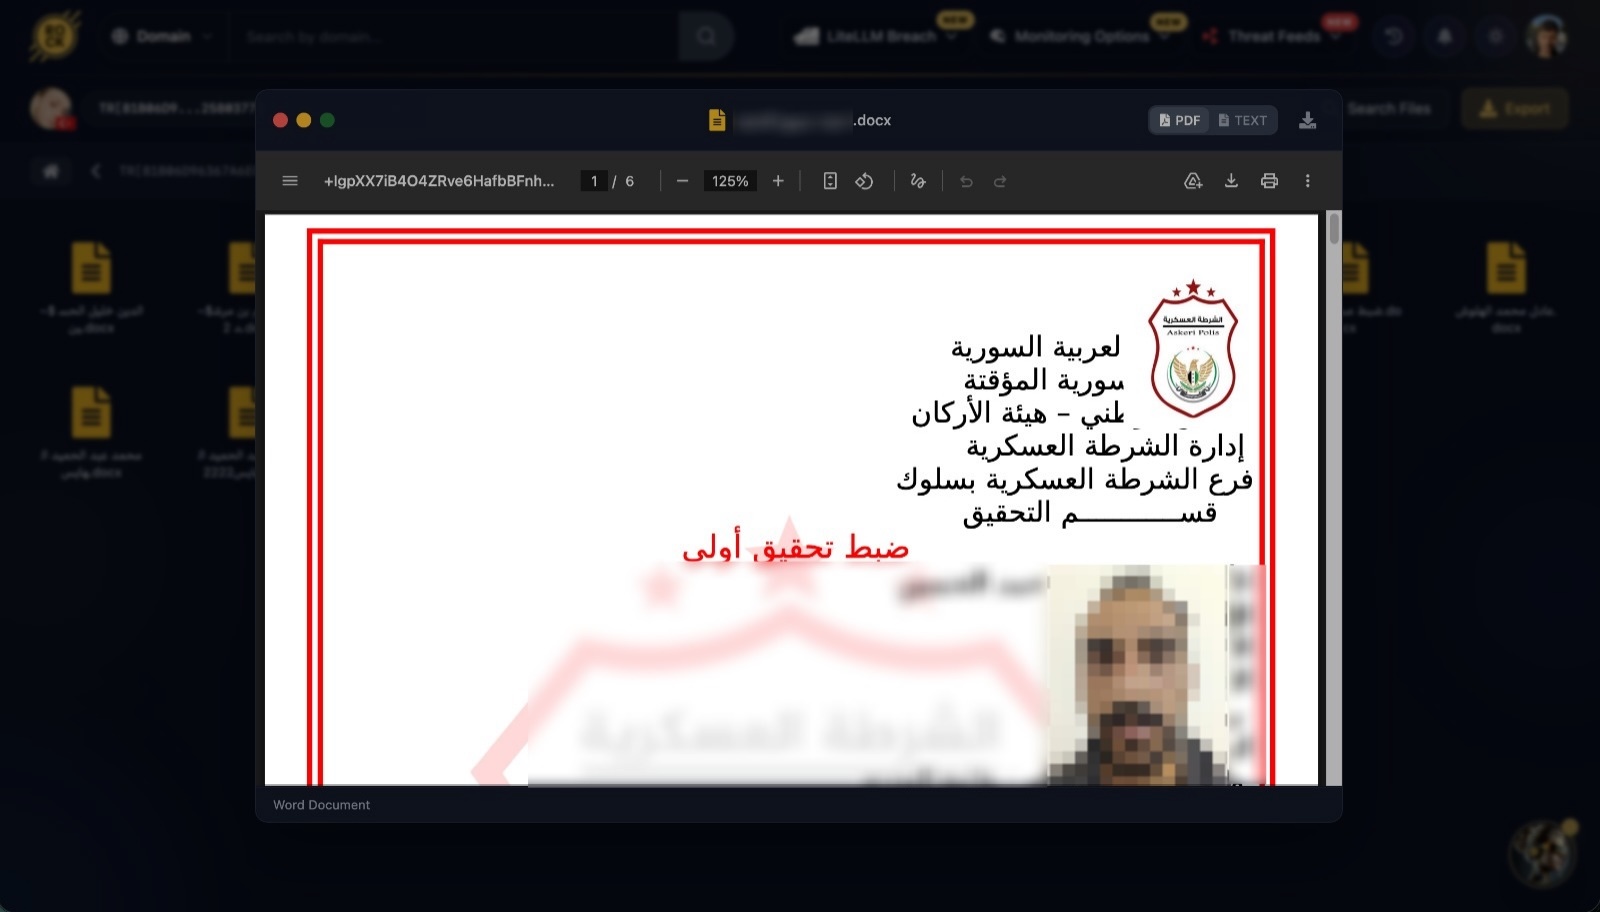
A RedLine infostealer infection on a Syrian National Army Military Police officer’s computer exposed active interrogation records, detainee photographs, family details, and signed confessions from the Suluk unit. The recovered files also showed alleged espionage claims, a soldier-run smuggling network, and at least one rewritten statement, all stored unencrypted on the officer’s desktop. #RedLine #SyrianNationalArmy #MilitaryPoliceSuluk #AhraralSharqiya #JayshalMajd #20thDivision