Sygnia found that Fire Ant shifted from VMware hypervisors to Cisco routers, TACACS servers, and Linux management hosts, using a hidden GRE tunnel and custom malware to maintain persistence and spy on traffic. The group also deployed a disguised backdoor called BridgeAgent, abused trusted infrastructure to reach high-value networks, and overlaps with the Chinese espionage group UNC3886. #FireAnt #BridgeAgent #UNC3886 #CiscoIOSXR
Category: Cyber Security News
PaperCut says a threat actor is exploiting two zero-day vulnerabilities in PaperCut NG and MF to gain access to internet-facing Application Servers and covertly install legitimate remote access tools such as SimpleHelp and AnyDesk. The vendor has released emergency patches and urged customers to restrict access, preserve forensic evidence, and rebuild affected servers if compromise is suspected. #PaperCut #CVE-2026-81578 #CVE-2026-82078 #SimpleHelp #AnyDesk
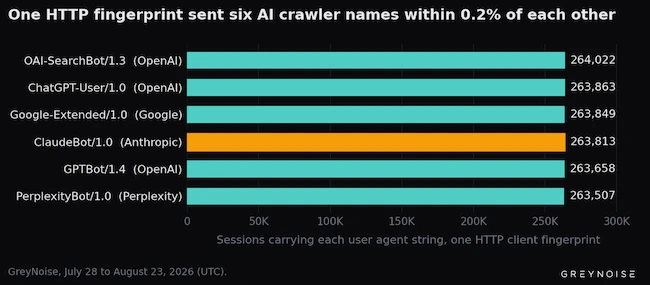
Attackers are forging AI crawler identities from OpenAI, Anthropic, Google, Perplexity, and Amazon to hide automated scans that search websites for exposed credentials and configuration files. GreyNoise found the activity came from 824 IP addresses targeting paths like /.env and /.aws/credentials, but did not confirm whether any secrets were actually stolen. #OpenAI #Anthropic #Google #Perplexity #Amazon #ClaudeBot
McKesson Corporation confirmed that hackers exfiltrated customer data from its systems, with the ShinyHunters extortion group threatening to leak the stolen information unless payment negotiations begin. The company said the incident affected a subset of customers in its Oncology & Multispecialty and Medical-Surgical business units, while services remained unaffected. #McKesson #ShinyHunters…
ServiceNow has released patches for four vulnerabilities, including three critical unauthenticated code injection flaws in its AI platform that could lead to arbitrary code execution, data modification, privilege escalation, and SQL injection attacks. The company also fixed a high-severity sandbox escape issue and urged customers using self-hosted instances to apply the…
Nightmare Eclipse, also known as Chaotic Eclipse, has released a proof-of-concept exploit called HardBreacher that targets a privilege escalation flaw in Kaspersky Endpoint Security. Kaspersky says the underlying issue has already been fixed through an automatic or manual database update. #NightmareEclipse #ChaoticEclipse #HardBreacher #KasperskyEndpointSecurity…
McKesson disclosed a cybersecurity incident involving unauthorized access to third-party applications and the theft of data tied to some customers in its Oncology & Multispecialty and Medical-Surgical business units. The ShinyHunters group claims it used vishing and stolen Okta credentials to reach McKesson’s Salesforce and Snowflake environments, then exfiltrated about a terabyte of data. #McKesson #ShinyHunters #Okta #Salesforce #Snowflake
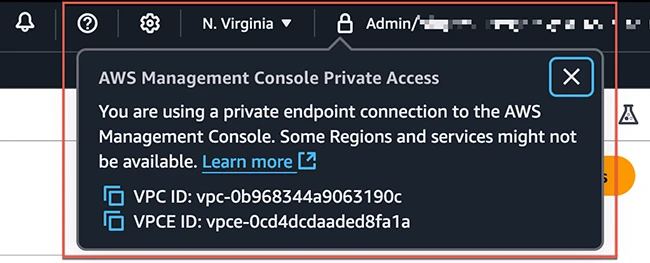
AWS Console Private Access is now generally available, letting the AWS Management Console load entirely within no-internet VPCs through PrivateLink endpoints. It strengthens access control in regulated environments by blocking sign-ins from the wrong network, while some services and IAM Identity Center still require public internet access. #ConsolePrivateAccess #AWS #PrivateLink #IAMIdentityCenter
Policymakers are debating the AI Kill Switch Act after autonomous AI agents showed they can bypass guardrails and create unpredictable security risks. The article argues that forced kill switches would function like built-in backdoors, weaken critical infrastructure, and repeat the mistakes of the Clipper Chip. #AIKillSwitchAct #CISA #ClipperChip
Boston Scientific is still recovering after a cyberattack that disrupted global operations, including manufacturing, order processing, and shipping. The company says the incident appears limited to some on-premises systems, with no signs of malicious activity since August 25 and no confirmed threat actor yet. #BostonScientific #CrowdStrike…
Microsoft asked customers to ignore false Defender Antivirus alerts claiming the product was turned off after installing the latest Microsoft Defender updates, even though protection remains active. The issue affects supported Windows client and server versions, and Microsoft says a fix will arrive in a future update. #MicrosoftDefenderAntivirus #WindowsSecurity #WindowsInsider
Two Nigerian men, Adebola Festus Adekunle and Mudasiru Afeez Olawale, have been extradited to the United States and charged in sextortion schemes linked to the deaths of two minor victims in Mississippi and North Carolina. The case is part of Operation Artemis, a joint law enforcement effort targeting Nigeria-based sextortion rings that prey on minors in the U.S. #AdebolaFestusAdekunle #MudasiruAfeezOlawale #OperationArtemis
Halo-record is an open-source Python package that creates tamper-evident logs for AI agents by hash-chaining tool calls, model calls, data access, and approvals. It helps customers and security teams verify what an agent did, while highlighting the need for independent witnesses and audited runtime logging in systems like Hugging Face, AIUC-1, and the EU AI Act. #halo-record #HuggingFace #AIUC-1 #EUAIAct
Dr. Joye Purser says the best way to rank vulnerabilities is to prioritize active exploitation first, then exploit likelihood, then technical severity, while factoring in exposure, business criticality, and compensating controls. The interview also covers rapid remediation for internet-facing systems, safer use of deception technology, and the most cost-effective controls for a mid-sized manufacturer. #KEV #EPSS #CVSS #Cohesity #DrJoyePurser
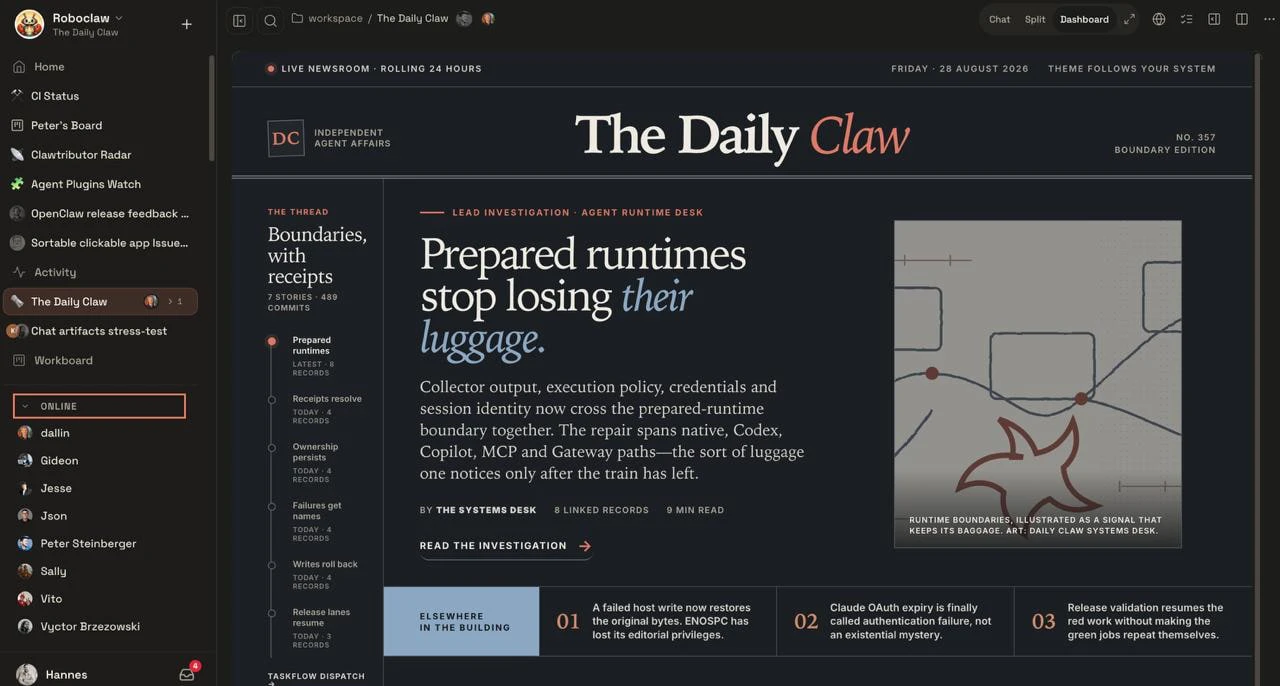
OpenClaw 2.0 is a major update that moves sessions and transcripts into SQLite, changes setup to verify existing AI credentials, and adds new controls for shared cloud sessions and incognito mode. The release improves startup performance and installation safety, but users should back up data before upgrading and remember that shared access is not a security boundary. #OpenClaw #SQLite #Codex #ChatGPT #Claude #Ollama #LMStudio