
Elastic denies claims that its Defend EDR product is impacted by a zero-day vulnerability, despite previous warnings from Ashes Cybersecurity. The company emphasizes that there is no evidence of a flaw leading to detection bypass or remote code execution. #ElasticDefend #AshesCybersecurity #ZeroDayVulnerability…
Category: Cyber Security News

A critical vulnerability in Google Chrome’s V8 JavaScript engine has been identified, potentially allowing remote code execution. Users are urged to update to the latest Chrome version to stay protected from exploitation attempts. #CVE‑2025‑9132 #V8 #GoogleChrome…
Recent Windows 11 24H2 updates are causing data corruption issues with some SSD and HDD models, especially those with Phison NAND controllers. Microsoft and Phison are working together to resolve the problem, but users are advised to avoid large data writes te…

A young man from Oregon has been charged with developing and managing the RapperBot DDoS-for-hire botnet that targeted victims across 80+ countries. The operation included extensive law enforcement efforts to seize control and dismantle the malicious network. #RapperBot #DDoSForHire…

North Korean threat actors, possibly working from China or mimicking Chinese tactics, targeted South Korean diplomatic missions with sophisticated spear-phishing campaigns using cloud platforms and GitHub. They employed open-source malware, like Xeno RAT and MoonPeak, to infiltrate systems and exfiltrate sensitive information, blending operational tactics across regions. #Kimsuky #MoonPeak…

A comprehensive BIA is essential for building an effective Business Continuity and Disaster Recovery (BCDR) strategy, helping businesses identify critical functions and assess potential impact of disruptions. Leveraging tools like Datto enhances recovery readiness by automating backups, testing, and ransomware detection, ensuring resilience amidst evolving threats. #BusinessImpactAnalysis #Datto #CyberThreats…
A security researcher uncovered several vulnerabilities in Intel’s internal websites, potentially exposing millions of employee details. Intel swiftly patched these flaws, emphasizing their commitment to security but highlighting gaps in their bug bounty coverage. #IntelVulnerabilities #EmployeeDataExposure…
Google and Mozilla have issued security patches for Chrome and Firefox to address high-severity vulnerabilities, including remote code execution risks. These updates help protect users from potential exploits targeting browser weaknesses using advanced vulnerability detection tools like Google’s Big Sleep AI. #V8JavaScriptEngine #BigSleepAI…
Pharmaceutical company Inotiv experienced a cybersecurity breach involving ransomware, which encrypted its internal systems and caused operational disruptions. The Qilin ransomware group claimed responsibility, stealing valuable data and adding Inotiv to its leak site. #QilinRansomware #InotivDataLeak…

A large-scale DDoS-for-hire botnet called Rapper Bot has been dismantled, with law enforcement arresting Ethan Foltz, the alleged mastermind. The operation was responsible for hundreds of thousands of attacks globally, targeting critical infrastructure and major organizations. #RapperBot #DDoSforHire…
Microsoft released emergency out-of-band updates to fix a bug caused by August 2025 security patches, which disrupt Windows recovery and reset functions. These updates are crucial for systems affected by the known issues with Windows 10 and Windows 11 versions…
Microsoft has fixed a known issue causing Windows upgrade failures with error code 0x8007007F on some Windows 11 and Windows Server systems. The company recommends retrying upgrades for affected devices and has released emergency patches for other Windows upda…

Citizen Lab’s new report reveals that several popular VPN providers are controlled by the same entity and employ insecure security practices, risking user privacy and security. The research highlights the sharing of code, security flaws, and hidden ownership among VPN apps like Turbo VPN and VPN Monster, linked to Chinese security…
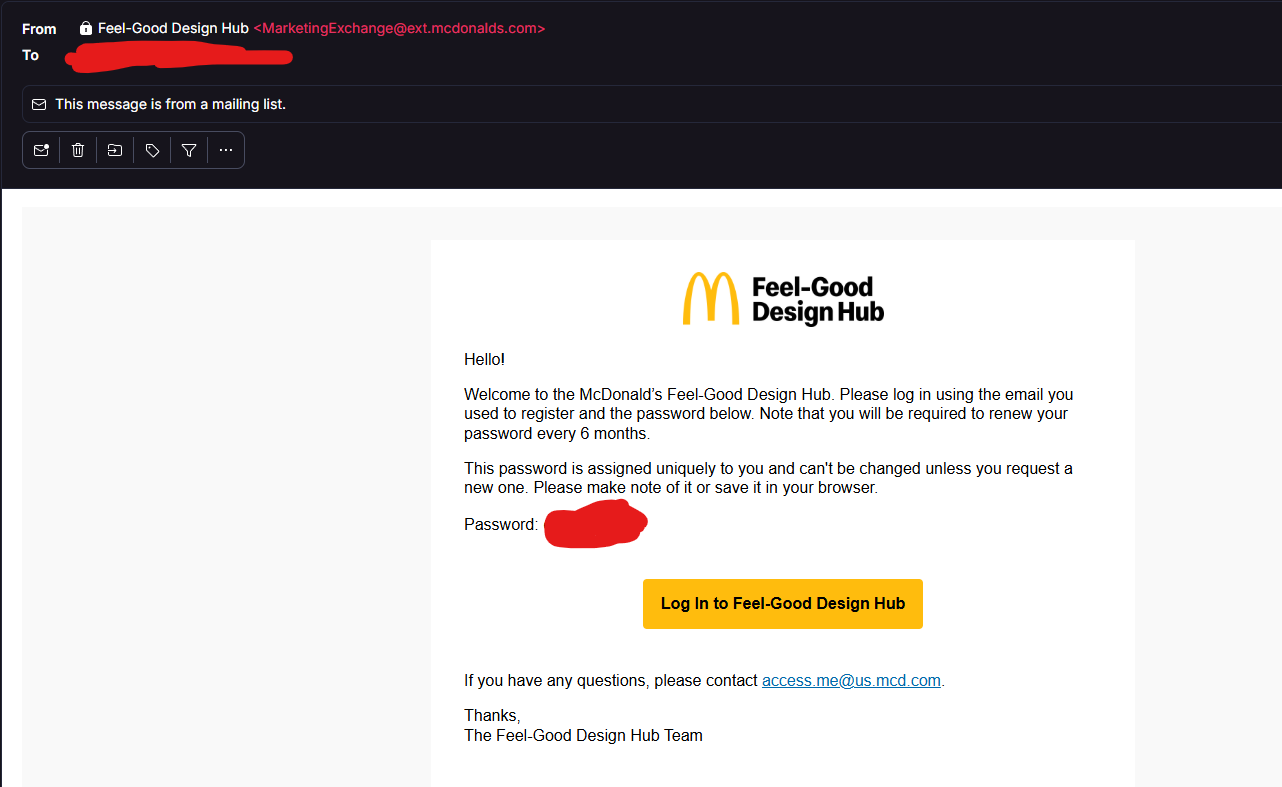
An independent researcher uncovered multiple security vulnerabilities within McDonald’s digital systems, exposing risks from client-side validation issues to sensitive data leaks. The findings highlight the importance of comprehensive cybersecurity practices and responsible reporting channels. #McDonalds # cybersecuritybreach…

The cybersecurity landscape this week highlights the emergence of PipeMagic, a modular backdoor exploiting a Windows zero-day, used by threat actors like Storm-2460 and RansomEXX to deploy ransomware through fake ChatGPT apps. Additionally, nation-state campai…