
Google is introducing ‘Developer Verification’ to enhance Android security by blocking malware from sideloaded apps outside the Google Play store. This initiative aims to reduce the significant threat posed by malicious apps from internet sources, expanding protections to developers beyond Google Play. #AndroidSecurity #DeveloperVerification
Category: Cyber Security News
This article discusses a multi-national effort to combat North Korea’s scheme of illicitly employing its citizens in IT roles to fund malicious activities. Key players include the U.S., Japan, and South Korea, who are working together to share intelligence and prevent financial and cyber threats linked to North Korea. #LazarusGroup #NorthKoreaITScheme…

The U.S. CISA has added two Citrix vulnerabilities and one Git-related vulnerability to its KEV list, with some actively exploited in the wild, highlighting ongoing threats involving Citrix products. Organizations using NetScaler ADC and Gateway are urged to update their systems to mitigate these high-severity security risks. #CitrixVulnerabilities #NetScalerExploits…
Nevada is experiencing a two-day cyberattack that has disrupted its government websites, communication systems, and online platforms, leading to the closure of all state offices. Authorities continue to investigate the incident, and emergency services remain unaffected while working to restore normal operations. #NevadaCyberattack #GovernmentSystemsDisruption
Hackers exploited a Salesforce integration via the Salesloft platform to steal sensitive credentials including AWS keys and Snowflake tokens. The ShinyHunters group claims responsibility for these coordinated attacks, which also involved breaching downstream cloud services. #ShinyHunters #SalesforceBreaches

Researchers have developed Sni5Gect, an open-source toolkit that can intercept and inject messages in 5G networks to downgrade connections or crash devices without using rogue base stations. This groundbreaking method exploits unencrypted early-stage messages, revealing significant vulnerabilities in 5G communication protocols. #Sni5Gect #5Gvulnerabilities…

Citrix has issued security updates for three vulnerabilities in NetScaler ADC and Gateway, including one actively exploited in the wild. These flaws pose serious risks like remote code execution, denial-of-service, and access control issues. #CVE-2025-7775 #NetScalerADC #CISA…

Legacy Treatment Services in New Jersey experienced a significant data breach in October 2024, affecting over 41,000 individuals with sensitive personal and medical information compromised. The ransomware group Interlock claimed responsibility, leaking stolen data and threatening further extortion. #Interlock #LegacyTreatmentServices…

Sen. Ron Wyden has called for an independent review of the federal judiciary’s cybersecurity following recent breaches involving sensitive case data. He criticized the courts’ negligence and incompetence, urging the Supreme Court to adopt stronger security measures and transparency. #Wyden #FederalCourtBreach…
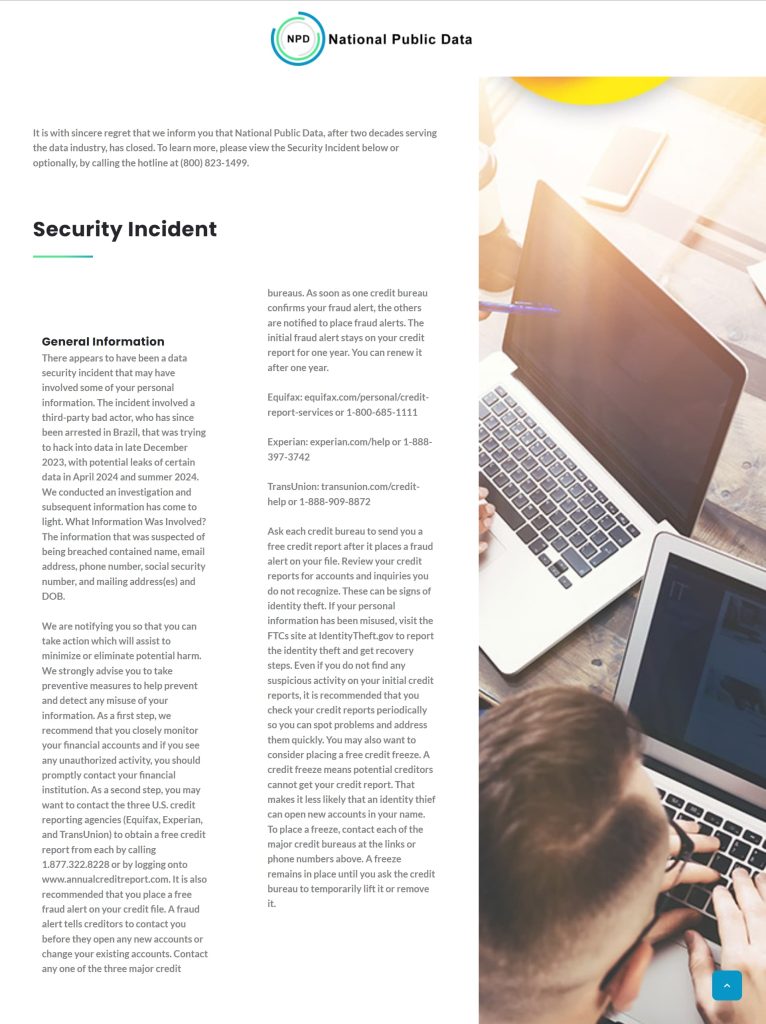
National Public Data has resumed operations under new ownership after experiencing a massive leak of 2.9 billion records, raising concerns about data privacy and broker accountability. Despite efforts to offer opt-outs, leaked personal information remains accessible and vulnerable to criminal misuse. #JericoPictures #PerfectPrivacyLLC…

A Chinese software developer was sentenced to four years in prison for intentionally damaging his US employer’s computer systems using malicious code, including a kill switch. The insider threat resulted in system crashes, data deletion, and significant financial losses, with no evidence of nation-state involvement. #DavisLu #InsiderThreat #OhioEmployer #SystemSabotage…
Nissan Japan’s subsidiary, Creative Box Inc., experienced a data breach after unauthorized access, with the Qilin ransomware group claiming to have stolen four terabytes of sensitive design data. The incident highlights the ongoing threat of ransomware groups exploiting vulnerabilities to steal valuable corporate information. #QilinRansomware #CreativeBoxInc

Despite significant investments in GDPR compliance, many businesses still face risks due to employees neglecting basic password practices. Effective, continuous employee training combined with tools like Passwork can transform compliance into a strategic security advantage. #GDPR #PasswordManagement
The U.S. CISA has issued warnings about a high-severity vulnerability in Git CVE-2025-48384 that could lead to arbitrary code execution. Additionally, CISA highlights two Citrix Session Recording vulnerabilities CVE-2024-8068 and CVE-2024-8069, urging timely patching before September 15th. #CVE202548384 #CitrixSessionRecordingVulnerabilities

A large-scale cybercriminal campaign called ShadowCaptcha is exploiting compromised WordPress sites to deliver information stealers, ransomware, and cryptocurrency miners using social engineering tactics and obfuscated scripts. The campaign primarily targets websites in multiple countries and employs advanced techniques like DLL side-loading and anti-debugging to maintain stealth. #ShadowCaptcha #EpsilonRed #HelpTDS…