
Chess.com experienced a data breach through a third-party file transfer tool, exposing personal information of over 4,500 users. The company confirmed that no banking or login credentials were compromised, and law enforcement was notified immediately. #WingFTP #CrushFTP #ChesscomDataBreach…
Category: Cyber Security News

The US Department of State has announced rewards for information on three Russian FSB officers linked to extensive cyberattacks on global energy infrastructure. These officers, part of FSB’s Center 16, are accused of deploying Havex malware and spear-phishing campaigns in operations like Dragonfly and Dragonfly 2.0, targeting over 380 energy companies…
Browser-based attack techniques have become the primary threat in 2025, targeting the browser as the new battleground for enterprise security. Effective detection and response are crucial as attackers exploit browser vulnerabilities, phishing, malicious code, and OAuth integrations to compromise business data. #AiTM #ClickFix
The French data protection authority fined Google €325 million for cookie violations and unauthorized advertising in Gmail. This action highlights ongoing concerns about data privacy and compliance with European regulations. #CNIL #Google #CookieRegulations #DataPrivacy
TP-Link has announced a critical zero-day vulnerability affecting multiple router models, with patches underway for different regions. CISA has also issued warnings about other exploited vulnerabilities in TP-Link routers, linked to the Quad7 botnet threat actor. #TPLinkVulnerability #Quad7Botnet
Researchers from Palo Alto Networks have identified a new AI supply chain attack called ‘Model Namespace Reuse,’ which exploits the deletion or transfer of model names on platforms like Hugging Face to deploy malicious AI models. The attack demonstrates significant risks against cloud platforms such as Google Vertex AI and Microsoft…
Apple is now accepting applications for the 2026 Security Research Device Program, offering security researchers specially configured iPhones for vulnerability discovery. The program provides advanced tools and early access to security projects, with rewards for identified security issues. #SRDP #AppleSecurityResearch…

Google’s latest Android Security Bulletin patching 111 vulnerabilities includes two actively exploited zero-day flaws affecting Android Runtime and the Linux kernel. The severity of these vulnerabilities emphasizes the importance of immediate updates to protect devices from privilege escalation attacks. #CVE-2025-48543 #CVE-2025-38352…

This article covers the latest episode of the Black Hat USA 2025 CISO Podcast Series, focusing on the dual nature of AI in cybersecurity. It emphasizes the evolving role of CISOs in balancing innovation with responsibility when deploying AI tools. #BlackHatUSA #CISO #ArtificialIntelligence #CybersecurityLeadership…
Researchers have uncovered malware called Stealerium that automates sextortion practices by capturing webcam images of victims browsing pornographic sites and stealing sensitive data. The malware, distributed freely on Github, targets individuals and small groups, increasing privacy invasions and blackmail risks. #Stealerium #infostealer #cyberblackmail…
This article discusses the security breach involving TLS certificates for 1.1.1.1, which could enable man-in-the-middle attacks on Cloudflare’s DNS service. The incident highlights vulnerabilities in the public key infrastructure and issues with certificate transparency oversight. #TLSCertificates #CertificateTransparency…

School District 5 in South Carolina suffered a significant ransomware attack by Interlock, exposing personal data of over 31,000 individuals. The incident caused disruptions to school operations, delayed payroll, and prompted offers of credit monitoring and identity theft insurance. #Interlock #SchoolDistrict5 #SouthCarolina #RansomwareAttack…

Cloudflare successfully thwarted the largest DDoS attack on record, reaching 11.5 Tbps for 35 seconds without affecting online services. The attack was a massive UDP flood originating from compromised IoT devices and multiple cloud providers, highlighting the rising scale of cyber threats. #DDoS #IoTDevices…
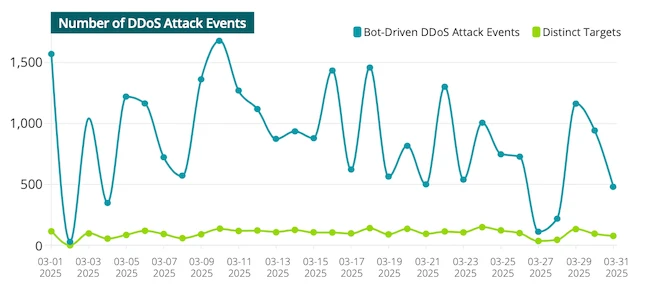
In the first half of 2025, global DDoS attacks surged, driven by geopolitical conflicts and increased accessibility of attack tools like AI automation and DDoS-for-hire services. Hacktivist groups such as NoName057 and DieNet have intensified their campaigns targeting critical infrastructure, emphasizing the need for advanced DDoS defenses. #NoName057 #DieNet #AIautomation…
Microsoft’s August 2025 security updates have introduced new User Account Control prompts and app installation issues for non-admin users across Windows platforms, due to a patch addressing the CVE-2025-50173 privilege escalation vulnerability. Microsoft is working on fixes including enabling MSI repair operations without UAC prompts and providing temporary workarounds for affected users. #CVE202550173 #MSI #WindowsUpdate