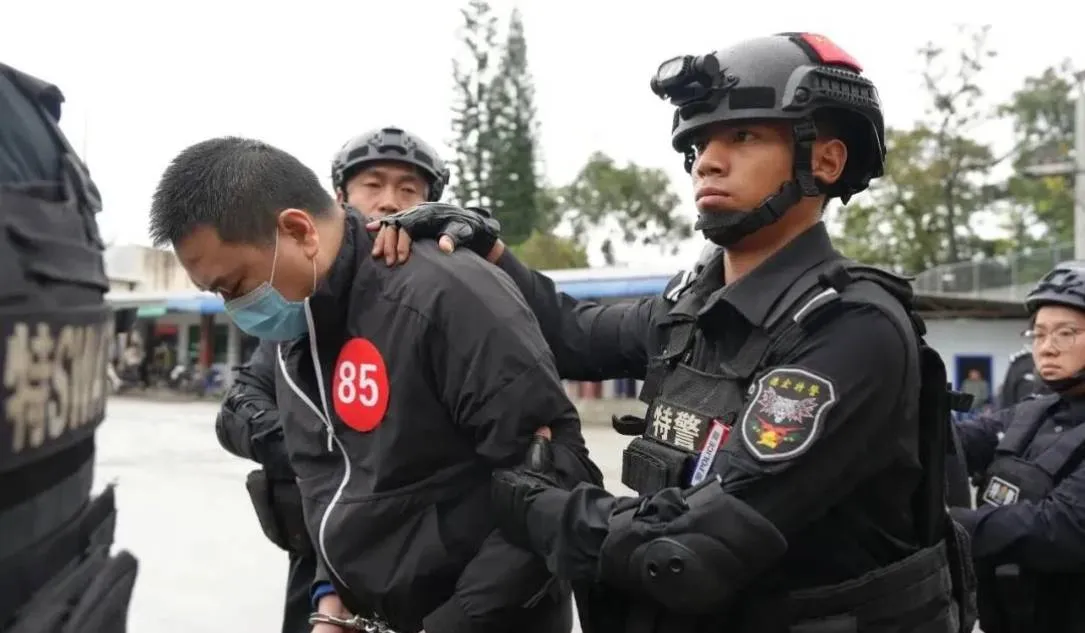
The U.S. Treasury Department has imposed sanctions on individuals and entities involved in cyber scams and illegal activities across Myanmar and Cambodia, aiming to disrupt extensive fraud operations that have caused over $10 billion in losses. These actions target scam centers, forced labor camps, and money laundering networks linked to criminal…
Category: Cyber Security News

A cyberattack on Jaguar Land Rover disrupts its operations and poses a serious threat to the UK’s economic growth, highlighting deficiencies in the government’s cybersecurity regulations. Experts warn that delayed legislation and insufficient strategic action could leave Britain vulnerable to more severe cyber threats. #JaguarLandRover #UKCybersecurity #CyberSecurityBill…

LockBit, once a dominant ransomware threat, is attempting a comeback with its new LockBit 5.0 update, featuring revamped ransomware panels and enhanced evasion capabilities. Despite these efforts, law enforcement actions and rival groups’ rise have significantly hindered its resurgence. #LockBit #LockBit5.0 #RansomwareDecline…
Salesloft experienced a supply chain-style breach starting with its GitHub account in March, leading to OAuth token theft and subsequent Salesforce data breaches in August. Multiple threat actors, including ShinyHunters and Scattered Spider, were involved, targeting sensitive customer data across various organizations. #GitHubAttack #OAuthTokens #SalesforceDataTheft #SupplyChainBreach
This article reports the largest supply chain attack in history, involving malware injection into popular npm packages with over 2.6 billion weekly downloads. The attack was carried out through compromised maintainer accounts and sophisticated phishing schemes targeting developers. #npmjshelp #supplychainattack

Calcio, a major illegal sports streaming platform with over 120 million visits, was shut down through a collaboration between ACE and DAZN. This action highlights ongoing efforts to combat sports piracy and protect the integrity of live sports broadcasting. #Calcio #ACE #DAZN #IllegalStreaming
Lovesac, an American furniture retailer, experienced a cybersecurity breach exposing personal data of an undisclosed number of individuals. The RansomHub ransomware gang claimed responsibility, threatening to leak stolen data if demands are not met. #RansomHub #DataBreach

Cybersecurity researchers have uncovered a sophisticated malware campaign that uses paid search ads and manipulated GitHub links to deliver malicious payloads, targeting Western European IT and software firms. The campaign employs advanced evasion techniques like encrypted payloads and GPU-based decryption routines, posing significant threats to organizations. #GPUGate #Malvertising…

Salesloft’s data breach originated from a compromised GitHub account, allowing threat actors to access and manipulate coding repositories. The incident involved sophisticated reconnaissance and theft of OAuth tokens, impacting multiple organizations. #UNC6395 #GitHub…
AI-powered ransomware, including the research prototype Ransomware 3.0, now utilizes large language models to automate and personalize cyberattacks without human intervention. Real-world threats have been observed where AI tools like Claude Code are exploited for reconnaissance, data exfiltration, and creating sophisticated malware—signifying an alarming evolution in cybercrime techniques. #Ransomware3.0 #ClaudeCode…

Chinese hackers linked to the threat group APT41 attempted to spy on US trade organizations through a malware campaign before trade talks. Google’s Mandiant identified the attack, emphasizing the threat posed by state-sponsored cyber espionage. #APT41 #ChineseHackers…

WSUS, an old on-premises patch management tool, is being phased out in favor of modern cloud-native solutions like Action1, which offers superior ease of deployment and comprehensive coverage. As organizations seek scalable, automated, and real-time patch management, Action1 provides a significant upgrade for today’s cybersecurity needs. #WSUS #Action1

Modern organizations face a new threat where attackers pose as legitimate employees through fake identities and AI-generated profiles, bypassing traditional email security measures. Implementing zero standing privileges (ZSP) can effectively restrict persistent access, reducing the risk of infiltration like North Korean operatives exploiting remote hiring. #NorthKorea #ZeroTrust #IdentityFraud…

Nepal’s government imposed a social media ban, leading to violent protests and casualties as police clashed with demonstrators. The restrictions were justified by officials due to concerns over cybercriminals and disinformation, but faced heavy criticism from rights groups and the public. #NepalBan #SocialMediaRestrictions…
Cybercriminals exploited secrets stolen during the Nx supply chain attack to publicly release over 6,700 private repositories, leading to widespread data exposure. The attack involved malicious Nx package versions, AI CLI exploitation, and data exfiltration of sensitive credentials and files, impacting hundreds of users and organizations. #NxSupplyChain #s1ngularity #GitHubRepositories #AIExfiltration…