
Apple’s Memory Integrity Enforcement (MIE) introduces a groundbreaking system-wide security feature to protect iPhone users from spyware by utilizing advanced memory tagging and hardware protections. This innovation aims to significantly disrupt exploit chains used by mercenary spyware and enhance overall memory safety on consumer devices. #MemoryTaggingExtension #SpywareProtection…
Category: Cyber Security News

SAP has released security patches addressing multiple critical vulnerabilities in SAP NetWeaver and SAP S/4HANA that could lead to remote code execution, file uploads, and unauthorized access. Users should promptly apply these updates to mitigate potential exploitation risks, especially given recent active threats in the wild. #SAPNetWeaver #S4HANA #CVE202542944 #CVE202542922…

Adobe has issued a warning about a critical security flaw, CVE-2025-54236, in its Commerce and Magento Open Source platforms, which could allow attackers to control customer accounts. While no exploits have been observed in the wild, Adobe has released a hotfix and protective WAF rules to prevent potential attacks. #CVE202554236 #MagentoVulnerability…

Daily Recap, A sweeping review of recent cybersecurity incidents and industry shifts, from breaches impacting individuals and organizations to supply-chain compromises and AI-driven threats. It highlights notable events like the Sapphos data exposure, Plex breach, Nexar’s 130 TB of video, and the evolving landscape of ransomware, supply-chain attacks, and state-backed surveillance, along with emerging defenses and policy responses. #Sapphos #Plex #Nexar #WayneBreach #Wealthsimple #Lovesac #Salesloft #GhostAction #npmHijack #Chaos #ScatteredSpider #LockBit #LunaLock #APT41 #SaltTyphoon #KazMunayGas #JLR #Calcio #NozomiNetworks #ObservoAI #BlackHat

Shadow AI Agents represent a growing cybersecurity threat where unseen, unauthorized AI agents operate within enterprise systems, impersonating trusted users and risking data breaches. This emerging challenge requires new detection and governance strategies to maintain security and control. #ShadowAI #NonHumanIdentities…

A new Android malware called RatOn has evolved into a highly sophisticated threat, capable of NFC relay attacks, automated money transfers, and device fraud. It primarily targets financial apps and cryptocurrency wallets, with active development and deployment noted in the Czech and Slovakian regions. #RatOn #NFSkate…

The U.S. Department of Justice is actively pursuing civil forfeiture of stolen cryptocurrency, including $5 million in Bitcoin from SIM swapping attacks. These thefts involve unauthorized transactions and money laundering, often ending in online casinos or illicit schemes. #SIMSwapping #CryptoFraud…

A U.S. federal court has unsealed charges against Ukrainian ransomware hacker Volodymyr Viktorovich Tymoshchuk for controlling strains like LockerGoga, MegaCortex, and Nefilim, which targeted hundreds of organizations worldwide. Law enforcement is actively pursuing him and other members involved in these ransomware operations, which caused significant financial and operational damage. #LockerGoga #MegaCortex…

A major U.S. blood center, New York Blood Center, experienced a significant ransomware attack that compromised sensitive patient and employee data. This incident highlights ongoing cybersecurity risks faced by healthcare organizations and their efforts to notify affected individuals. #NYBloodCenter #RansomwareAttack #HealthcareCybersecurity…

KuCoin’s security team uncovers a sophisticated Lazarus Group phishing campaign targeting financial and crypto organizations through fake interviews, poisoned code, and exploiting recent vulnerabilities. The campaign demonstrates Lazarus’s evolving tactics, including social engineering, supply chain attacks, and malware deployment. #LazarusGroup #APT38 #CryptoTargeting…
Adobe has released patches for nearly twenty vulnerabilities across nine major products, addressing critical flaws in ColdFusion and Commerce that pose significant exploitation risks. Although no active exploitation has been reported, these vulnerabilities are highly prioritized for immediate remediation to prevent potential attacks. #ColdFusion #CVE202554261 #Commerce #Magento #AdobeUpdate…
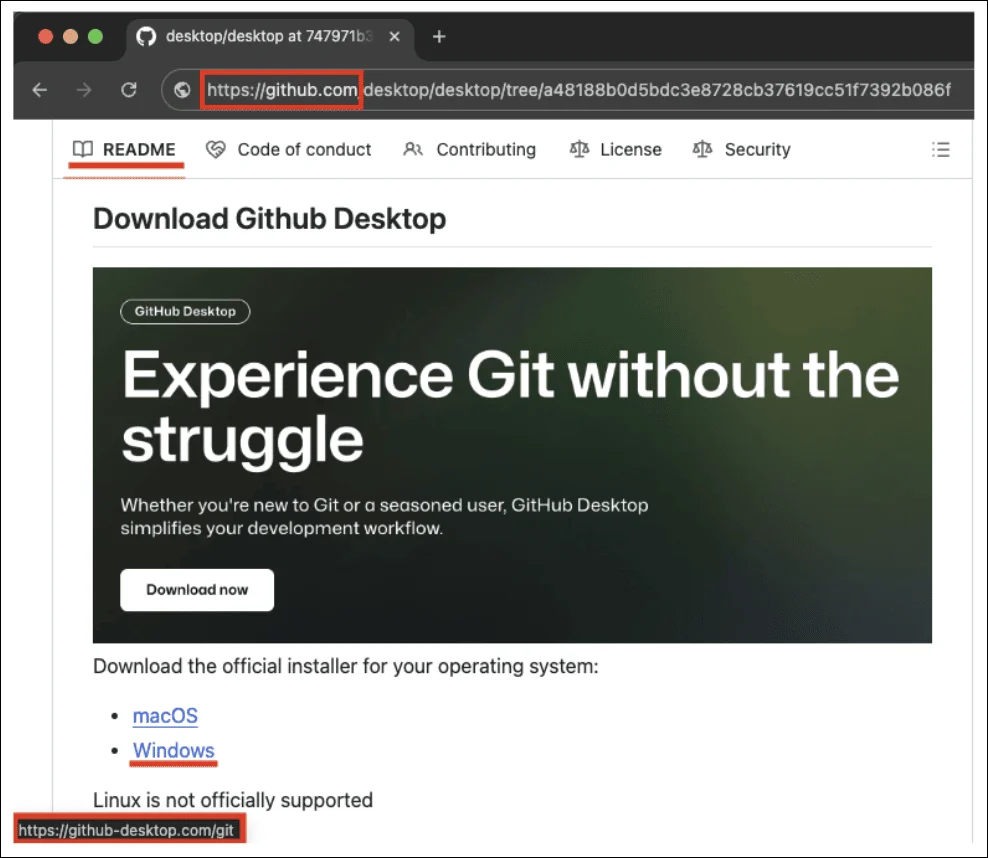
Researchers have uncovered a malicious campaign targeting EU IT workers, delivering fake GitHub Desktop installers via sophisticated malvertising tactics. The campaign leverages GPU-based decryption and evasion techniques to evade detection and enables potential credential theft and lateral movement. #GPUGate #AtomicStealer…

A suspected Chinese intelligence operation has been using fake websites and job postings to recruit former U.S. government employees and policy experts. Despite their crude appearance, these efforts could pose significant threats, highlighting the importance of vigilance and reporting suspicious activities. #ChineseIntelligence #ForesightNetwork…
SAP has released security advisories addressing multiple product vulnerabilities on September 9, 2025, urging users to update their systems. The Cyber Centre reports active exploitation of CVE-2025-42957 in the wild, emphasizing the importance of applying patches. #SAPNetWeaver #CVE202542957…
The U.S. Department of the Treasury has imposed sanctions on major cyber scam networks operating in Southeast Asia, highlighting their ties to organized crime and human rights abuses. These actions aim to isolate these threat actors financially and legally, despite no arrests being made. #YataiInternationalHoldings #HengHeBavet