
China is implementing stricter cybersecurity regulations requiring network operators to report severe incidents within one hour, effective November 1, 2025. These measures aim to bolster protection for critical infrastructure and respond more swiftly to data breaches and cyberattacks. #CyberspaceAdministrationOfChina #CybersecurityLaw #DataBreaches #CriticalInfrastructure…
Category: Cyber Security News

Chinese-speaking users are targeted by a sophisticated SEO poisoning campaign that distributes malware through fake software sites. The campaign involves manipulating search rankings and using lookalike domains to infect victims with variants of Gh0st RAT, including HiddenGh0st, Winos, and kkRAT. #HiddenGh0st #Winos #kkRAT…
The FBI has issued a FLASH alert warning about cyber threat groups UNC6040 and UNC6395 targeting Salesforce environments through different attack vectors, including social engineering and OAuth token theft. These campaigns have resulted in significant data breaches across major organizations, with hackers aiming to exfiltrate and extort sensitive customer and corporate information. #UNC6040 #UNC6395 #ShinyHunters #Lapsus #SalesforceSecurity

IBM X-Force reports on Hive0154, a China-aligned threat group, reveals their use of advanced malware such as Toneshell9 and SnakeDisk to target specific regions like Thailand. The group employs sophisticated techniques like proxy-aware C2 communication and region-specific USB Worms, demonstrating their persistent and well-developed capabilities. #Hive0154 #Toneshell9 #SnakeDisk…

The FBI and DHS/CISA have issued an alert about cybercriminal groups UNC6040 and UNC6395 targeting Salesforce data through vishing, API exploitation, and compromised OAuth tokens. Organizations are urged to enhance security measures, monitor for suspicious activity, and review indicators of compromise. #UNC6040 #UNC6395 #SalesforceSecurity…

The weekly recap highlights continued double-extortion ransomware activity and copycat families, with Yurei leveraging open-source Prince code and healthcare remaining a major target. It also details rapid RATs, APT campaigns, supply-chain compromises, and evolving extortion trends, underscoring cross‑actor intrusions, AI‑assisted threats, and defensive guidance #Yurei #SafePay #BlackNevas #LunaLock #CyberVolk #ZynorRAT #MostereRAT
Threat actor WhiteCobra is attacking VS Code, Cursor, and Windsurf users by distributing malicious extensions through popular extension repositories. Their campaign involves sophisticated impersonation tactics and the use of malware like LummaStealer to drain cryptocurrency wallets. #WhiteCobra #LummaStealer
Microsoft has announced the end of support for Windows 10 on October 14, 2025, urging users to upgrade to Windows 11 or use the Extended Security Updates program. Windows 11 now surpasses Windows 10 in adoption, with over 53% of Windows systems running the latest OS, highlighting a gradual shift in the Windows ecosystem. #Windows10 #Windows11 #ExtendedSecurityUpdates
A new phishing-as-a-service platform called VoidProxy targets Microsoft 365 and Google accounts using sophisticated adversary-in-the-middle tactics. It employs Cloudflare-protected malicious sites and intercepts credentials, MFA codes, and session cookies to facilitate account compromise. #VoidProxy #AitM #Okta #Microsoft365 #Google

Daily Recap, researchers warn the VoidProxy phishing-as-a-service is actively bypassing MFA to steal Google and Microsoft session tokens and enable account takeovers, urging stronger auth like passkeys. The recap highlights threats from bootkits like HybridPetya bypassing UEFI Secure Boot, Akira ransomware affiliates exploiting patched SonicWall CVE-2024-40766, critical patches for Chrome, Cisco IOS XR, and Samsung, and ongoing espionage, data theft, and state-backed campaigns affecting governments and enterprises. #VoidProxy #HybridPetya #Akira #Pegasus #Predator #EggStreme #SonicWall #Chrome #Windows11 #Salesforce #ShinyHunters #INC #DELMIA

The FBI has issued alerts on cyber threats from groups UNC6040 and UNC6395 targeting Salesforce platforms through various attack methods, including OAuth token exploitation and vishing campaigns. Companies like Salesloft and organizations using Salesforce are advised to enhance their security measures, as threat actors continue to execute data theft and extortion…
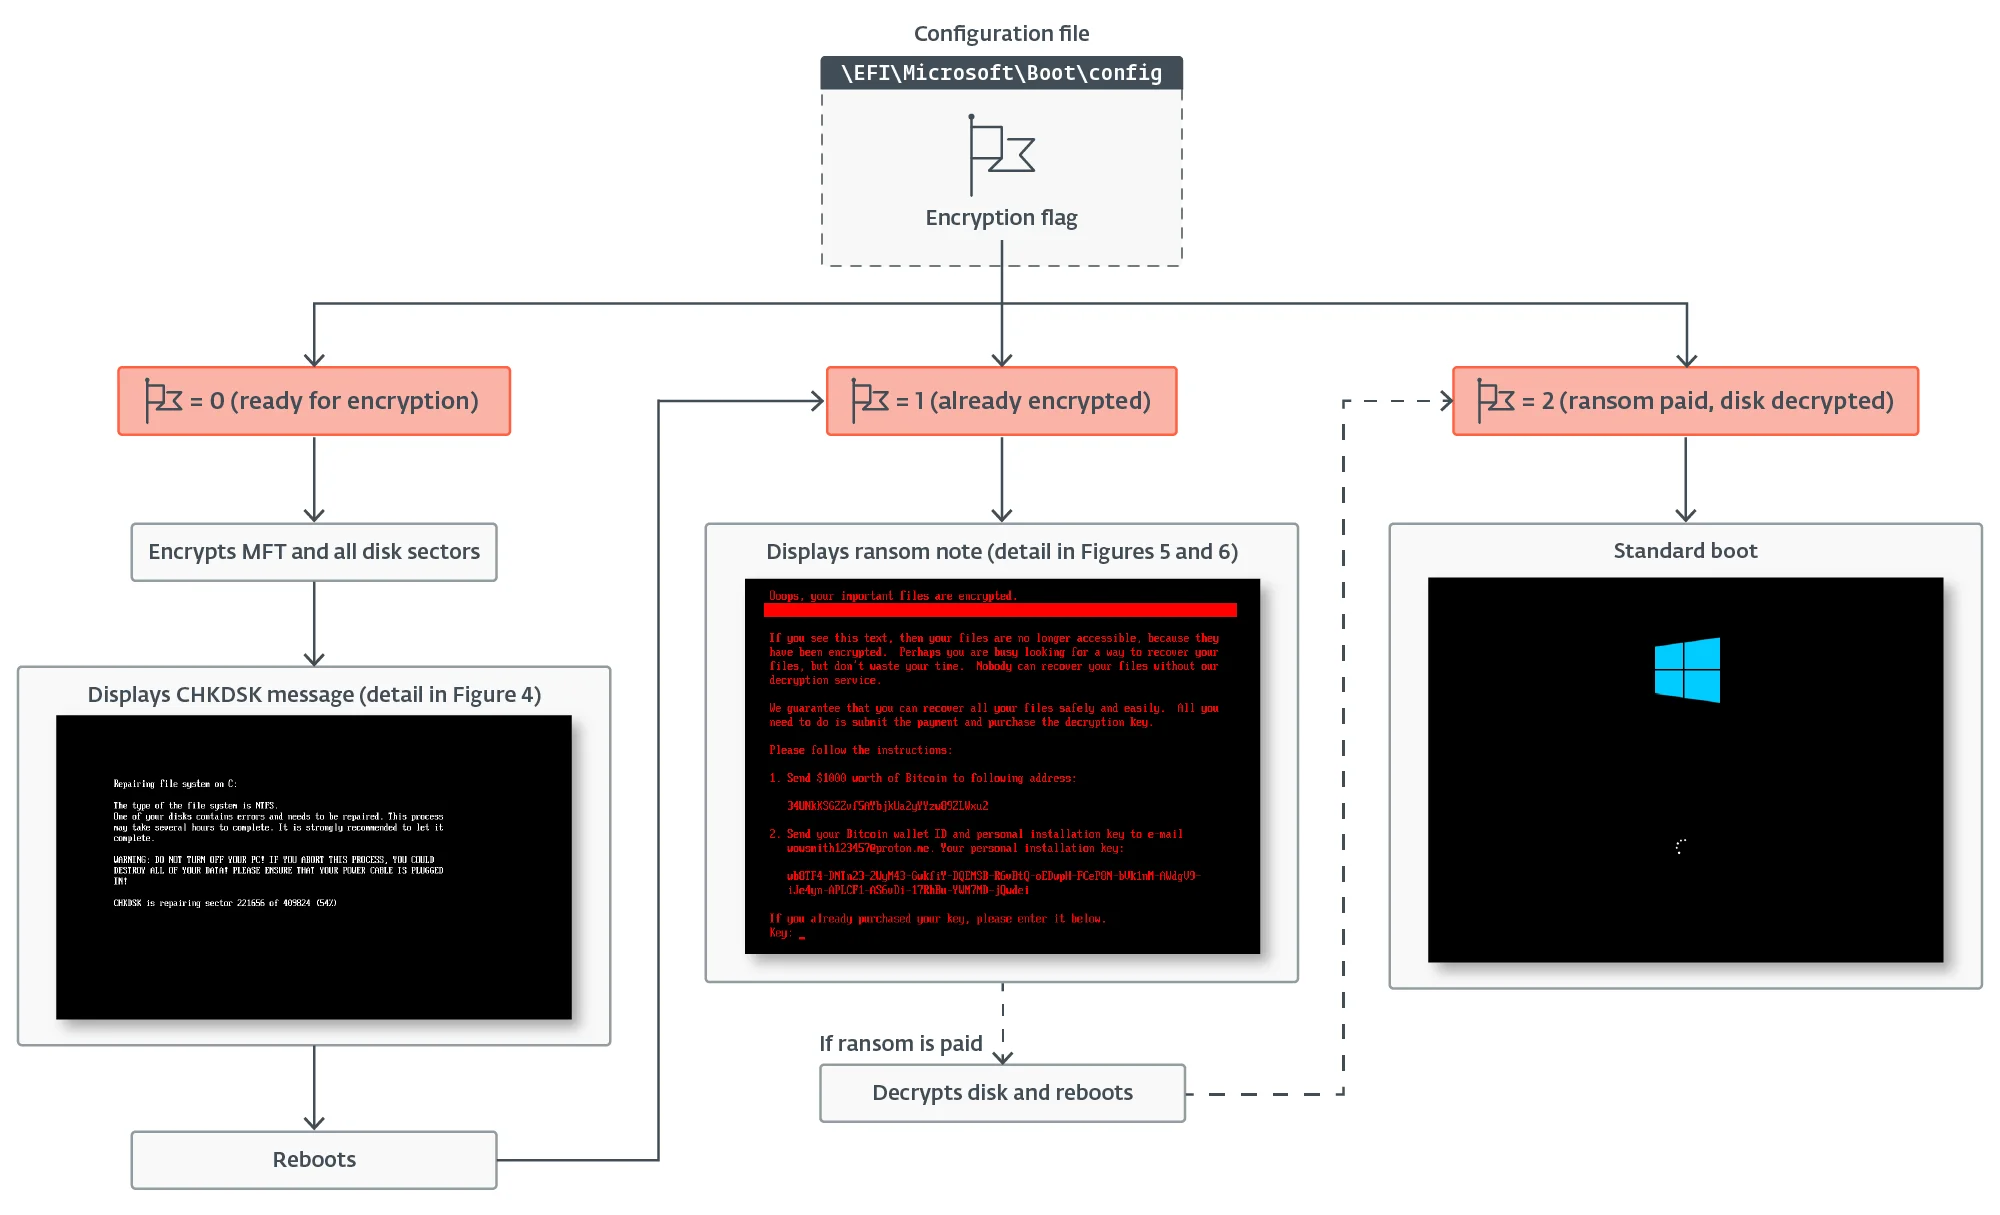
ESET researchers have uncovered HybridPetya, a sophisticated malware that combines bootkit and ransomware capabilities with UEFI system compromise. This malware can bypass UEFI Secure Boot using CVE-2024-7344 and is currently a proof of concept with no active threats observed in the wild. #HybridPetya #CVE20247344…
A sophisticated phishing-as-a-service called VoidProxy targets Google and Microsoft accounts, bypassing traditional MFA defenses using adversary-in-the-middle techniques. This operation captures session tokens and credentials, enabling account takeovers and further malicious activities, highlighting the need for advanced protections like passkeys. #VoidProxy #OktaThreatIntel…
Daily Recap, The latest cybersecurity updates highlight a surge in ransomware like HybridPetya leveraging CVE-2024-7344 to bypass UEFI Secure Boot, plus Akira actively exploiting CVE-2024-40766 in SonicWall SSLVPNs. Also noted are ToneShell anti-analysis tricks and AsyncRAT drops, a Panama Ministry breach, and broader patching efforts across DELMIA Apriso, Cisco IOS XR, Samsung Android, and Adobe AV25-583.
#HybridPetya #CVE-2024-40766 #ToneShell #AsyncRAT #PanamaBreaches #DELMIA #IOSXR #SamsungCVE-2025-21043 #CISAProgram #C2PA
Multiple cybercriminal groups are exploiting a phishing service called VoidProxy to hijack Microsoft and Google accounts by stealing credentials and session tokens in real time. Experts warn that this ongoing campaign affects various industries globally and recommends robust authentication measures like passkeys to prevent such attacks. #VoidProxy #AiTM…