Cybersecurity experts have uncovered a widespread supply chain attack on npm packages, involving at least 187 compromised packages containing self-propagating malware. The campaign, called ‘Shai-Hulud’, targets prominent packages and abuses tools like TruffleHog to exfiltrate secrets and create unauthorized workflows. #ShaiHulud #npmSupplyChainAttack
Category: Cyber Security News
A large-scale Android ad fraud operation named “SlopAds” involved 224 malicious apps on Google Play, generating 2.3 billion ad requests daily. The campaign utilized sophisticated evasion methods like steganography and remote configuration to conceal malicious activities from security tools. #SlopAds #FatModule
Microsoft 365 has introduced Copilot Chat, an AI-powered content-aware chat integrated into Word, Excel, PowerPoint, Outlook, and OneNote for eligible business users. This feature enhances productivity by providing contextual assistance within the apps and offers the option to access broader data with a paid license. #Microsoft365 #CopilotChat

Cybersecurity researchers have identified critical vulnerabilities in Chaos Mesh that could allow attackers to take over Kubernetes clusters. The flaws stem from unauthenticated access to the GraphQL server, enabling remote code execution and malicious fault injections. #ChaosMesh #KubernetesSecurity…
A short-term funding bill aims to extend key cybersecurity laws, including CISA 2015 and the State and Local Cybersecurity Grant Program, until November 21. This extension provides lawmakers more time to decide on longer-term renewal plans amidst ongoing legislative debates. #CybersecurityInformationSharing #ThreatIntelligenceLegislation…
Conor Fitzpatrick, founder of BreachForums, received a new three-year prison sentence after previous release was overturned, due to his extensive cybercriminal activities and involvement in criminal forums. The Department of Justice emphasized the severity of his crimes, including trafficking stolen data and child pornography, and highlighted ongoing efforts to combat cybercrime…
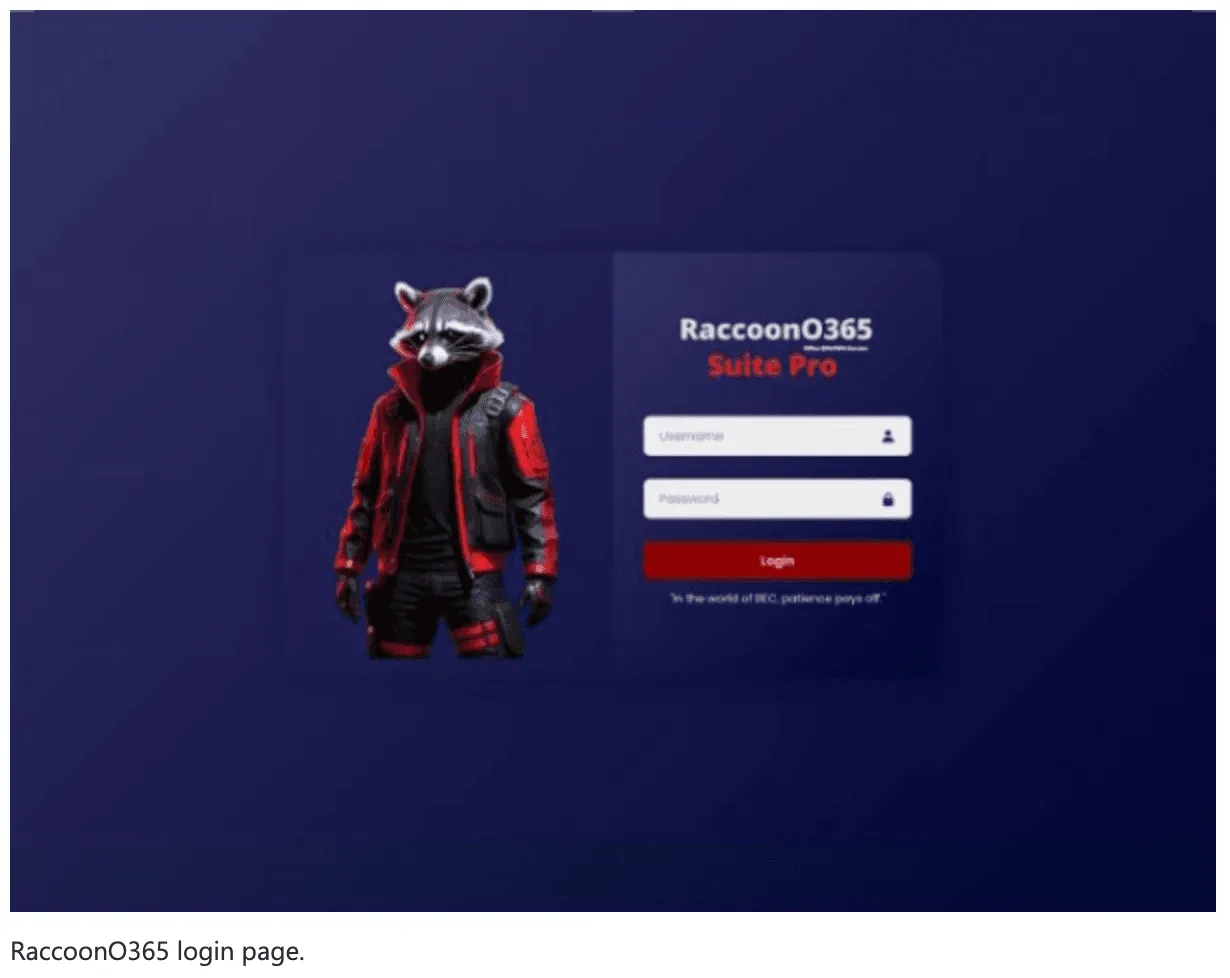
Microsoft has seized 338 websites linked to RaccoonO365, a phishing service used by cybercriminals to steal Microsoft credentials. The operation revealed a sophisticated criminal network behind the tool, which targeted thousands of users globally and employed advanced techniques, including AI-backed services. #RaccoonO365 #JoshuaOgundipe…

Check Point Software Technologies plans to acquire Lakera to enhance its AI security offerings, particularly for Agentic AI applications. This move aligns with industry trends as companies seek to protect generative AI, LLMs, and autonomous systems in enterprise environments. #Lakera #AIsecurity…

A recent supply chain attack targeted nearly 200 NPM packages, including some from CrowdStrike, utilizing a self-propagating worm to infect downstream packages. The incident highlights the evolving sophistication of supply chain threats and emphasizes the need for improved security measures like dependency audits and package verification. #CrowdStrike #ShaiHulud…

Hackers stole the personal data of millions of customers from luxury brands Gucci, Balenciaga, and Alexander McQueen, including names, contacts, and addresses. The breach was carried out by Shiny Hunters, but no financial information was compromised. #ShinyHunters #Kering #LuxuryBrands…

A recent SEO poisoning attack targeted Chinese-speaking Windows users by manipulating search results to direct them to malicious websites. The campaign involved disguised malware in legitimate-looking installers, using SEO techniques and anti-analysis tactics to evade detection and establish persistent infections. #Hiddengh0st #Winos…
A new FileFix social engineering campaign impersonates Meta support to trick users into installing the StealC infostealer malware through multi-layered phishing and steganography techniques. This evolving attack highlights the importance of user awareness and advanced detection measures in cybersecurity. #MetaSupport #StealC #FileFix #SocialEngineering #Infostealer
Apple has released security updates to patch a zero-day vulnerability (CVE-2025-43300) affecting older iPhones and iPads, which was exploited in highly sophisticated targeted attacks. The flaw involves an out-of-bounds write in the Image I/O framework, leading to potential remote code execution; Apple and WhatsApp have warned about ongoing exploitation. #CVE202543300 #ImageIO #targetedattacks #AppleSecurity
Jaguar Land Rover has extended its production shutdown by another week due to a severe cyberattack that disrupted its systems and resulted in data theft. The cybercriminal group “Scattered Lapsus$ Hunters” has claimed responsibility, deploying ransomware and stealing information from the automaker’s network. #Lapsus$ #ShinyHunters

A fully certified VMware team enhances an organization’s security, collaboration, and innovation efforts. Certification improves technical expertise, security practices, and employee retention, making it a strategic investment for modern infrastructure. #VMwareCertification #vSphereSecurity