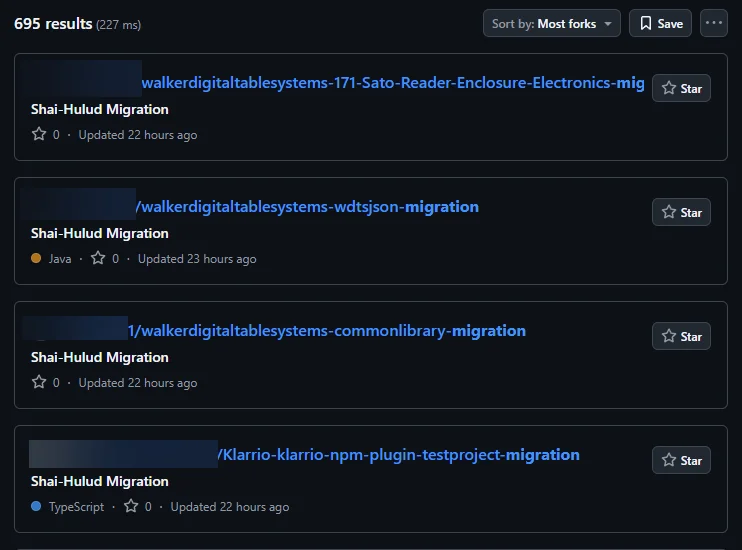
A self-replicating worm called “Shai-hulud” is rapidly infecting npm packages by stealing credentials and exfiltrating sensitive data through compromised GitHub repositories. The attack exploits npm tokens and GitHub access, turning private repositories public and adding malicious workflows, representing a significant supply chain threat. #Shaihulud #npmsecurity #GitHubThreats…
Category: Cyber Security News

Poland is significantly increasing its cybersecurity budget to €1bn to combat frequent Russian cyber-attacks, including targeting critical infrastructure like hospitals and water supplies. The country also faces physical threats such as drone incursions and GPS jamming, highlighting the multifaceted nature of modern hybrid threats. #RussianCyberAttacks #WaterSupplyHack #GPSJamming #PolandDefense…

Jaguar Land Rover has extended its production halt due to a cyber-attack, causing widespread supply chain disruptions and financial impact on suppliers. The incident highlights the vulnerabilities of interconnected manufacturing systems and the ongoing threat of cybercriminal groups targeting operational resilience. #ScatteredSpider #Lapsus$ #JLR…

Quantum computing and AI are transforming technological innovation but also pose significant cybersecurity threats, including the potential to break encryption and enable smarter attacks. Experts warn that organizations must prepare for a surge in quantum and AI-driven cyber threats by building resilient, multi-layered security systems. #QuantumComputing #AIThreats #QuantumSafeCryptography #CyberResilience…

Cybercriminal group TA558, associated with RevengeHotels, has launched sophisticated phishing campaigns targeting the hospitality industry in Latin America using AI-generated scripts and malware. These attacks aim to steal credit card data by delivering Remote Access Trojans like Venom RAT, with evolving tactics to bypass security measures. #RevengeHotels #VenomRAT…

The Jaguar Land Rover cyberattack, attributed to the Scattered Lapsus$ Hunters, has caused extensive production shutdowns, impacting thousands of jobs and supply chains in the UK. The incident underscores the long-lasting damage malware attacks can inflict and the importance of robust cybersecurity measures. #ScatteredLapsus$ #JLR #TataMotors…

Recent threat activity includes a fake AnyDesk installer mimicking ClickFix attacks and utilizing advanced infection strategies involving Cloudflare verification pages and MSI packages. The campaigns also feature the use of the Cephalus ransomware, which employs DLL sideloading to deploy payloads. These evolving tactics highlight the importance of user awareness and advanced detection measures. #MetaStealer #CephalusRansomware
Microsoft has issued reminders that Office 2016 and Office 2019 will end support on October 14, 2025, urging users to upgrade to avoid security and compatibility issues. The company also announced the end of support for Windows 10, Exchange 2016, and Exchange 2019, emphasizing the importance of migrating to newer versions like Microsoft 365 Apps, Office 2024, or Office LTSC 2024. #Office2016 #Office2019 #Windows10 #Exchange2016 #Exchange2019
SonicWall has issued a warning to reset credentials following a security breach that exposed firewall configuration backup files in MySonicWall accounts, impacting less than 5% of their firewall customer base. The incident involved brute force attacks and could allow threat actors to exploit sensitive information, but SonicWall is actively working with authorities and providing guidance to mitigate risks. #SonicWall #CVE-2024-40766
Insight Partners, a major venture capital firm, experienced a data breach involving sophisticated social engineering, leading to the theft and encryption of sensitive data. The incident impacted over 12,000 individuals and highlights the ongoing threat of cybercriminals exploiting trusted organizations. #InsightPartners #SocialEngineering #DataBreach #Ransomware

A China-aligned threat actor, TA415, has conducted spear-phishing campaigns targeting U.S. government, think tanks, and academic organizations related to U.S.-China relations. The group uses sophisticated methods including spoofed emails, obfuscated scripts, and persistent backdoors to gather intelligence amid ongoing trade negotiations. #TA415 #BrassTyphoon…

A major cyberattack on Jaguar Land Rover (JLR) has caused significant disruptions in the UK automotive industry, impacting suppliers and local economies. The incident highlights the vulnerability of industrial sectors to cyber threats and the need for government intervention. #JLRCyberattack #UKAutomotive…

RevengeHotels, a cybercriminal group active since 2015, is using artificial intelligence to enhance its hotel-targeted attacks across multiple countries. They employ AI-generated code and sophisticated phishing tactics to steal sensitive data from hotel guests and staff, reflecting a broader trend of threat actors leveraging AI for more effective cyberattacks. #RevengeHotels #VenomRAT…

A California federal judge dismissed Meta’s appeal against a verdict holding the company liable for illegally collecting health data via the Flo app. The case highlights concerns over data privacy laws and big tech’s handling of sensitive reproductive health information. #Meta #FloApp #CaliforniaInvasionOfPrivacyAct…

RegScale, a provider of GRC solutions, has raised over $30 million in a Series B funding round, bringing its total funding to over $50 million. The company’s CCM platform uses AI to monitor compliance, automate audits, and analyze risks, helping organizations manage cybersecurity and operational risks effectively. #RegScale #CCM #AI #GRC…