
Daily Recap, Cybersecurity News highlights a wave of state and geopolitical activity, including APT28’s Phantom Net targeting Ukraine and TA415’s Silent Spy operations leveraging VS Code remote tunnels, plus AI-driven disinformation tied to Romania and cross-border attacks against India’s infrastructure. The cybercrime section notes high-profile breaches (Tiffany, Insight Partners, Brevard) and evolving tooling (CountLoader, SystemBC) alongside AI-enabled phishing and credential theft on cloud platforms, with notable incidents like Scattered Spider and JLR, and regulatory actions shaping the risk landscape. #PhantomNet #SilentSpy #RomaniaInfluence #IndiaAttacks #AfghanistanNetban #PolandResponse #ScatteredTeens #JLRAttack #CountLoader #SystemBC #RevengeHotels #SonicWallNotice #ShadowLeak #AICrypto #ShinyHunters #GhostActionTokens #Shai-hulud #SilentSync #GlassAction
Category: Cyber Security News

SonicWall has confirmed a breach exposing customer firewall configuration files on its MySonicWall.com platform, raising concerns about systemic security issues. The attack involved brute force tactics targeting stored backup files, potentially putting customer networks at risk. #SonicWall #FirewallBreach…

A new malware called Raven Stealer has been identified as a stealthy tool for stealing personal data through browsers and sending it via Telegram. It employs advanced techniques like process hollowing to evade detection, highlighting the evolving nature of cyber threats. #RavenStealer #Lat61Threat #PointWild…

A data breach at New York Blood Center Enterprises affected nearly 194,000 individuals, exposing personal, health, and banking information in January 2025. The organization is offering free credit monitoring and investigating the breach while remaining operational. #NYBloodCenter #DataBreach #RansomwareAttacks #HealthcareSecurity…

A new vulnerability in Microsoft’s Entra ID (CVE-2025-55241) poses a significant risk of complete tenant takeovers by exploiting architectural gaps. Organizations should apply patches, audit legacy apps, and migrate to Microsoft Graph to mitigate these threats. #CVE-2025-55241 #EntraID #AzureAdGraphAPI…
ShadowLeak demonstrates how prompt injections can exploit LLMs through malicious content embedded in emails or documents. Despite mitigations, attackers can still exfiltrate sensitive data by exploiting workflows and AI features. #ShadowLeak #PromptInjection…

CISA revealed details of malware used in attacks exploiting vulnerabilities in Ivanti Endpoint Manager Mobile, leading to unauthorized remote code execution. The threat actors used malicious loaders to maintain persistence, extract data, and manipulate server functions. #IvantiEPMM #CVE20254427 #CVE20254428 #MaliciousLoaders #RemoteCodeExecution…

Two teenagers from the UK were arrested for their involvement with the Scattered Spider hacking group, linked to the August 2024 cyber attack on Transport for London. The group has also targeted U.S. healthcare organizations, causing extensive financial losses and disruption. #ScatteredSpider #TfLAttack…
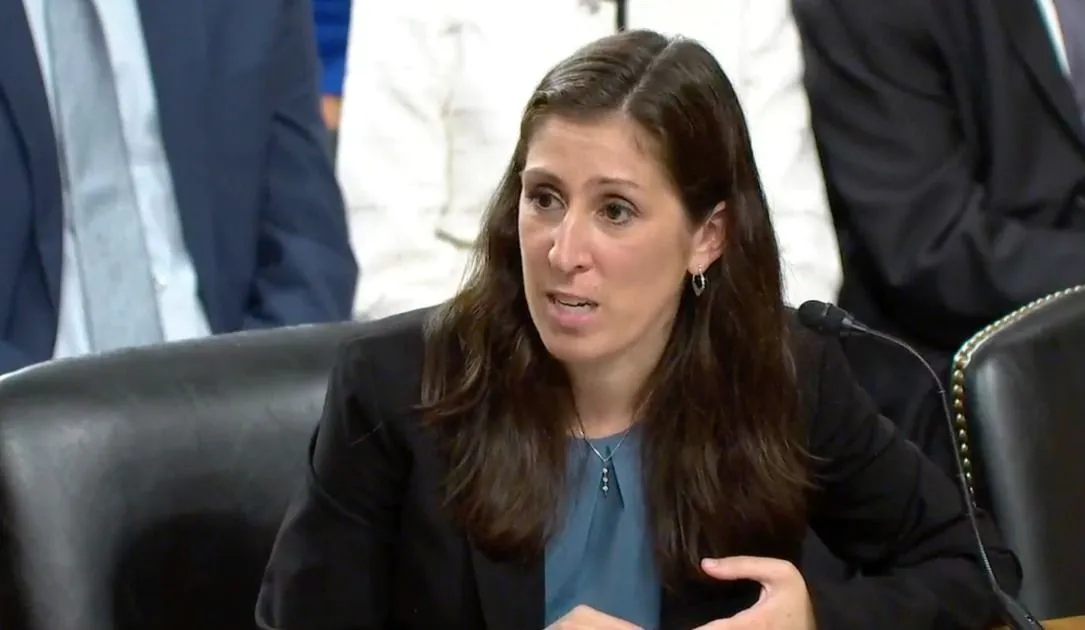
Katherine Sutton has been confirmed as the U.S. Defense Department’s cyber policy chief, becoming only the second person to hold this position. Her appointment comes amid recent leadership vacancies and ongoing concerns about strengthening the Pentagon’s cyber capabilities against China and other digital adversaries. #CyberPolicy #PentagonLeadership…

OpenAI has patched a vulnerability called “ShadowLeak” that could allow attackers to steal sensitive information via ChatGPT’s Deep Research agent. The exploit involved sending malicious emails that enabled covert data exfiltration without user interaction. #OpenAI #DeepResearch #ShadowLeak #Vulnerability #Cyberattack…
MuddyWater, an Iranian state-sponsored APT, has shifted from broad RMM-based intrusions to more targeted attacks using custom malware and spearphishing. Their evolving tactics and infrastructure, including cloud hosting platforms, make them a persistent threat to international critical sectors. #MuddyWater #IranianApt…
Novakon’s industrial control systems, specifically their HMIs, are affected by critical vulnerabilities that could allow remote code execution without authentication. The vendor has not yet released patches or responded to security concerns, raising fears of potential exploitation in critical infrastructure settings. #Novakon #CyberDanube…

Qilin remains the leading ransomware group in August, but emerging competitors like Sinobi, The Gentlemen, and the reemergence of LockBit pose new threats to the ransomware landscape. The rise of supply chain attacks and the dominance of U.S. targets highlight evolving risks for cybersecurity defenses. #Qilin #Sinobi #LockBit #TheGentlemen…

CISA’s Malware Analysis Report reveals a new hacking campaign exploiting Ivanti Endpoint Manager Mobile (EPMM) vulnerabilities CVE-2025-4427 and CVE-2025-4428. The threat actors deployed custom malware for persistent access, targeting specific software versions and using innovative delivery methods. #CISA #IvantiEPMM #CVE20254427 #CVE20254428…

A Russian regional carrier, KrasAvia, experienced a digital service disruption that resembled a cyberattack, similar to the incident involving Aeroflot. Cyberattacks on Russia’s aviation sector have increased since the Ukraine conflict, with groups like Silent Crow and Cyber Partisans involved. #SilentCrow #Aeroflot…