A ransomware attack on Collins Aerospace disrupted check-in systems at major European airports, causing delays and cancellations. The threat actor remains unidentified, but manual procedures helped mitigate some impacts; the incident highlights ongoing cyber risks in the aviation sector. #CollinsAerospace #RTX #ScatteredSpider…
Category: Cyber Security News
A ransomware attack disrupted Collins Aerospace systems, impacting major European airports and causing flight delays and cancellations. The attack may be linked to cybercrime groups like ShinyHunters or Scattered Spider, with ongoing investigations by law enforcement. #CollinsAerospace #ShinyHunters #ScatteredSpider #ENISA…
Academic researchers demonstrate that CPU vulnerabilities like L1TF and half-Spectre can be exploited together to leak sensitive data from virtual machines in public cloud environments. The findings highlight the need for improved mitigation strategies to protect cloud infrastructure from transient execution attacks. #L1TF #Foreshadow #Spectre #CloudSecurity #IntelVulnerabilities…

Mycroft is a Toronto-based company that has launched an AI-driven security platform to help organizations manage their cybersecurity and IT operations efficiently. The platform provides enterprise-grade security and compliance features for startups and SMBs, supported by recent seed funding. #Mycroft #AI Security Platform…

A critical vulnerability (CVE-2025-55241) in Microsoft Entra ID allows attackers to impersonate Global Administrators across multiple tenants using invisible Actor tokens and a flaw in the Azure AD Graph API. This exploit can access sensitive data and tenant configurations without detection, highlighting significant security risks. #CVE202555241 #MicrosoftEntraID…

A critical vulnerability in Microsoft Entra ID (CVE-2025-55241) could allow attackers to impersonate any user, including Global Admins, across tenants, leading to potential full tenant compromise. Microsoft addressed this flaw in July 2025, but the issue highlights significant risks associated with legacy APIs and cross-tenant access abuse. #CVE-2025-55241 #MicrosoftEntraID #AzureAdGraphAPI…

A recent report highlights how CopyCop, a Russian influence network, is rapidly expanding its disinformation efforts using large language models and fake media sites across numerous countries. The organization aims to undermine support for Ukraine and destabilize Western democracies through AI-generated propaganda and fabricated content. #CopyCop #Storm1516 #Deepfakes #Llama3 #Disinformation…
Fortra has issued patches for a critical vulnerability in their GoAnywhere MFT software that could allow attackers to execute remote commands. Despite no evidence of active exploitation, the flaw poses a significant threat to exposed systems, especially given the history of previous exploits against Fortra products. #CVE202510035 #GoAnywhereMFT…

Major European airports including Berlin, Brussels, Dublin, and London faced significant cyberattacks disrupting check-in systems and causing widespread flight delays and cancellations. The attacks targeted Collins Aerospace’s Muse software, highlighting the increasing cyber threats to critical aviation infrastructure. #CollinsAerospace #MuseSoftware…

Cybersecurity Threat Research ‘Weekly’ Recap. The report highlights a week of widespread vulnerability disclosures, supply-chain attacks, and ransomware trends, including a self-replicating npm worm (Shai-Hulud) and numerous loader, adware, and credential-stealing campaigns that span multiple platforms from Windows to macOS and mobile. It also covers APT/state-aligned operations, targeted phishing, and defensive tooling to enhance detection and response.
#Shai-Hulud #SystemBC #ChillyHell #Oyster #Kawa4096 #BlackLock #Qilin #Kimsuky #TA415 #TA415 WhirlCoil
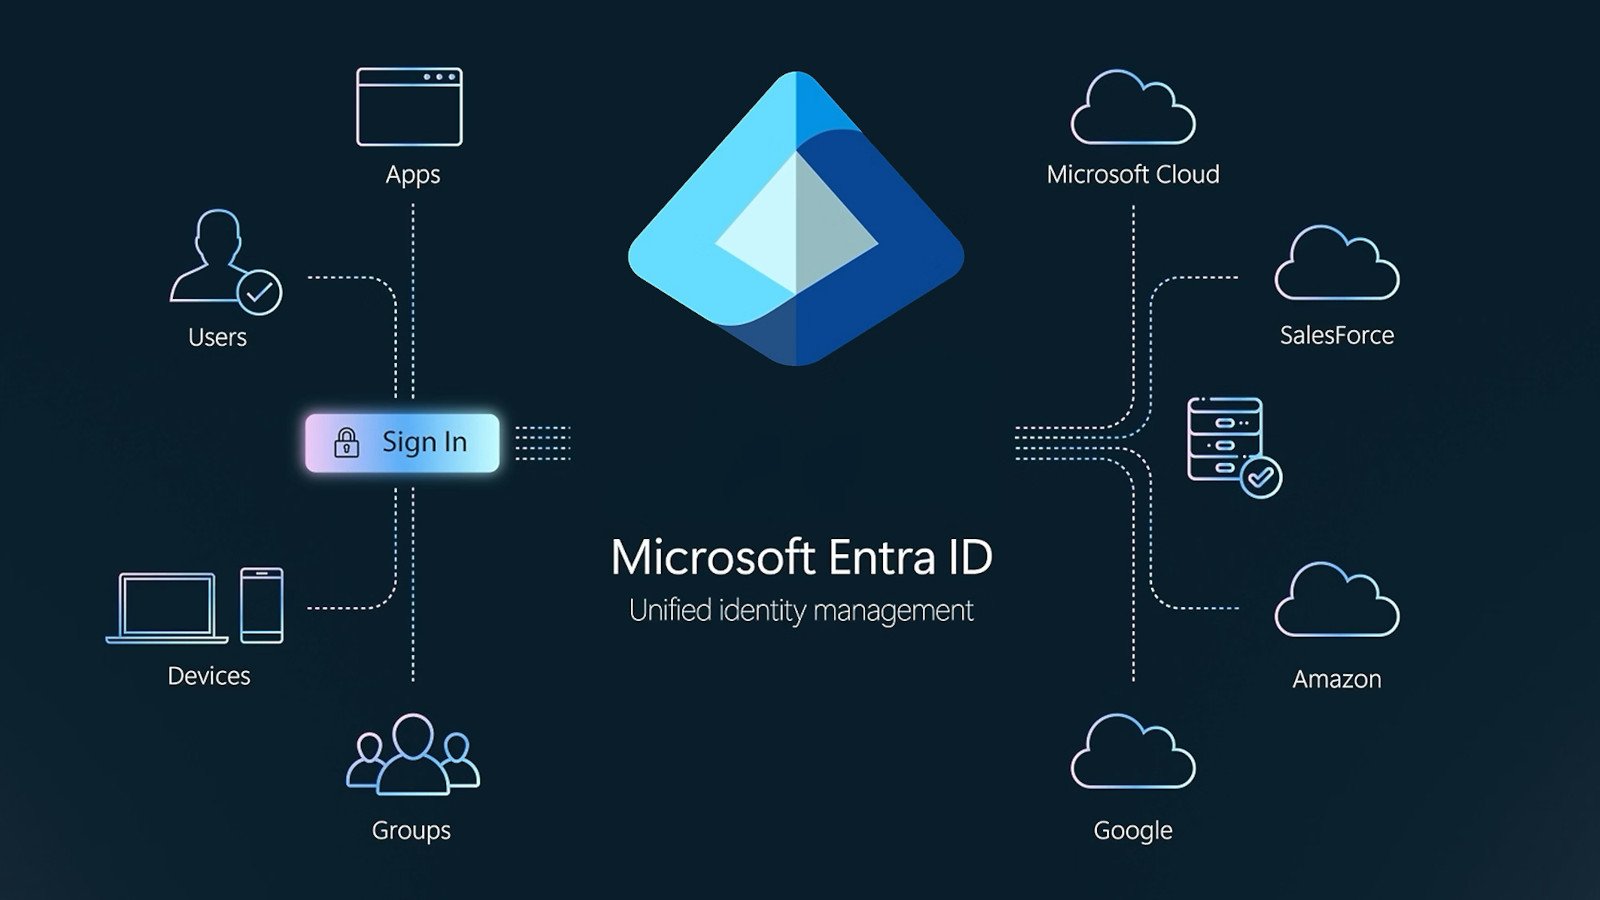
A critical security flaw involving legacy actor tokens and a vulnerability in Azure AD Graph API could have allowed worldwide access to Microsoft Entra ID tenants. Security researcher Dirk-jan Mollema discovered these issues, leading to a resolved privilege escalation vulnerability. #AzureADGraph #ActorTokens
A cyberattack targeted check-in and boarding systems at several major European airports, causing operational disruptions and delays. Experts believe the attack exploited vulnerabilities in third-party systems, raising concerns about industry-wide security risks. #CollinsAerospace #EuropeanAirports…
A cyberattack on Collins Aerospace’s airport check-in systems caused widespread flight disruptions across several European airports, especially Brussels Airport. Despite ongoing issues, airports and airlines are employing manual and backup systems to mitigate the impact. #CollinsAerospace #EuropeanAirports…

North Korean threat actors are using ClickFix-style social engineering to deliver malware like BeaverTail and InvisibleFerret, targeting marketing and trading roles in cryptocurrency and retail sectors. These campaigns are evolving with the use of compiled binaries and fake job platforms, reflecting operational adaptation by Lazarus subgroup. #NorthKoreanThreats #Lazarus #BeaverTail #InvisibleFerret…

Daily Recap, Researchers expose MalTerminal and ShadowLeak, highlighting growing LLM abuse and zero-click data exfiltration risks in AI-enabled threats. The report covers state-backed operations, ransomware trends, and notable breaches involving Jaguar Land Rover, ShinyHunters, and MrBeast, underscoring the widening attack surface across AI, OT, and consumer ecosystems. #MalTerminal #ShadowLeak #Turla #Gamaredon #UNC1549 #Lapsus$Hunters #JaguarLandRover #ShinyHunters #MrBeast