European law enforcement has arrested suspects linked to a crypto investment fraud ring that defrauded over €100 million from more than 100 victims. The operation revealed a multi-year scam offering fake high returns, with proceeds funnelled through bank accounts in Lithuania and victims coerced to pay additional fees to recover their assets. #CryptoFraud #Eurojust #Europol
Category: Cyber Security News

Cybersecurity researchers have uncovered the ShadowV2 botnet, a sophisticated DDoS platform that employs containerization and an extensive API for attack management. The campaign demonstrates the evolving landscape of cybercrime-as-a-service, utilizing advanced techniques to bypass defenses like Cloudflare UAM. #ShadowV2 #Docker #DDoSForHire…

Large organizations are reducing their workforce to improve efficiency, but this trend has heightened cybersecurity risks, especially around hardcoded secrets. As security teams shrink, the latest research shows that breaches involving stolen credentials are more costly and harder to contain, emphasizing the need for strategic, precise remediation tools. #HardcodedSecrets #CredentialBreaches…

SolarWinds has released patches for a critical security flaw in Web Help Desk software, which could allow remote code execution without authentication. The vulnerability, CVE-2025-26399, is related to deserialization issues in the AjaxProxy component and is a patch bypass for previous exploits. #SolarWinds #CVE2025-26399…

Jaguar Land Rover is still offline due to a cyberattack, leading to significant financial losses and supply chain disruptions. The incident highlights the broader economic security risks of cyber threats to major industrial sectors. #JLR #CyberAttack #SupplyChainDisruption…
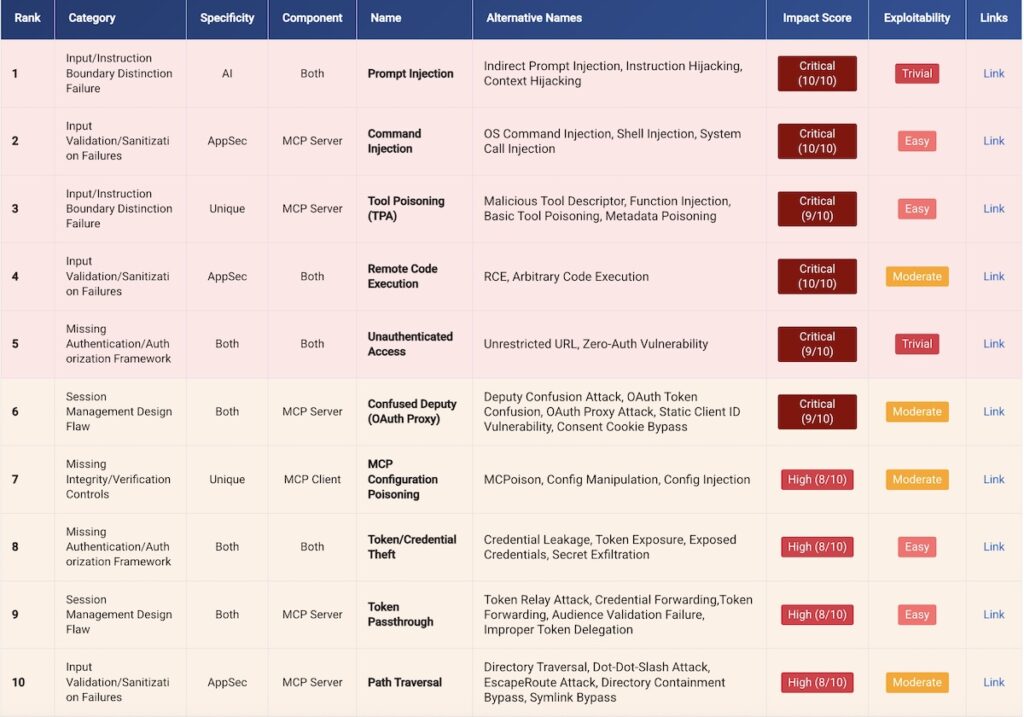
MCP (Model Context Protocol), an open standard by Anthropic, is crucial for safe interaction between AI agents and data sources but has vulnerabilities that could be exploited by malicious actors. Adversa’s comprehensive analysis highlights key security flaws, including prompt injection, and offers mitigation strategies to protect agentic AI systems. #ModelContextProtocol #AgenticAI…
All Microsoft Entra Tenants Were Exposed to Silent Compromise via Invisible Actor Tokens: Researcher
Microsoft quickly addressed a significant Azure Entra privilege escalation vulnerability, showcasing responsible disclosure. However, a deeper vulnerability involving undocumented Actor tokens posed a severe threat to global tenants, highlighting the limits of traditional security measures. #AzureEntra #ActorTokens…

Unit 221B, a threat intelligence firm, has secured $5 million in seed funding to enhance its proprietary platform, eWitness, which tracks cybercriminals and supports law enforcement investigations. The company’s efforts have led to the arrest of cybercriminals, including Ethan Foltz, demonstrating its impact on disrupting cyber threats. #EWitness #CybercriminalArrests…
Stellantis experienced a data breach through a third-party platform used in its North American operations, impacting customer contact information. The automaker assures no sensitive financial data was accessed, and they are advising customers to remain alert to phishing attempts. #ShinyHunters #Salesforce…
A vulnerability in the American Archive of Public Broadcasting’s website allowed unauthorized access to private media files for years, which was only recently patched. The exploit was exploited through an IDOR flaw and circulated among content preservation communities, highlighting risks in digital archives and online communities. #AAPB #IDOR
A ransomware attack on Collins Aerospace’s systems caused major disruptions at several European airports, including Heathrow, Brussels, and Berlin. The incident led to hundreds of flight delays and cancellations, prompting collaboration between cybersecurity agencies and law enforcement. #CollinsAerospace #EUcyberattack
This article highlights a cross-site scripting (XSS) vulnerability in certain versions of Lectora e-learning software, affecting both desktop and online platforms. Users are advised to update and republish courses to mitigate security risks. #LectoraDesktop #LectoraOnline #CrossSiteScripting…

A hacking group called ComicForm has been conducting targeted phishing campaigns against organizations in Belarus, Kazakhstan, and Russia since April 2025, mainly focusing on industrial and financial sectors. The attackers use sophisticated malware delivery mechanisms, including obfuscated loaders and credential harvesting phishing sites, with signs of broader international targeting. #ComicForm #Formbook…

Stellantis reported a data breach caused by unauthorized access to a third-party platform, exposing customer contact information but no sensitive or financial data. The incident aligns with a broader cyberattack affecting Jaguar Land Rover’s manufacturing operations. #Stellantis #JaguarLandRover #cyberattack #dataexposure…

Russia is increasing disinformation and influence operations aiming to sway Moldova’s upcoming parliamentary elections and hinder its integration with the West. These efforts include fake news networks, propaganda campaigns, and credible leaks planning to weaken President Maia Sandu’s government. #Ilanshor #DisinformationCampaigns…