
A new self-propagating malware called SORVEPOTEL targets Brazilian users by exploiting WhatsApp to spread rapidly across Windows systems. The campaign focuses on speed and propagation rather than data theft or ransomware, mainly affecting government and enterprise sectors. #SORVEPOTEL #WhatsAppMalware…
Category: Cyber Security News

LinkedIn has filed a lawsuit against ProAPIs for operating a massive network of fake accounts to scrape and sell user data without permission. The case highlights the growing issue of data scraping and privacy breaches facilitated by scale and automation. #ProAPIs #DataScraping…

Flock Safety is launching Raven, a new gunshot and human voice detection system that raises concerns over privacy and civil liberties. The company’s expanding surveillance technology, used by police and private entities, faces ongoing legal and public scrutiny. #FlockSafety #Raven #SurveillanceControversy #CivilLiberties…
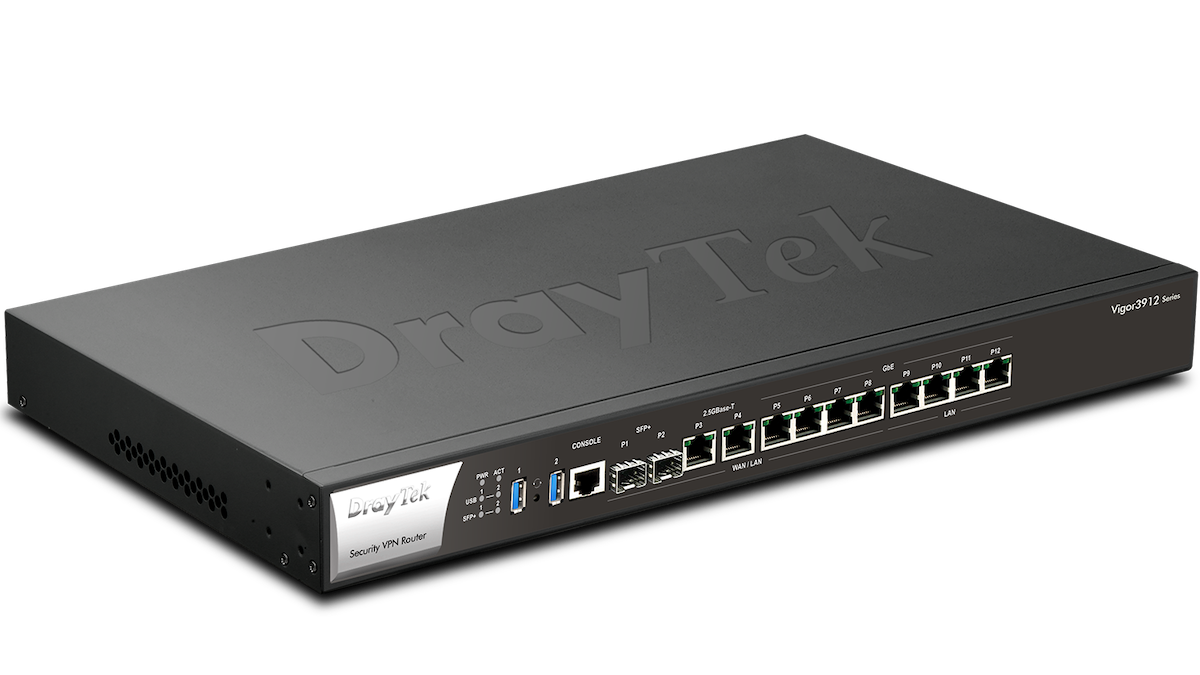
DrayTek has released firmware updates to fix a critical remote code execution vulnerability in DrayOS routers, tracked as CVE-2025-10547. Although no active exploitation has been reported, the flaw could allow attackers to execute arbitrary code remotely through crafted web requests, posing a threat to SMBs and prosumer users. #DrayOS #CVE-2025-10547…

Cybersecurity startup Oneleet secures $33 million in Series A funding to expand its integrated security platform. Their solution streamlines attack surface management, code scanning, and compliance automation to improve organizational security posture. #Oneleet #CybersecurityFunding…
This cybersecurity roundup covers recent updates from Microsoft, new espionage tactics, and data breaches affecting government agencies and private companies. It highlights emerging threats, innovative defense tools, and measures users can take to protect their digital assets. #MicrosoftSentinel #CitrixBleed…

Splunk has revealed six critical security vulnerabilities affecting multiple versions of Splunk Enterprise and Splunk Cloud Platform, mainly involving JavaScript execution, SSRF, and server-side issues. Immediate upgrades and certain mitigation steps are recommended to protect against potential exploitation. #SplunkVulnerabilities #XSS #SSRF…

A cyberattack on Shamir Medical Center exposed sensitive patient email data but did not compromise its core medical record system. The Russian-speaking group Qilin claims responsibility, demanding ransom and threatening to release stolen data. #Qilin #ShamirMedicalCenter #IsraeliHospitals #Cyberattack…

The U.S. CISA has added a critical command injection vulnerability, CVE-2025-4008, in Smartbedded Meteobridge devices to its KEV list due to active exploitation. The flaw allows remote attackers to execute arbitrary code without authentication, risking device control and data breaches. #Smartbedded #CVE-2025-4008…

A threat actor linked to groups like YoroTrooper and Tomiris is targeting Russian and Central Asian entities with malware such as FoalShell and StallionRAT. This group, known as Cavalry Werewolf, uses sophisticated phishing campaigns and remote access tools to infiltrate government and industrial organizations. #YoroTrooper #Tomiris #FoalShell #StallionRAT…
Oracle investigates extortion emails sent to its E-Business Suite customers, potentially linked to known vulnerabilities and cybercrime groups Cl0p and FIN11. While the hackers’ claims of sensitive data theft are unconfirmed, the incident highlights the ongoing exploitation of Oracle vulnerabilities by cybercriminals. #Cl0p #FIN11 #OracleVulnerabilities…
French startup MokN has secured €2.6 million to expand its deception-based identity protection technology that uses honeypots to trap cyber threat actors. The company’s innovative approach helps recover stolen credentials before they are exploited or sold on the dark web. #MokN #Honeypots #CyberDefense #DarkWebThreats…
The US CISA has issued a warning that a vulnerability in Meteobridge devices, specifically CVE-2025-4008, has been exploited in attacks. This flaw involves an unauthenticated command injection via a public CGI script, impacting roughly 100 exposed devices. #CISA #Meteobridge #CVE-2025-4008…

Cybersecurity Awareness Month 2025 emphasizes building a cyber safe culture, focusing on the importance of strong passwords amidst advancing AI threats. While passwords remain a vital first line of defense, adopting password managers and strong password habits is crucial for digital safety. #CybersecurityAwarenessMonth #Passwords #AIThreats…

The cyberattack on Japan’s largest brewery, Asahi Group Holdings, has halted production and disrupted the supply chain of its flagship beer, Asahi Super Dry. The incident, suspected to be a ransomware attack, has caused a looming shortage of the popular beverage across retailers, restaurants, and e-commerce platforms. #AsahiGroup #Ransomware #Cyberattack…