
Two teenagers have been arrested in connection with a cyberattack on Kido nursery chain, which involved the theft and release of sensitive data of around 8,000 children. The hackers, identified as Radiant, demanded ransom and published children’s profiles, raising serious concerns about digital extortion and minors’ privacy. #Radiant #KidoNurseries…
Category: Cyber Security News

India is experiencing a surge in cybercrime incidents amidst extensive internet connectivity, with the government implementing various legal, technological, and awareness initiatives to combat cyber threats. The country is also actively enhancing national cybersecurity infrastructure and fostering international collaboration to secure its digital landscape. #IndiaCybersecurity #CyberFraud #NCRP #CERTIn #OnlineGamingBan…
A hacktivist group called TwoNet shifted from launching DDoS attacks to targeting critical infrastructure, including a fake water treatment facility used as a honeypot. Their activities reveal an evolving threat landscape where cybercriminals engage in both hacktivism and operational technology (OT) attacks. #TwoNet #CVE2021-26829
Microsoft is working to resolve a significant outage affecting its Azure Front Door CDN, causing disruptions in Microsoft 365 services across multiple regions. The company has restored 98% of the affected services and is actively monitoring the situation. #AzureFrontDoor #Microsoft365Outage
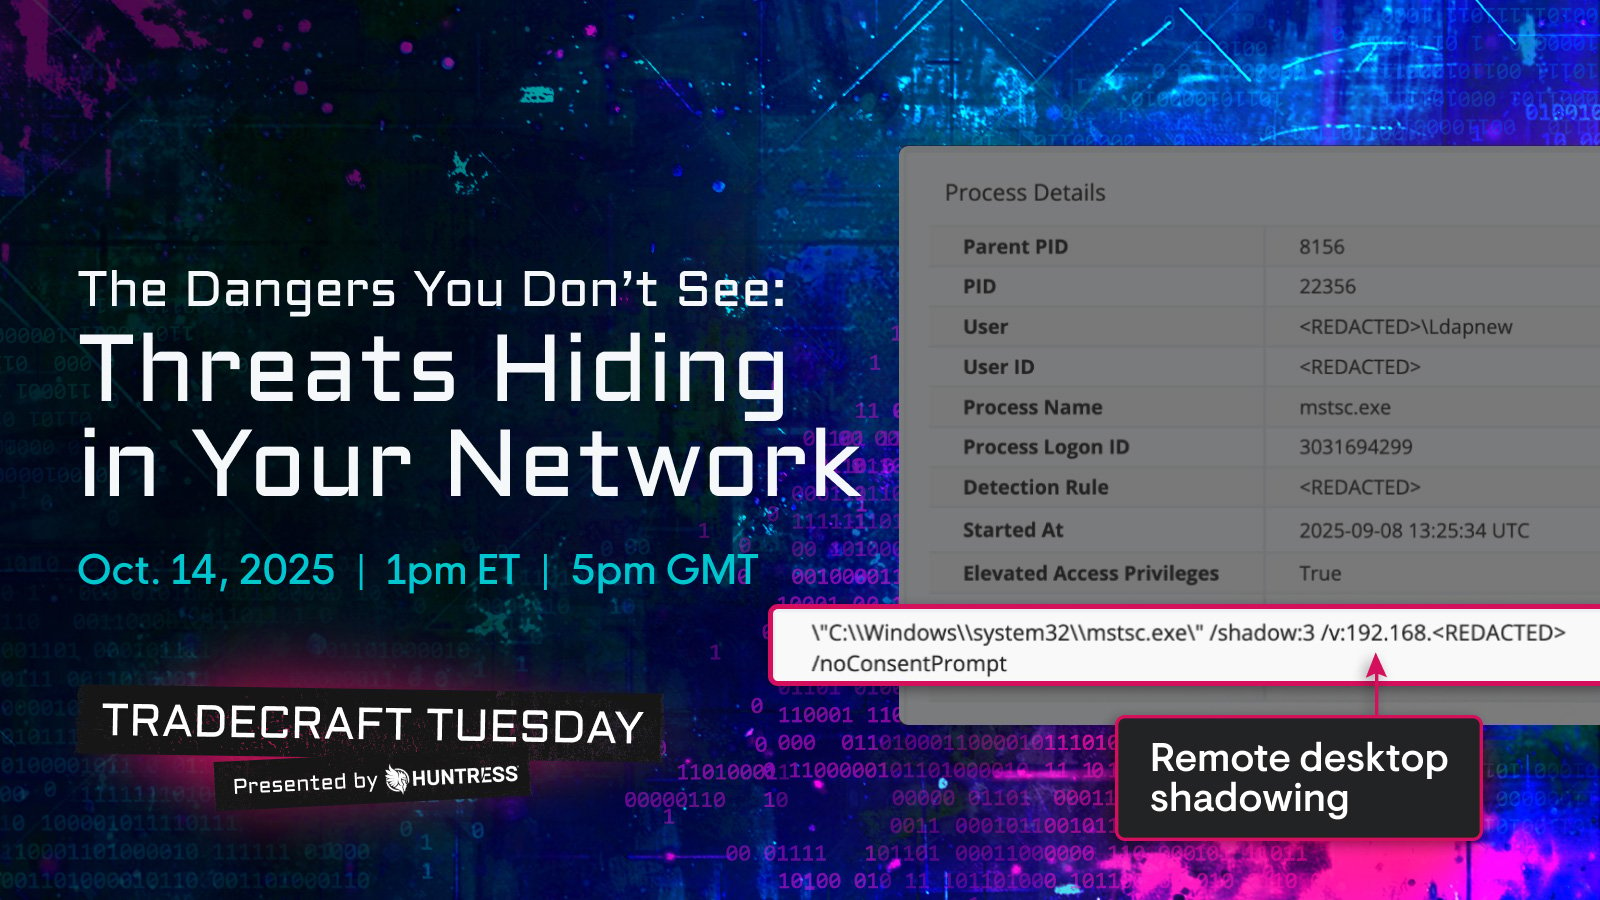
This report details a sophisticated cyberattack chain involving Python loaders, credential theft, and a transition to the PureRAT remote access tool, suggesting a highly organized threat actor. The attack leverages layered obfuscation, process hollowing, and in-memory payloads, emphasizing the need for defense-in-depth strategies. #PureRAT #PXAstealer
SonicWall’s recent security breach compromised the firewall configuration backup files of all customers using their cloud backup service, exposing sensitive data. Customers are urged to reset credentials and monitor their devices, as the investigation confirmed unauthorized access. #SonicWall #MySonicWall #Mandiant

Telstra denies any recent data breach, asserting that the compromised data was scraped from public sources and not from its internal systems. However, threat actors claiming to have access to over 19 million PII records continue to threaten and list Telstra among their victims. #ScatteredSpider #Lapsus$Hunters…

Daily Recap, Google launches an AI Vulnerability Reward Program offering up to $20,000 for critical flaws and DeepMind’s CodeMender auto-detects and patches vulnerable code. Chinese-linked actors abuse Nezha to deploy Gh0stRAT across multiple Asian targets, while BatShadow pushes Vampire Bot via Go-based malware; Salesforce rejects extortion tied to ShinyHunters and Clop exploits Oracle zero-day, with North Korea-linked theft exceeding $2B in crypto this year. #CodeMender #Gh0stRAT #Nezha #VampireBot #ShinyHunters #Clop #NorthKoreanCryptoTheft
Discord reports a significant data breach involving a third-party support platform, exposing millions of users’ personal information, including government IDs and payment details. The company denies responsibility, blaming a compromised outsourced support account, while threat actors demand ransom and threaten public release of stolen data. #Zendesk #BPOSecurity

This webinar discusses the dangers of weak passwords and how traditional policies often fail to protect against cyberattacks. It emphasizes real breach cases and introduces tools like Specops to improve password security effectively. #PasswordBreaches #CredentialAttacks…

Cybersecurity researchers have uncovered a campaign targeting WordPress sites with malicious JavaScript injections leading to site redirection and malware distribution. The campaign uses sophisticated techniques like remote payload loading and cache smuggling to evade detection and deliver malicious content, emphasizing the importance of securing WordPress environments and implementing strong security measures….

Suspected nation-state hackers exploited a zero-day vulnerability to breach the email accounts of a law firm, likely linked to China. The attack is part of a broader campaign targeting the U.S. legal sector for national security and trade information, with investigations ongoing. #ZeroDayAttack #ChinaNexus…
California’s new legislation mandates browsers to implement simple, accessible opt-out mechanisms for third-party data selling, enhancing user privacy rights. This marks the first law of its kind in the U.S., making it easier for millions to control their personal data. #CaliforniaConsumerPrivacyAct #DataPrivacyRights…
AI security posture management (AI-SPM) is an emerging security layer that helps organizations monitor, control, and mitigate risks related to AI systems, especially large language models. It provides transparency, compliance checks, and defenses against threats like prompt injection, data exposure, and shadow AI, ensuring safe AI adoption. #AI-SPM #LLMSecurity…
Crimson Collective is actively targeting AWS cloud environments to exfiltrate data and extort organizations, notably attacking Red Hat and GitLab repositories. Their tactics involve compromising IAM accounts, privilege escalation, and utilizing AWS services for data theft and extortion, highlighting the need for stricter security measures. #CrimsonCollective #AWS #RedHat #GitLab #IAM