
Fortra has investigated and disclosed a critical vulnerability, CVE-2025-10035, in GoAnywhere Managed File Transfer that has been actively exploited since September 2025. Threat actors, including Storm-1175, are using this flaw to deploy ransomware, emphasizing the importance of timely updates and access restrictions. #GoAnywhereMFT #Storm1175 #MedusaRansomware…
Category: Cyber Security News

A pro-Russian hacker group called TwoNet infiltrated a honeypot designed to simulate critical infrastructure systems, illustrating the naivety of inexperienced hacktivists targeting OT and ICS. The incident emphasizes the blurred lines between propaganda and actual cyber operations and highlights ongoing threats to utilities and critical infrastructure. #TwoNet #Honeypot #OTThreats #CriticalInfrastructure…
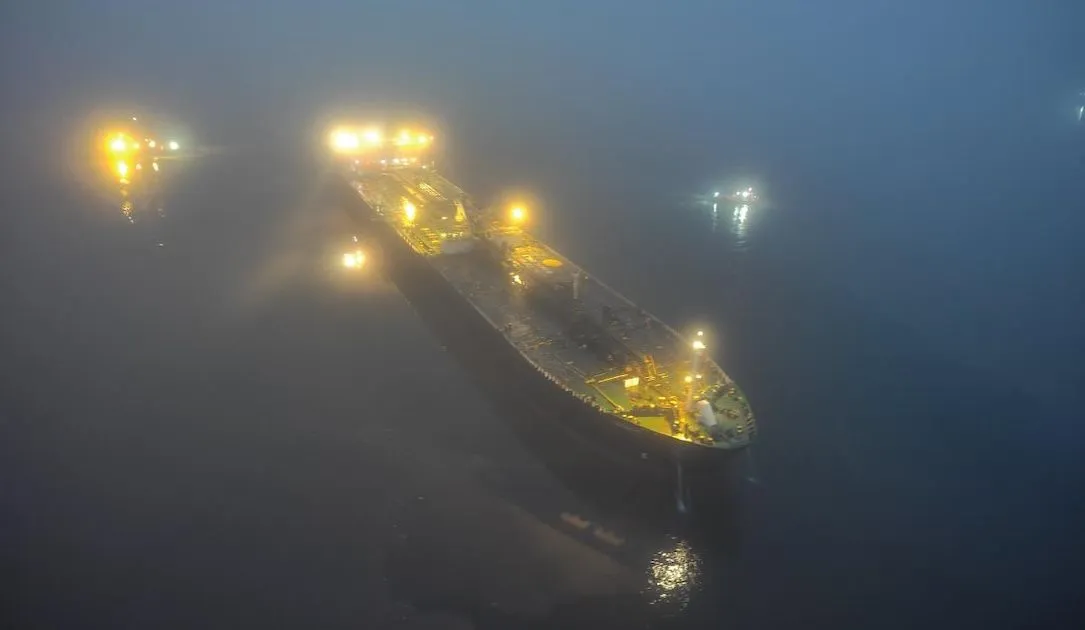
Finland’s court has halted the trial of three officers from the Russian-linked Eagle S oil tanker due to jurisdiction issues related to international waters and maritime laws. The case highlights ongoing challenges in prosecuting sabotage activities by vessels operating under questionable flags amid increasing concerns over Russia’s hybrid warfare tactics. #EagleS…
Juniper Networks has released patches to address nearly 220 vulnerabilities across Junos OS, Junos Space, and Security Director, including nine critical flaws in Junos Space. Users are urged to update promptly as most vulnerabilities have no available workarounds, although none are known to be exploited currently. #JunosSpace #CriticalVulnerabilities…
A new botnet named RondoDox exploits over 50 vulnerabilities across various network devices, including routers, DVRs, and servers, to conduct malicious activities such as DDoS attacks and cryptocurrency mining. Its rapid expansion and use of sophisticated evasion techniques pose a significant threat to organizations with exposed network infrastructure. #RondoDox #Mirai #Morte…
Multiple exploitation campaigns are targeting Cisco, Palo Alto Networks, and Fortinet devices, originating from shared IP subnets. These activities include scanning, brute-force attacks, and exploitation of recent vulnerabilities, indicating coordinated threat actor operations. #CiscoVulnerabilities #PaloAltoGlobalProtect #FortinetVPNattacks…

Microsoft Threat Intelligence reports a series of financial cyberattacks targeting U.S. universities by the threat actor Storm-2657, which exploits weak authentication to hijack payroll systems via phishing and social engineering. The attacks focused on changing payroll details in cloud HR platforms like Workday, emphasizing the need for stronger MFA measures to…

A new proof-of-concept exploit named “fenrir” targets MediaTek-powered devices like the Nothing Phone (2a), allowing attackers to execute arbitrary code by compromising the secure boot process. This vulnerability puts devices at risk of firmware manipulation, unauthorized OS installation, and trust chain breaches. #NothingPhone2a #MediaTekVulnerability…
The FBI and international law enforcement have taken control of the BreachForums domain, disrupting the cybercrime operation run by ShinyHunters. Despite the seizure, the hackers claim their campaign targeting Salesforce remains unaffected, revealing widespread data breaches of major corporations. #ShinyHunters #BreachForums

Several organizations have been targeted by a zero-day exploit in Oracle’s E-Business Suite (EBS) software, leading to data theft and extortion. The attack, associated with the Cl0p ransomware crew, involved multiple vulnerabilities and sophisticated malware payloads. #CVE-2025-61882 #Cl0p #OracleEBS #ZeroDayExploit…
Google Threat Intelligence Group and Mandiant have uncovered an Oracle E-Business Suite extortion campaign involving sophisticated malware and exploited vulnerabilities, including a zero-day flaw CVE-2025-61882. The hackers likely associated with FIN11 have targeted multiple organizations, stealing data and demanding ransom, while exploiting known and unknown vulnerabilities. #CVE-2025-61882 #FIN11 #OracleEBS #GoldVeinJava…

The Protecting America from Cyber Threats Act aims to renew critical cybersecurity protections that expired, fostering ongoing threat information sharing between private sectors and the federal government. This legislation builds on a decade-old framework credited with preventing major cyber incidents like SolarWinds and Volt Typhoon, while also addressing liability concerns for…

Daily Recap, A wave of breaches and extortion efforts hit third-party platforms, Telstra, SonicWall, and major organizations, alongside notable malware and phishing campaigns, while AI security funding and policy updates shape the threat landscape. The incidents span data leaks, zero-days, and credential abuse, with activity from groups like Qilin and Crimson Collective, and evolving attack techniques such as PureRAT chains and WordPress-driven ClickFix phishing.
#DiscordBreach #Telstra #SonicWall #QilinRansomware #CrimsonCollective #TwoNet #WordPress #AI Vulnerability
Threat actors are leveraging the Velociraptor DFIR tool to deploy LockBit and Babuk ransomware, with suspected ties to Chinese nation-state actors named Storm-2603. This campaign demonstrates sophisticated tactics including privileged escalation, persistent access, and data exfiltration targeted at various systems. #Velociraptor #Storm2603
A cybercrime group known as Storm-2657 has been targeting university staff in the US through sophisticated phishing and payroll hijacking attacks since March 2025. The attackers exploit weaknesses like the lack of MFA and use social engineering to compromise accounts and redirect salary payments. #Storm-2657 #Workday #BEC