
Kearney Public Schools experienced a significant cybersecurity breach, disrupting their entire digital network and affecting communication tools. Despite the technical challenges, classes will continue as scheduled, emphasizing ongoing recovery efforts and cybersecurity concerns in education sectors. #KearneyPublicSchools #Cyberattack #EducationSecurity…
Category: Cyber Security News

Qantas Airways confirmed that personal data of 5.7 million customers was stolen in a cyberattack and has taken legal action to prevent further data spread. The airline has strengthened security measures and advised customers to stay vigilant against scams. #Qantas #Cyberattack #IdentityProtection…

Forescout Research has uncovered a new tactic by pro-Russian hacktivists, fabricating industrial attacks to boost their reputation, exemplified by the group TwoNet’s false claims of targeting critical water treatment systems. This escalation from web defacement and DDoS to actual OT/ICS interference signifies an increasing cyber-physical threat. #TwoNet #OTIntrusions…

Cybersecurity Threat Research ‘Weekly’ Recap. The report highlights ongoing package-manager abuse, covert C2 channels, and extortion trends, including malicious npm packages, Discord-based C2, and double-extortion operations. It also covers high-severity vulnerabilities being actively exploited, phishing advancements, information-stealing and MaaS developments, and the rise of malware-less database ransomware, with emphasis on detection challenges and CTI considerations.
#Discord #SonicWall #CVEs #Qilin #RansomHub #Storm-2657 #ChaosBot #LummaStealer #GhostSocks #CastleRAT #XWorm #WhatsAppWorm #ClayRat #CryptoScam #DatabaseRansomware #NVD
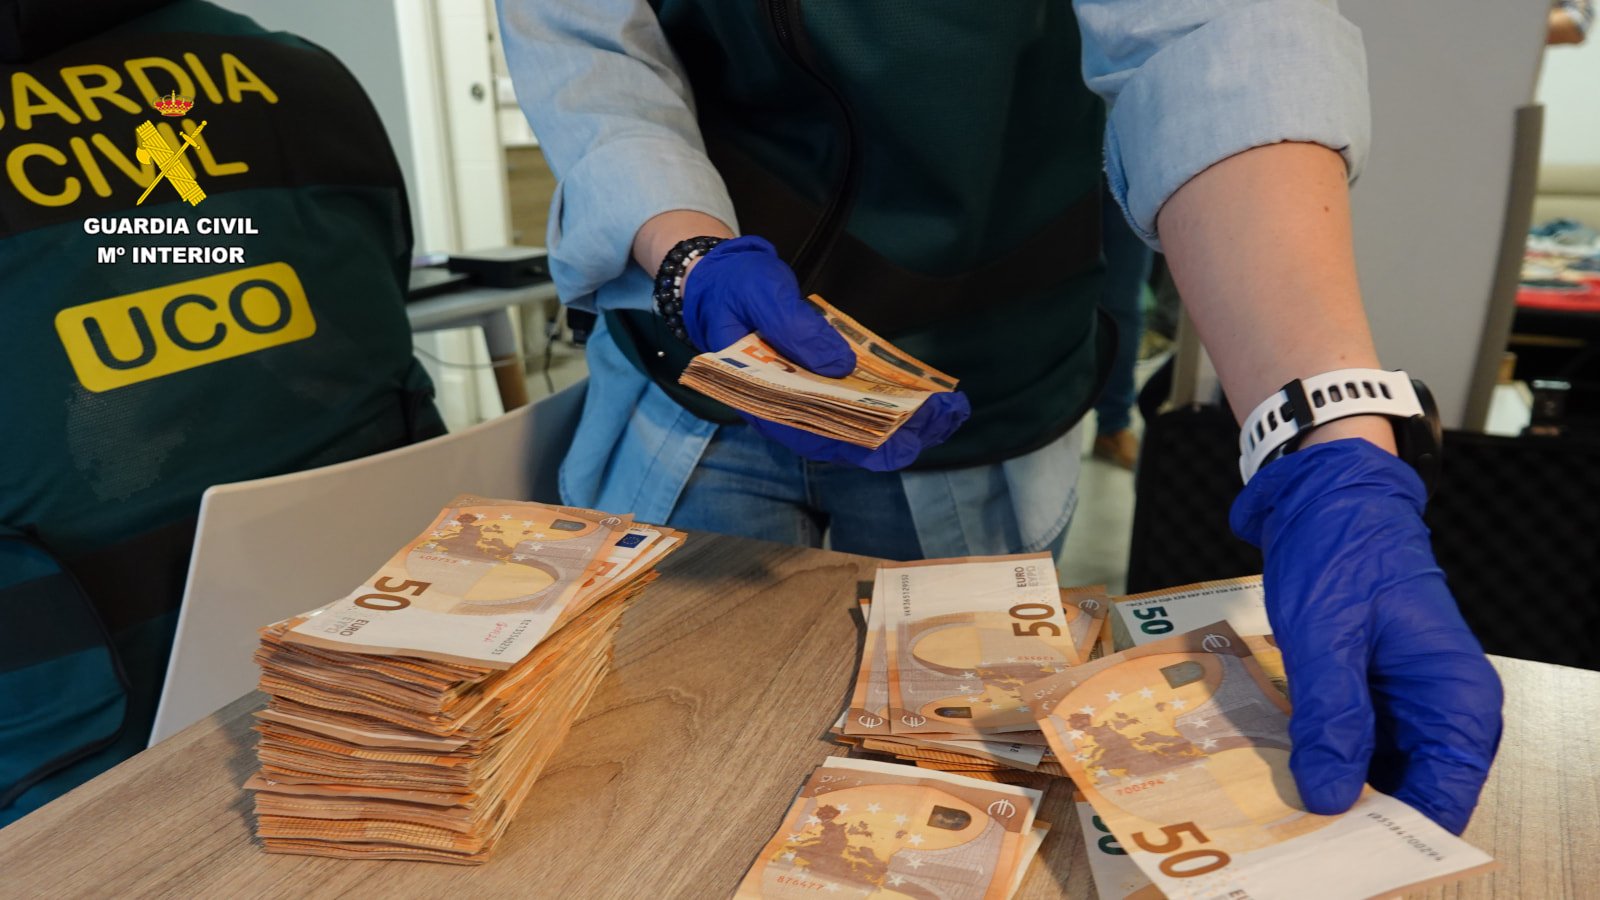
The Spanish Guardia Civil has dismantled the GXC Team, a cybercriminal operation offering AI-powered phishing kits, Android malware, and voice scams. The arrest and seizures have disrupted their global targeting of financial and e-commerce sectors. #GXCTeam #GoogleXcoder
A smishing campaign is targeting New Yorkers with fake text messages claiming to be from the Department of Taxation and Finance about an “Inflation Refund” to steal personal data. Authorities warn residents that the scam involves phishing websites that can lead to identity theft and financial fraud. #GXCTeam #InflationRefund #NYTaxFraud

Oracle has issued a security alert for a new high-severity vulnerability in its E-Business Suite, which could allow unauthorized access to sensitive data. Recent exploits have been linked to the deployment of malware payloads by suspected Cl0p-affiliated hacking groups. #CVE-2025-61884 #OracleE-BusinessSuite #Cl0p…

Daily Recap, Open-source supply-chain attacks from a North Korean APT targeting npm and Node.js SEA/Electron installers to deliver RATs and ransomware, alongside a Gladinet zero-day being actively exploited. The summary also notes polymorphic RATs, ClayRat Android spyware, BreachForums takedown, and notable data-theft incidents including Sugar Land outage and PowerSchool breach, with updates on Windows 11 EOS and GDPR findings. #Stealit #Contagious npm #ClayRat #PowerSchool #Sugar_Land #Windows11_23H2 #GNU

Threat actors are exploiting Velociraptor, a legitimate open-source DFIR tool, to facilitate ransomware operations linked to Storm-2603, a threat group using LockBit, Warlock, and Babuk ransomware. Their sophisticated tactics include exploiting SharePoint vulnerabilities, privilege escalation, and manipulating Active Directory, indicating a highly organized cybercrime operation possibly linked to Chinese state actors….

Cybersecurity firm Huntress warns of widespread SonicWall SSL VPN compromises, with attackers using valid credentials to quickly access multiple accounts. The incident coincides with SonicWall’s disclosure of a breach exposing firewall configuration backups, raising concerns about potential exploitation. #SonicWall #SSLVPN #Cyberattack #FirewallBreach…
The Socket Threat Research Team warns of ongoing North Korean cyber operations exploiting open-source npm packages to target Web3 and blockchain developers. These campaigns involve sophisticated supply chain attacks, fake personas, and malicious package impersonations linked to significant cryptocurrency theft. #NorthKoreanThreatActors #npmSupplyChain…
Daily Recap, A PoC titled fenrir breaches secure boot on MediaTek-powered devices including the Nothing Phone (2a), enabling arbitrary firmware/OS installs and trust-chain compromise; Android spyware ClayRAT masquerades as popular apps to spy on Russian users and exfiltrate data. #Fenrir #ClayRat
A 19-year-old Massachusetts man, Matthew Lane, pleaded guilty to hacking into PowerSchool’s databases, exposing sensitive data of over 60 million students and 9 million teachers. He faces a proposed seven-year prison sentence due to his repeated cybercrimes, use of sophisticated hacking techniques, and ransom demands. #PowerSchool #Cyberhacking…
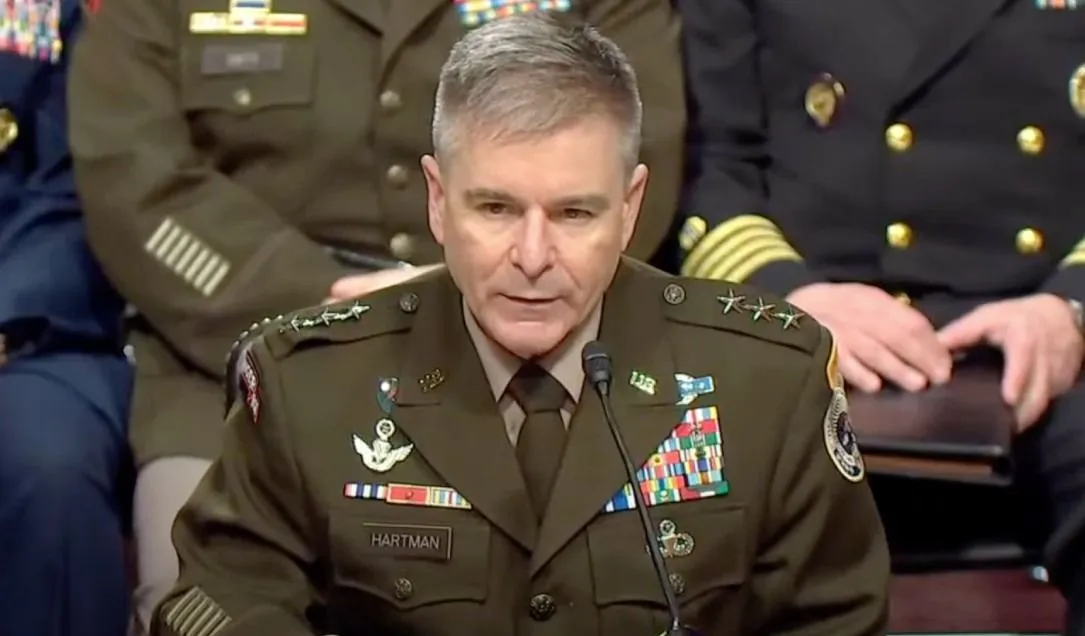
President Donald Trump has decided not to nominate Army Lt. Gen. William Hartman to lead U.S. Cyber Command and the NSA, leading to his retirement. The decision reflects internal disagreements about leadership arrangements and the ongoing leadership vacuum in critical cybersecurity agencies. #WilliamHartman #CyberCommand #NSA #DigitalDangers…
Apple is expanding and redesigning its bug bounty program, offering higher payouts and new research categories to incentivize security researchers. The new rewards aim to combat sophisticated spyware and zero-click attacks, with total payouts potentially exceeding $5 million. #Apple #BugBounty #Spyware #ZeroClickAttacks #MemoryIntegrity