
A Cisco Talos report unveils a malicious campaign linked to North Korea’s Famous Chollima group, targeting developers through fake job offers and trojanized open-source tools. The campaign leverages malware families BeaverTail and OtterCookie to steal cryptocurrency wallets, keystrokes, and sensitive data across multiple platforms. #FamousChollima #BeaverTail #OtterCookie #NPM #SupplyChainAttack…
Category: Cyber Security News

Researchers have uncovered that half of the geostationary satellite links contain unencrypted IP traffic, exposing sensitive data across various sectors. This study highlights the security vulnerabilities of satellite communications, affecting military, industrial, and commercial networks. #GEOsatellites #SatelliteTrafficProtection…
Microsoft has announced that Office 2016 and Office 2019 have reached the end of support, increasing vulnerability risks for users. They urge upgrading to supported versions like Microsoft 365 Apps or Office 2024 to maintain security and compliance. #Office2016 #Office2019 #Microsoft365 #Office2024
Microsoft successfully halted Rhysida ransomware campaigns by revoking over 200 malicious certificates used to sign fake Teams installers. The attacks employed domains mimicking Microsoft Teams to distribute Oyster malware, allowing threat actors remote access and data theft. #Rhysida #OysterMalware
Cyber threat actors exploited a recently patched vulnerability (CVE-2025-20352) in Cisco devices to deploy a Linux rootkit, gaining persistent access. The attacks targeted older Cisco switches lacking endpoint detection, using malware dubbed ‘Operation Zero Disco’ that can bypass security and move laterally within networks. #CVE-2025-20352 #OperationZeroDisco
Hackers compromised Prosper, a peer-to-peer lending platform, exposing personal data of over 17.6 million individuals. The breach involved sensitive information like Social Security numbers and addresses, though customer funds remain unaffected. #Prosper #DataBreach
Sotheby’s has experienced a data breach exposing sensitive customer information, including Social Security numbers and financial details, affecting a small number of individuals. The incident highlights ongoing cybersecurity risks faced by high-value asset institutions, with the company offering affected customers identity theft protection. #Sothebys #DataBreach

An investigation reveals a sophisticated Linux rootkit named LinkPro, utilized in targeted AWS infrastructure exploitation involving Docker and Kubernetes. The malware employs eBPF modules for stealth and communication via a “magic packet” to activate remote commands, highlighting advanced persistence and concealment techniques. #LinkPro #eBPF…
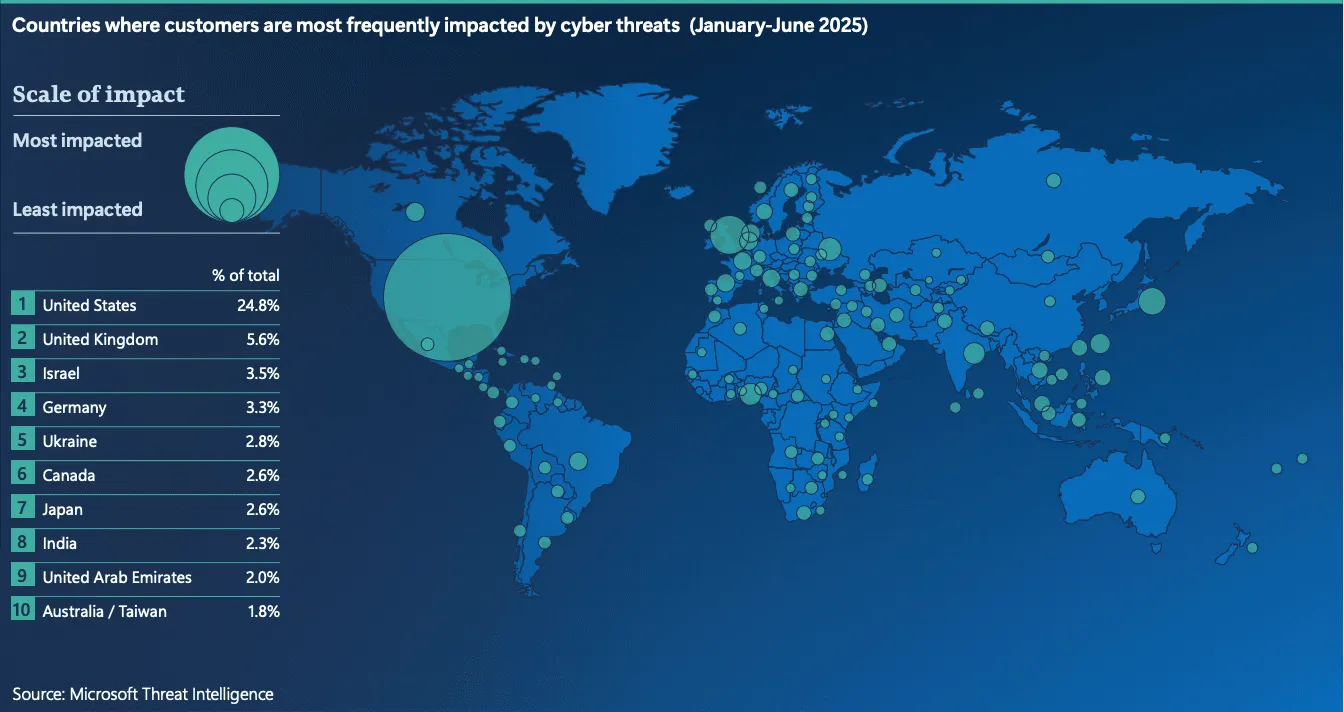
Hackers are increasingly exploiting stolen identities through password attacks, infostealers, and social engineering to breach organizations and deploy ransomware. Microsoft’s report highlights the rise in identity-based threats, targeted industries, and evolving tactics such as AV exclusion exploitation. #LummaStealer #ScatteredSpider…

Cambodia plans to repatriate 59 South Korean nationals rescued from scam centers amid diplomatic tensions after the death of a Korean student. The issue highlights the widespread transnational online scams and trafficking in Cambodia, involving authorities and regional cooperation. #SouthKoreanStudents #CambodianScamCenters…
Ring is partnering with Flock Safety to share footage with law enforcement agencies, raising privacy concerns among critics. The collaboration enables police to request user footage for investigations, potentially facilitating widespread surveillance. #Ring #FlockSafety #PrivacyConcerns…

Andrew Morton emphasizes the importance of risk-based third-party risk management (TPRM) with a focus on vendor tiering, adaptive assessments, and independent assurance reports. He advocates for a scalable, transparent approach that aligns with industry standards to produce actionable insights for leadership. #ThirdPartyRisk #ISO27001 #SOC2 #VendorManagement…
Windows 11 now supports an AI-powered Copilot digital assistant activated by the “Hey Copilot” wake word, enhancing user interaction through voice commands. Features include screen analysis with Copilot Vision and integration with Microsoft and third-party apps, but internet access remains essential for request processing. #Windows11 #CopilotVoice
North Korean hackers have innovatively used smart contracts on blockchains for malware delivery, leveraging the EtherHiding technique to evade detection and facilitate espionage activities. This development complicates campaign tracking and highlights the growing sophistication of North Korea’s cyber operations targeting cryptocurrency and web developers. #EtherHiding #JADESNOW
Modern security strategies are shifting from reactive threat detection to proactive exposure management using unified platforms. These platforms continuously discover, validate, and remediate vulnerabilities, transforming cybersecurity into a proactive defense. #UnifiedExposureManagement #BreachAndAttackSimulation