
Experian Netherlands was fined EUR 2.7 million for violating GDPR by improperly collecting and using personal data without informing or obtaining consent from individuals. The incident highlights issues related to data privacy, user awareness, and legal compliance within the realm of data analytics companies. #GDPR #ExperianNetherlands
Category: Cyber Security News
Cybercriminals are leveraging TikTok videos disguised as legitimate activation guides to spread the Aura Stealer malware and steal sensitive information. This campaign uses social engineering and PowerShell commands to infect computers and compromise user credentials. #AuraStealer #PowerShell #TikTokMalware

Europol’s Operation SIMCARTEL successfully shut down a high-level cybercrime platform that facilitated SIM farm services for global crimes like phishing and fraud. This effort led to arrests, confiscation of devices and assets, and targeted the infrastructure enabling over 49 million online accounts. #GoGetSMS #SIMfarm #Phishing #Cyberfraud…

Daily Recap, North Korea combines BeaverTail and OtterCookie into advanced JavaScript malware to steal data and cryptocurrency, while state-backed actors deploy diverse tooling including a new .NET CAPI backdoor and AI-enabled escalation techniques across Russia, China, and other regions. The update also highlights high-severity ASP.NET Core flaws, widespread data leaks such as Envoy’s Oracle E-Business breach, and SIM farm takedowns—reflecting broad, multi-vector threats and remediation efforts. #BeaverTail #OtterCookie #SilverFox #BulletproofChains #AIEscalation #Envoy #SIMFarmRaid
A new cyber campaign targets macOS developers with fake platforms like Homebrew, LogMeIn, and TradingView, delivering infostealing malware such as AMOS and Odyssey. The attackers use convincing fake sites and Terminal commands to trick users into installing malicious payloads. #AMOS #OdysseyStealer
North Korean operatives are using advanced malware strains and techniques, including blockchain-based command and control, to conduct cyber espionage, credential theft, and cryptocurrency targeting. These campaigns involve sophisticated social engineering tactics during job applications and leverage evasive malware such as BeaverTail, OtterCookie, and EtherHiding. #NorthKoreaCyberThreat #EtherHiding…
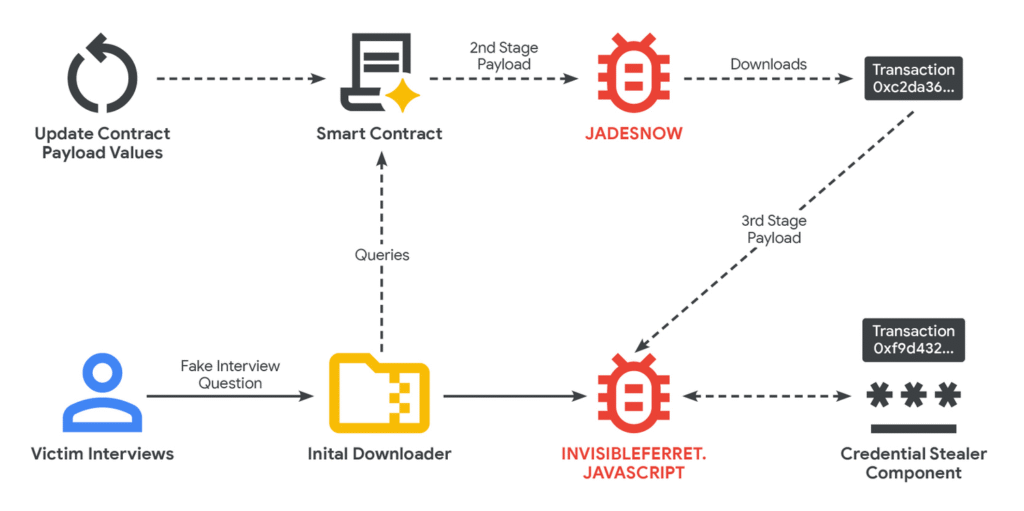
This article discusses the use of low-cost smart contracts on blockchains like Ethereum and BNB for deploying staged malware campaigns. It highlights North Korean threat actors UNC5342 and UNC5142 targeting cryptocurrency developers through social engineering and leveraging blockchain flexibility for malicious activities. #UNC5342 #EtherHiding…

A Massachusetts student was sentenced to four years in prison for hacking and extorting around $3 million from companies, including PowerSchool. The breach compromised data of over 60 million students and 9 million teachers, highlighting significant vulnerabilities in educational cybersecurity. #PowerSchool #DataBreach…

Cybersecurity researchers have identified a new campaign targeting the Russian automobile and e-commerce sectors using the CAPI Backdoor, a novel .NET malware. The attack involves phishing emails with ZIP archives and decoy documents, exploiting living-off-the-land techniques to evade detection. #CAPIBackdoor #LivingOffTheLand…

The Winos 4.0 malware family and HoldingHands RAT have expanded their targeting to Japan and Malaysia, utilizing phishing and SEO poisoning to deliver payloads. These cyberattacks are linked to the Chinese cybercrime group Silver Fox, leveraging malicious documents and sophisticated infection chains. #Winos4.0 #HoldingHandsRAT #SilverFox…
Daily Recap, Hackers stole sensitive bidding, customer and payment data from Sotheby’s and other major breaches, highlighting continued exposure across auction, marketplace, and education sectors. The report also notes critical vulnerabilities, notable malware/APT activity, and privacy concerns from surveillance partnerships and unencrypted traffic. #SothebysBreached #ProsperBreach #KearneyPublicSchools #WatchGuardVulnerable #LinkProRootkit #ChollimaOtterCookie
Envoy Air experienced a data breach involving its Oracle E-Business Suite, attributed to the Clop extortion gang exploiting a zero-day vulnerability. The incident highlights the ongoing threat posed by Clop’s zero-day exploits and data theft campaigns targeting enterprise systems. #Clop #OracleZeroDay
ConnectWise has issued security updates for its Automate platform to fix critical vulnerabilities that could allow interception and manipulation of sensitive communications. These flaws pose a significant risk as they could be exploited by threat actors to impersonate servers or modify updates, especially in on-prem environments. #CVE202511492 #CVE202511493 #ConnectWiseAutomate #AdversaryInTheMiddle

AI agents with unlimited autonomy pose significant security risks, especially as they access sensitive data and execute code without oversight. The shift toward identity-based security emphasizes the importance of managing access and safeguarding against expanding attack surfaces from automated systems and AI agents. #AIagents #IdentitySecurity…

Airlines are increasingly targeted by cybercriminals due to the valuable personal data they hold, especially passports and government IDs. Recent breaches, like the Qantas leak, highlight the ongoing threat from threat groups such as LAPSUS$ and CL0P, and the importance of proactive personal security measures. #LAPSUS$ #CL0P…