Cybersecurity researchers have uncovered a phishing campaign attributed to the Iran-linked threat group MuddyWater, targeting international organizations to gather intelligence. The attack used compromised email accounts and malware like Phoenix v4, alongside remote monitoring tools, to infiltrate high-value targets. #MuddyWater #PhoenixBackdoor…
Category: Cyber Security News

This webinar discusses the challenges of managing AI agents in enterprises, highlighting the risks of unmanaged AI identities. It offers strategies to enhance AI security without hindering business growth. #AIagents #AIsecurity #cyberrisks…

North Korean-linked threat actors, specifically the Lazarus Group, are targeting European defense and aerospace companies in a campaign called Operation Dream Job. They use social engineering and malware like ScoringMathTea and MISTPEN to steal proprietary information, with indications of efforts to enhance North Korea’s drone capabilities. #LazarusGroup #OperationDreamJob #ScoringMathTea #MISTPEN #DefenseIndustry…

A Polish politician was indicted for allegedly transferring funds illegally to purchase Pegasus spyware used for surveillance. The investigation highlights the widespread use of Pegasus to monitor opposition figures in Poland from 2017 to 2022. #NSOGroup #PegasusSpyware…

A cyber espionage campaign by the group Cavalry Werewolf targeted Russian government and industrial entities using phishing emails disguised as Kyrgyz government correspondence. The hackers deployed malware such as FoalShell and StallionRAT, expanding their reach possibly to Tajikistan and the Middle East. #CavalryWerewolf #FoalShell #StallionRAT #YoroTrooper #Kazakhstan…

Tinder is expanding its facial verification tool, Face Check, to more states to help prevent impersonation, bots, and fake accounts. The program has already shown a 60% reduction in potential malicious activity and is likely to be adopted by other apps under Match Group in 2026. #FaceCheck #Impersonation #MatchGroup…
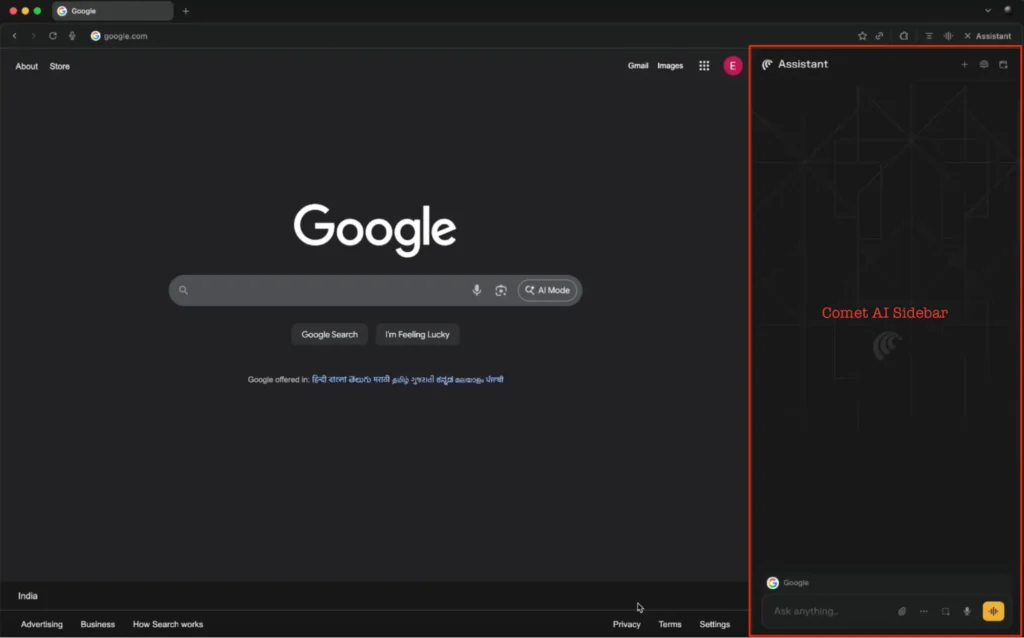
Malicious browser extensions can impersonate AI sidebar interfaces, making users vulnerable to phishing and malware attacks. These threats affect multiple browsers, including Edge, Brave, Firefox, and AI-specific browsers like ChatGPT Atlas and Perplexity’s Comet. #AI Sidebar Spoofing #Phishing #MaliciousExtensions…
Russian cybercriminals are now directly managed by the government, with the state leveraging them as geopolitical tools. International law enforcement efforts have increased pressure, leading to more targeted arrests and strategic shifts within Russia’s cybercrime ecosystem. #OperationEndgame #Conti #TrickBot #DarkCovenant…

WazirX, a major Indian cryptocurrency exchange, is resuming operations after a cyberattack in 2024 led to significant asset loss and suspension. The platform’s restart is backed by Singapore’s High Court approval of its restructuring plan, promising enhanced security and user benefits. #WazirX #CryptocurrencyRecovery…

A critical remote code execution (RCE) vulnerability has been discovered in the Rust async-tar ecosystem, affecting popular forks like tokio-tar and astral-tokio-tar. Organizations must urgently update or mitigate this flaw to prevent potential cyberattacks like file overwriting and supply-chain poisoning. #CVE‑2025‑62518 #TARmageddon…

The Microsoft Digital Defense Report 2025 highlights a shift toward financially motivated cyberattacks, with extortion and ransomware comprising over half of known motives. The report emphasizes the importance of integrated cybersecurity strategies and regional awareness, especially in Southeast Europe. #Ransomware #Cybercrime #MicrosoftDigitalDefense2025…
North Korean Lazarus hackers targeted three European defense companies involved in UAV technology using a sophisticated spear-phishing campaign called Operation DreamJob. The campaign involved tricking employees into downloading malicious files, allowing the hackers remote access to their systems, and focusing on military equipment development related to UAVs. #LazarusGroup #OperationDreamJob
OpenAI’s Atlas and Perplexity’s Comet browsers are vulnerable to AI Sidebar Spoofing attacks that could lead users to malicious websites or actions. Researchers demonstrated that attackers could inject fake sidebars to deceive users and manipulate their online activities with serious security implications. #AI Sidebar Spoofing #SquareX #CometBrowser #OpenAIBrowserAtlas #CredentialTheft
As AI agents become more autonomous, organizations face new security challenges that require a focus on identity governance and Zero Trust principles. Applying the NIST AI RMF with an identity-centric approach is essential to manage risks, oversee AI agent behavior, and ensure trustworthiness in AI-enabled systems. #AgenticAI #ZeroTrust #NISTAIrisis #TokenSecurity
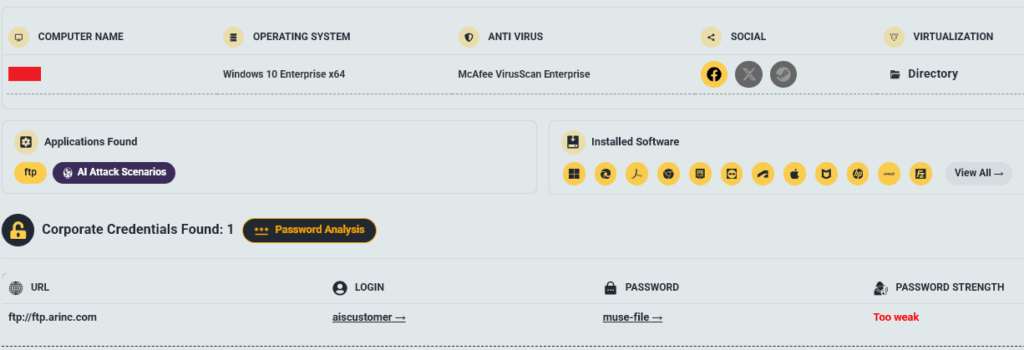
Two separate cyberattacks targeted Collins Aerospace during the week of September 15-19, 2025, involving data exfiltration by the group Everest and a ransomware incident causing major disruptions. These incidents highlight vulnerabilities from legacy credentials and simultaneous threat activities. #Everest #CollinsAerospace